- Deploy Console on ECS: Console and its monitoring container on Amazon Elastic Container Service (ECS) with Fargate, backed by a PostgreSQL database on Amazon RDS
- Deploy Gateway on ECS: a Gateway cluster on ECS with Fargate, behind a Network Load Balancer (NLB)
- Deploy Console with AWS CloudFormation: the AWS Marketplace listing
While this guide will help you get started, you may need to make additional configurations to ensure your deployment is production-ready.
Deploy Console on ECS
Before you start, make sure that you’ve already created a new Virtual Private Cloud (VPC) with a public subnet and two private subnets (needed for RDS) or are planning to use an existing one.This is important to ensure that your environment is secure and isolated. We also strongly recommend avoiding the use of the default VPC, as it can pose a security risk due to its common configuration.
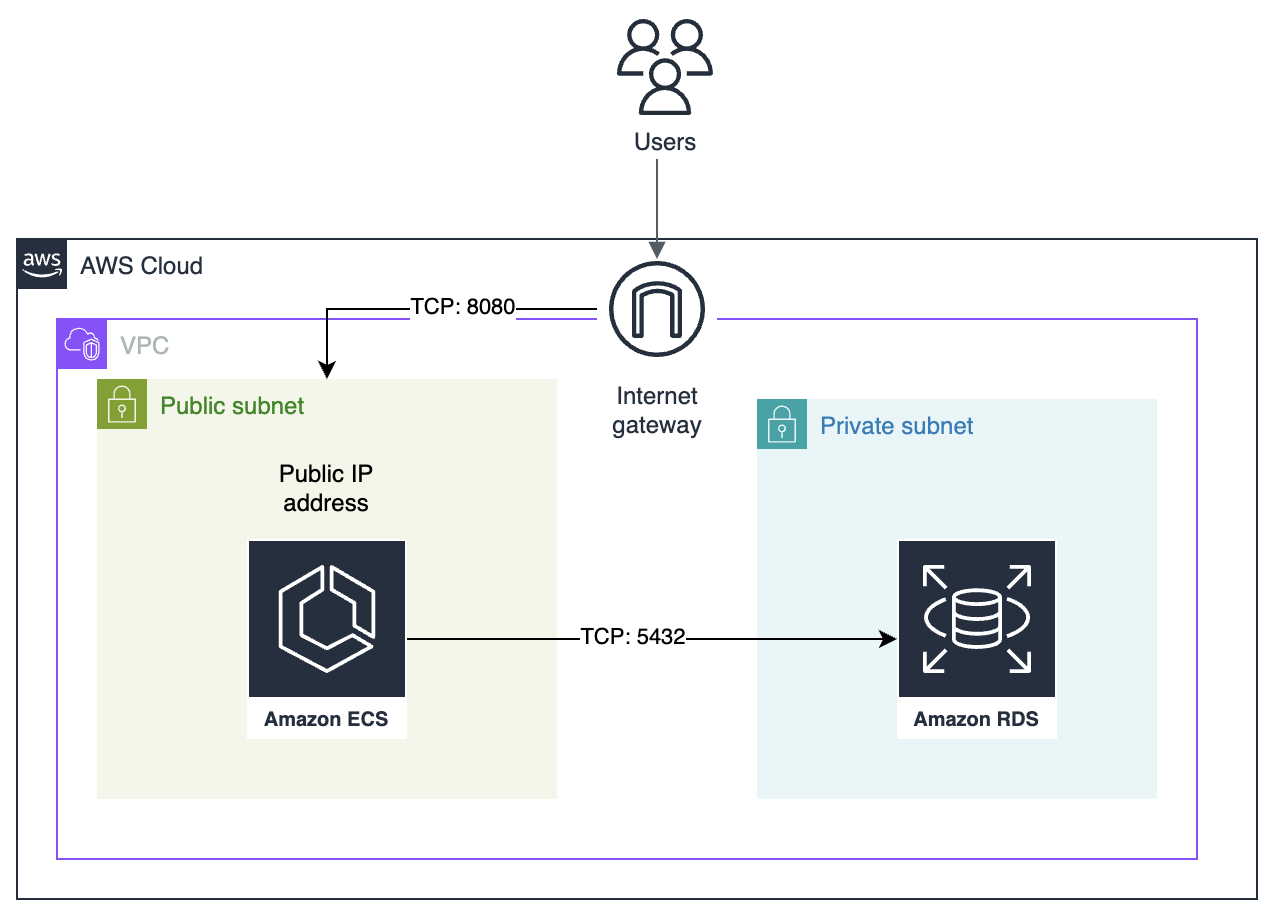
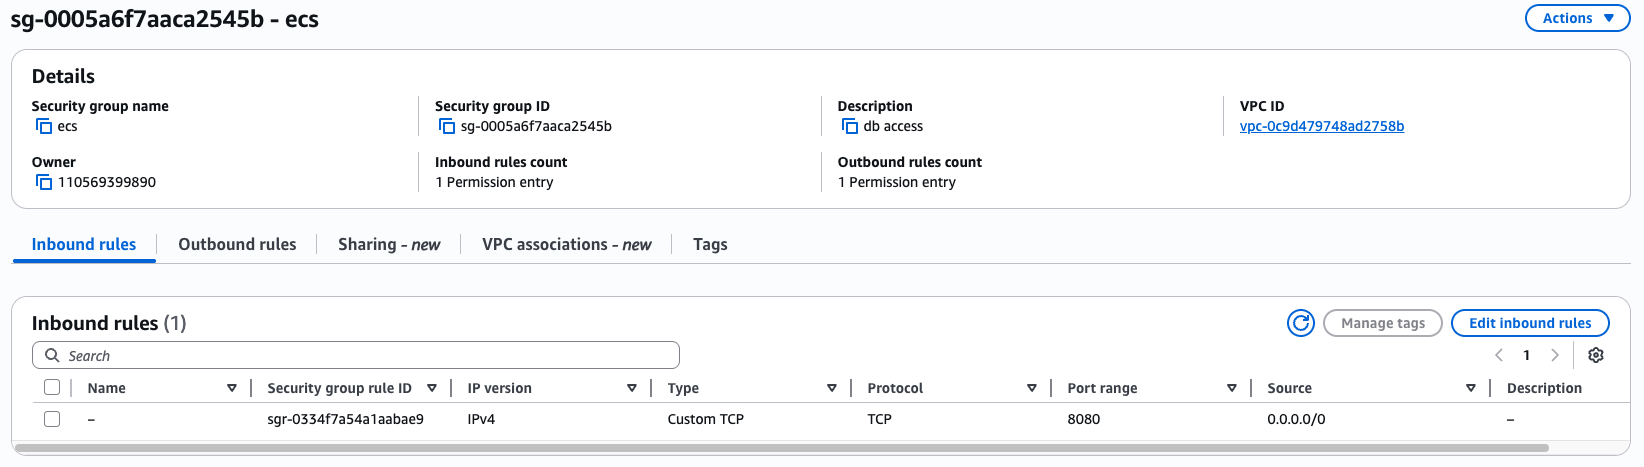
8080 from the internet to give Conduktor Console access.
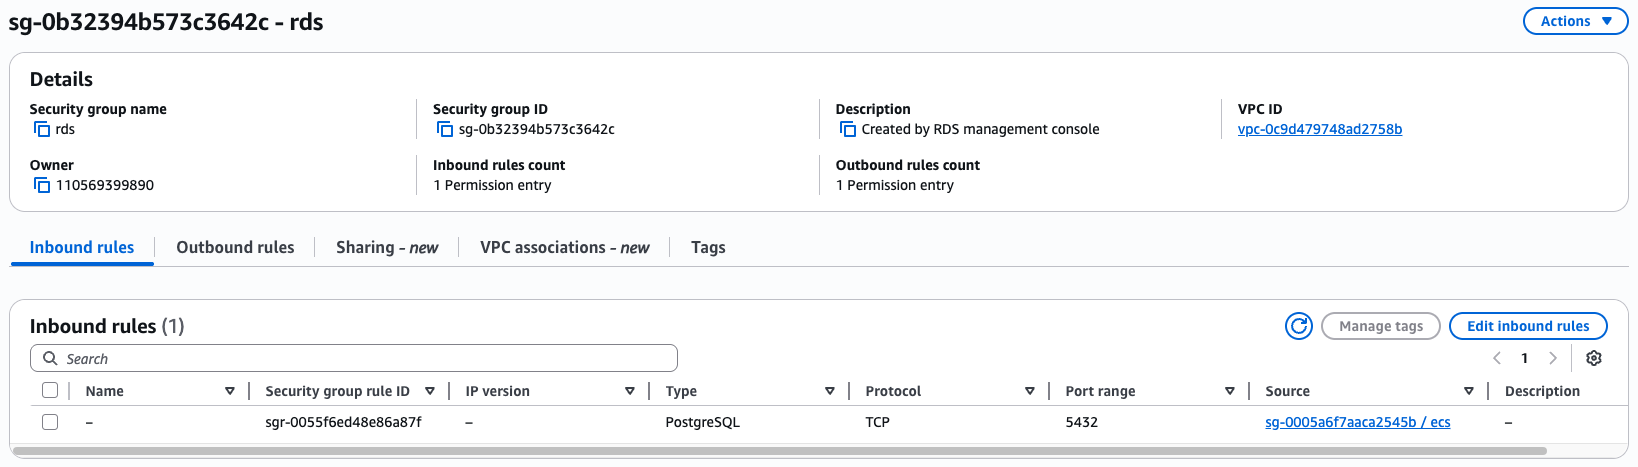
5432 from the public security group to give Conduktor Console access to the RDS database.
Step 1: Create a PostgreSQL database via Amazon RDS
You can skip this step if you already have an RDS database running you want to use.
- Select PostgreSQL
- In the Template section, select Free Tier if you are just evaluating Conduktor.
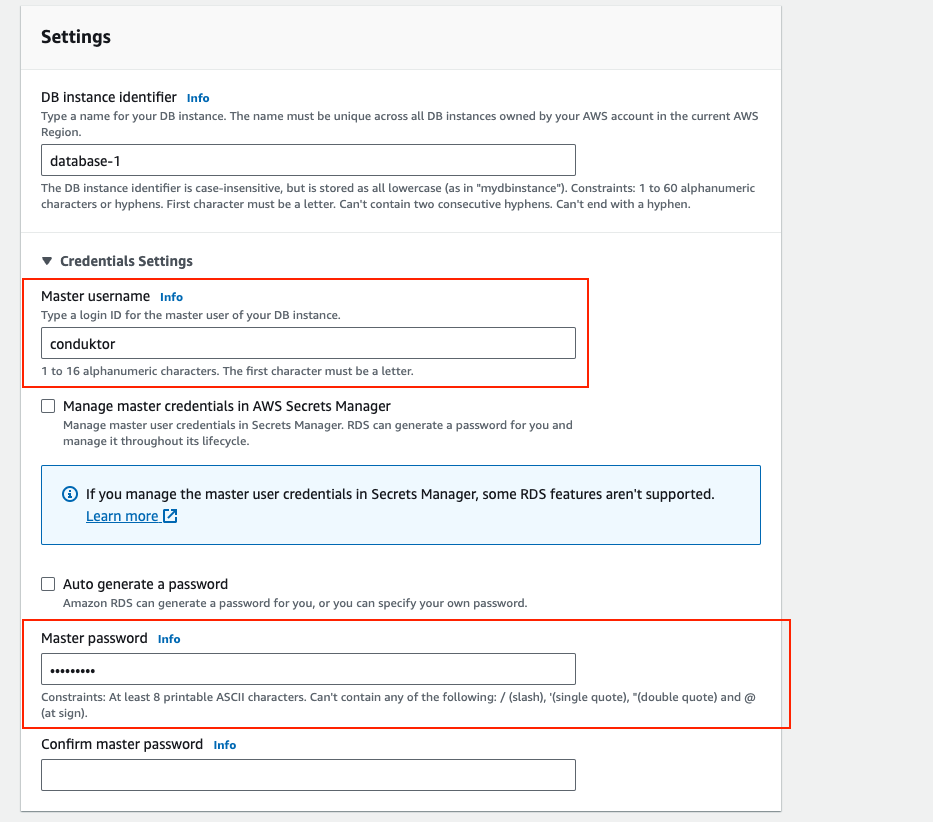
- Master username:
conduktor - Master password:
change_me
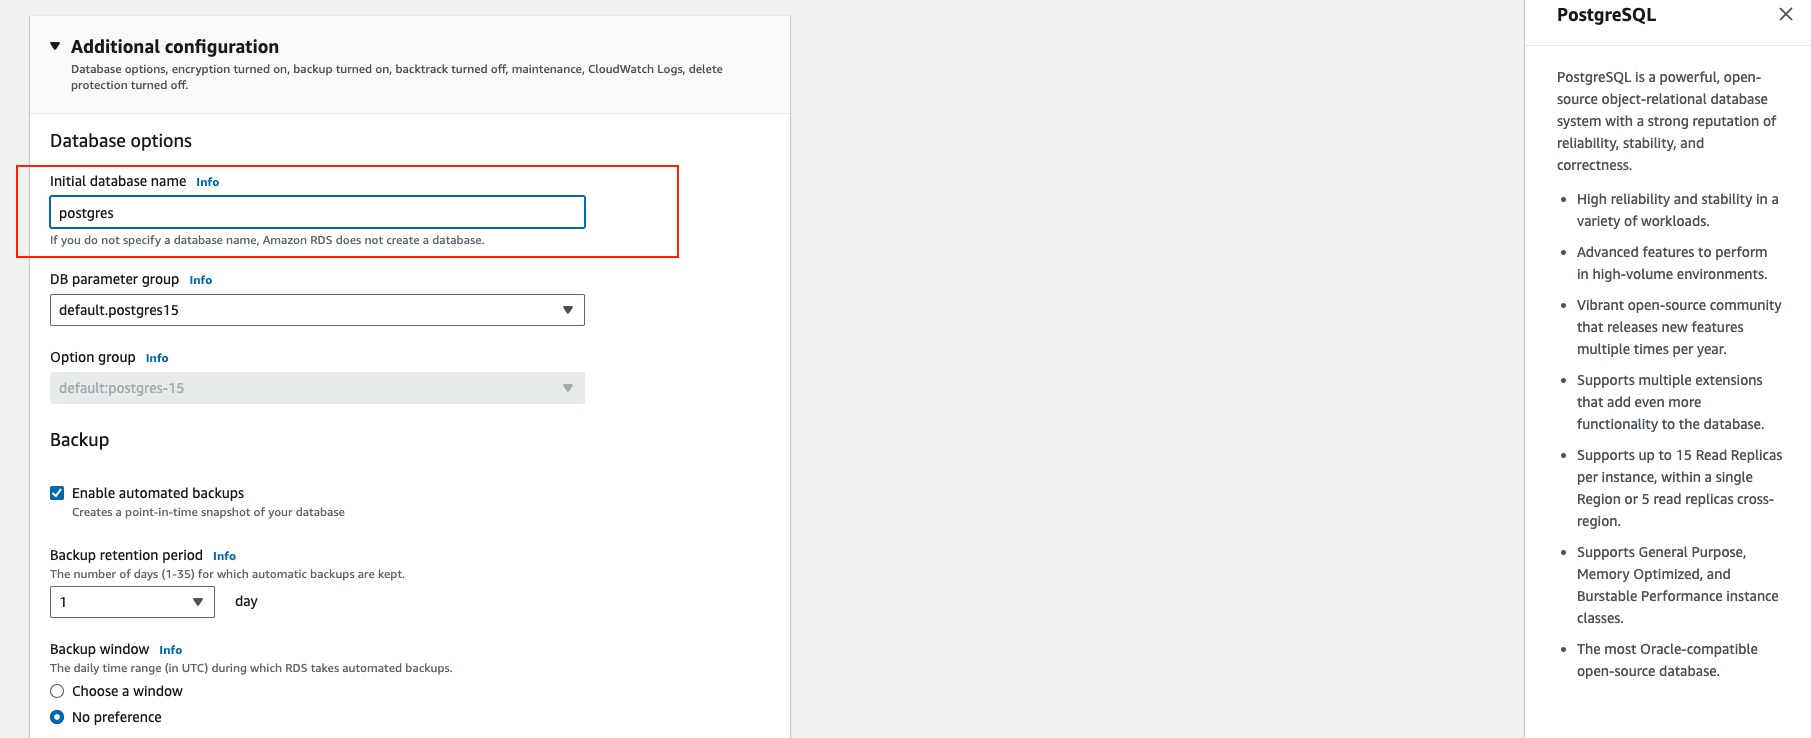
- Initial database name:
postgres
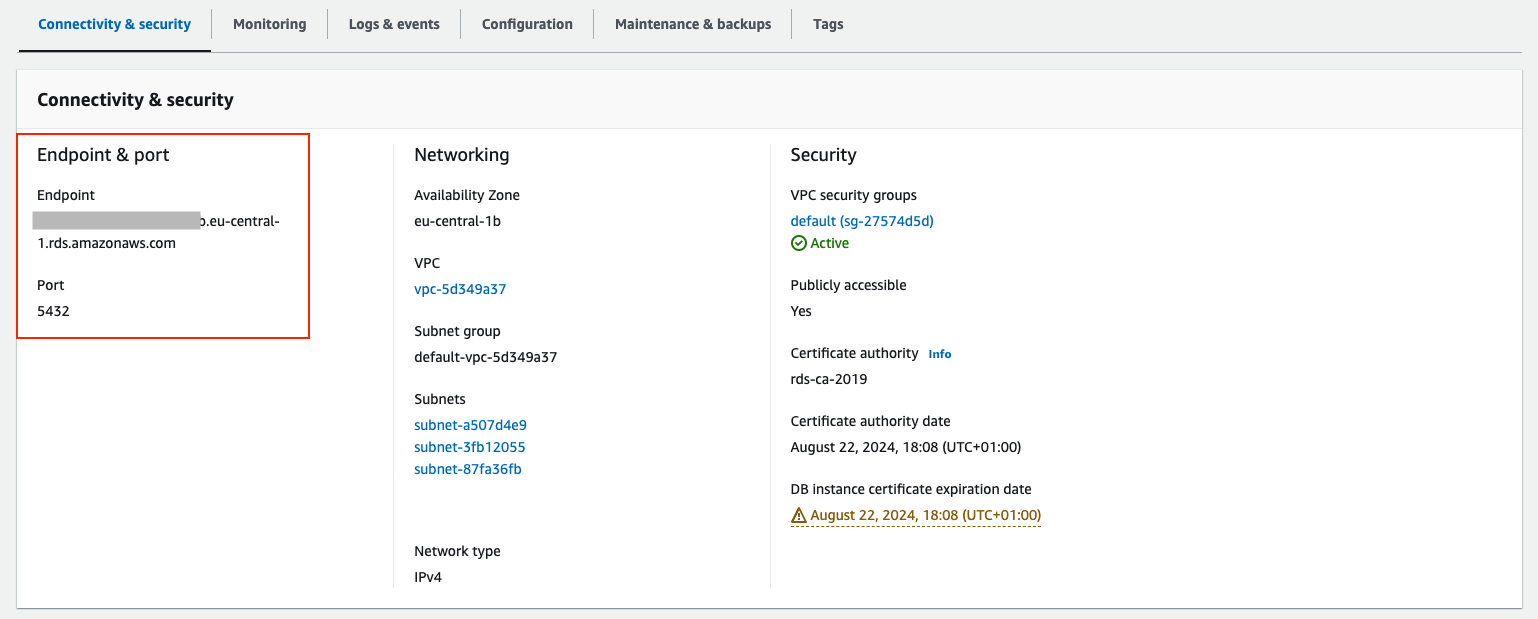
conduktor.xxx.eu-central-1.rds.amazonaws.com.
Step 2: Create a new Task definition on ECS
Now that we have our database, it’s time to deploy Conduktor using Docker containers and ECS (Amazon Elastic Container Service). Go to Amazon Elastic Container Service:- Select Task Definitions
- Click on Create new task definition
- Define the ECS family name as
conduktor, this will be useful to update our deployment with newer versions of Conduktor. - Specify the infrastructure requirements relevant to your deployment. As per system requirements, we recommend a minimum of 2x CPU cores and 4GB of RAM.
Step 2.1: Add the core console container
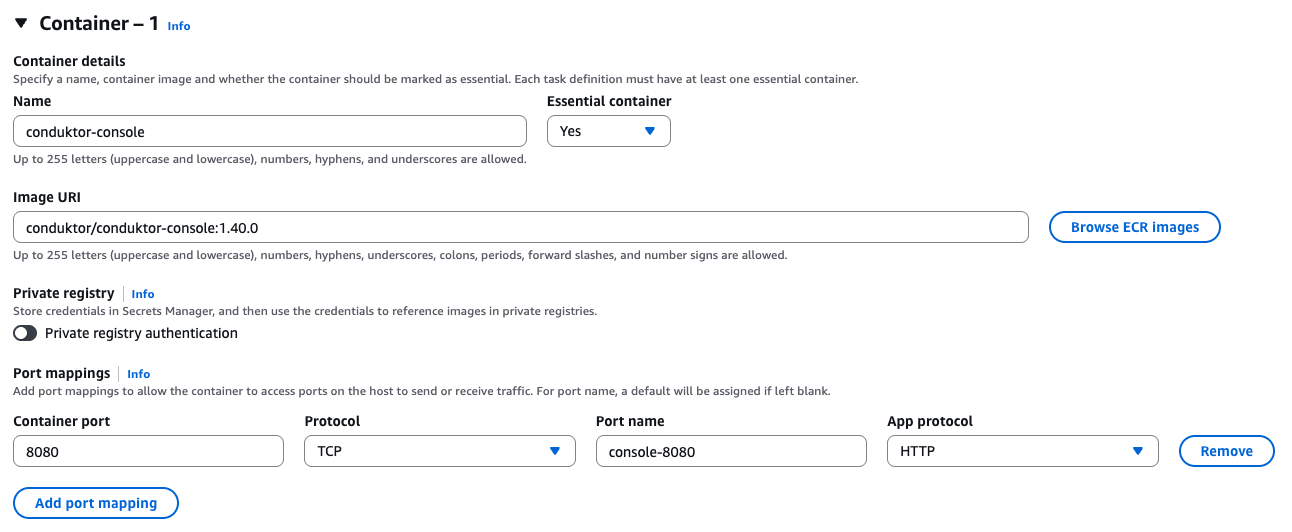
In the Container Details section:- Define the name of the container to
conduktor-console - Specify the Image URI and version for Conduktor Console. You should use the most recent major/minor version. E.g.:
conduktor/conduktor-console:<tag>. - Add a Port mapping on 8080. This is the port of the UI of Conduktor Console.
CDK_ADMIN_EMAIL: yourname@yourcompany.comCDK_ADMIN_PASSWORD: testP4ss!CDK_DATABASE_HOST: the endpoint you retrieved earlier, like conduktor-xxx.yyy.eu-central-1.rds.amazonaws.comCDK_DATABASE_NAME: postgresCDK_DATABASE_PASSWORD: change_meCDK_DATABASE_PORT: 5432CDK_DATABASE_USERNAME: conduktorCDK_MONITORING_ALERT-MANAGER-URL: http://localhost:9009/CDK_MONITORING_CALLBACK-URL: http://localhost:8080/monitoring/api/CDK_MONITORING_CORTEX-URL: http://localhost:9009/CDK_MONITORING_NOTIFICATIONS-CALLBACK-URL: http://localhost:8080CDK_LICENSE: Enterprise license key (Exclude if you are using Free)
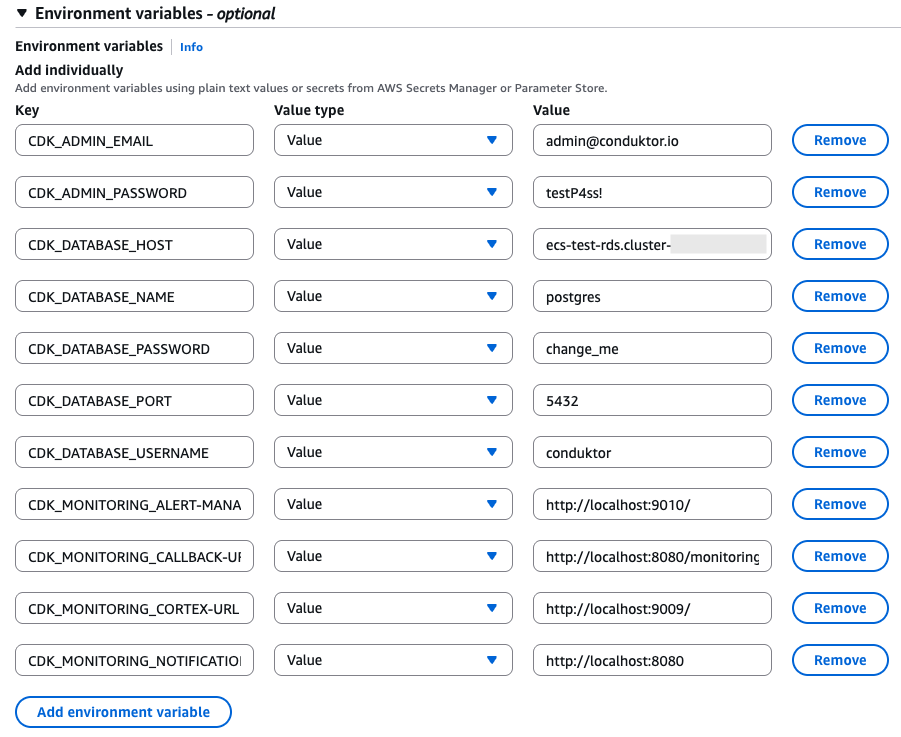
You can also add your Kafka cluster, schema registry, Kafka Connect and ksqlDB configurations as environment variables.If you’re just getting started, we recommend using the Console UI wizard instead.
Step 2.2: Add the Conduktor Cortex monitoring image
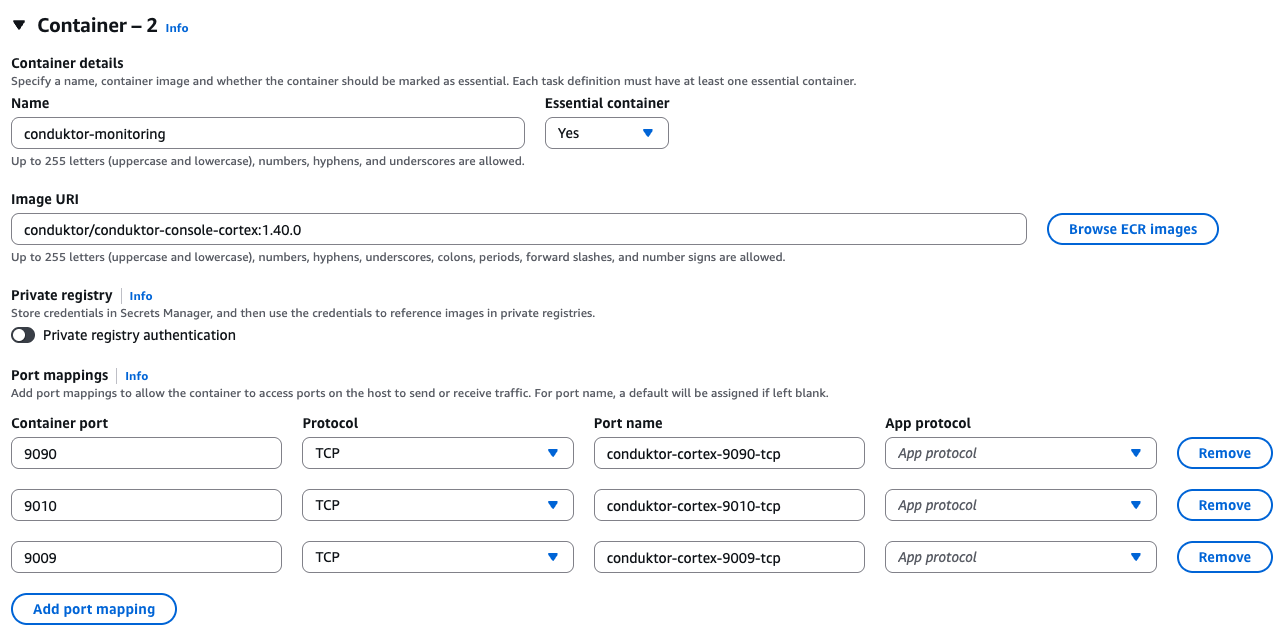
Under your first container definition, select + Add container so we can also specify the docker image required to get monitoring benefits inside Conduktor. In the Container Details section:- Define the name of the container to
conduktor-monitoring - Specify the Image URI and version for conduktor monitoring. You should use the most recent major/minor version. E.g:.
conduktor/conduktor-console-cortex:<tag>.
- 9090 | TCP | conduktor-cortex-9090-tcp
- 9009 | TCP | conduktor-cortex-9009-tcp
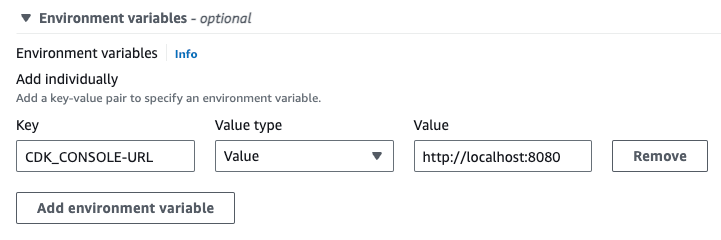
CDK_CONSOLE-URL: http://localhost:8080

Step 3: Create an ECS cluster and setup Conduktor service
We created a task definition, but it’s still just a “template”. Now, we need a cluster to deploy it. We’ll use ECS with Fargate. Go to Settings > Clusters and create a cluster (use the default options):- Name: conduktor-ecs
- In the Infrastructure section, make sure AWS Fargate (serverless) is selected (default) Create the cluster, it might take a few seconds.
- Click on your new cluster
conduktor-ecs - Create a new Service
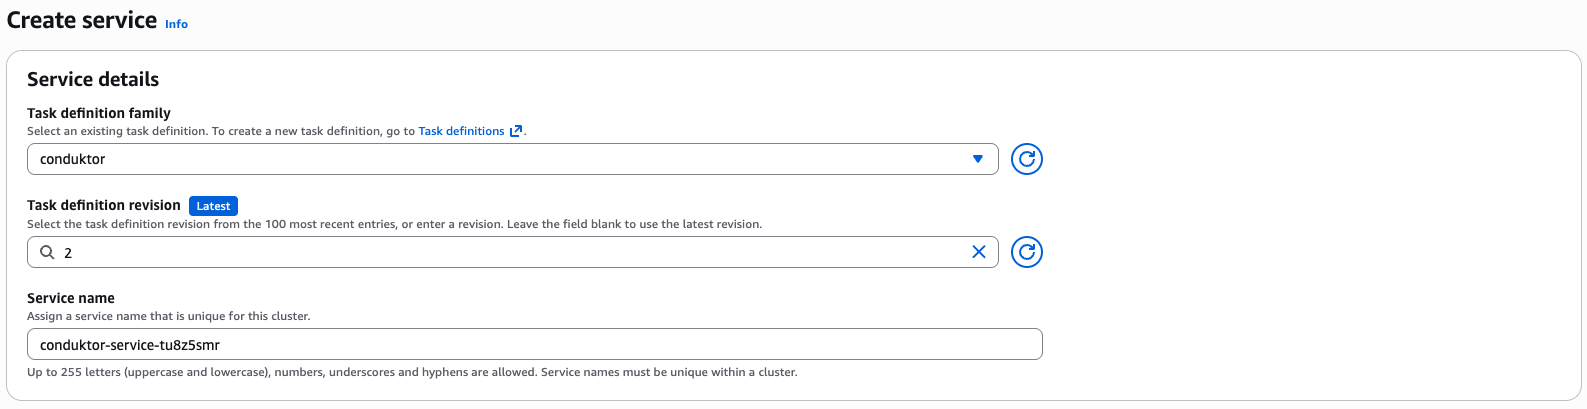
- In the Service details, Family dropdown select our task definition
conduktor. - Assign a unique name like Console to be able to identify it properly later on
- Leave the Environment section default which uses Fargate.
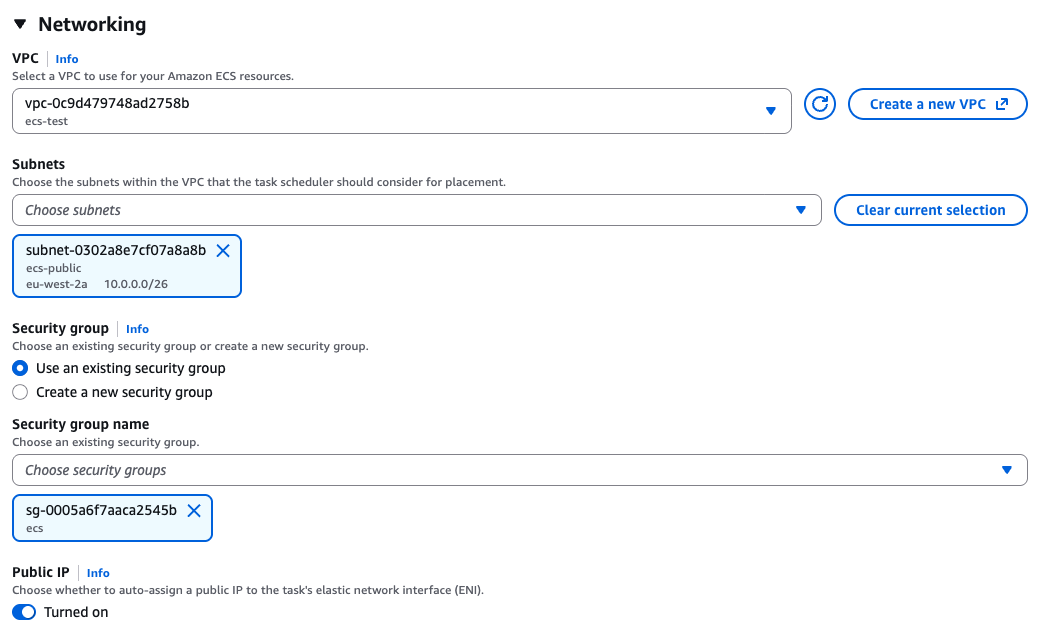
- In the Networking tab make sure to use the correct VPC and have it placed within the public subnet. Ensure that Public IP is enabled to give access to Console.
- Click Create in the bottom right corner.
Step 4: Access Conduktor and configure Kafka Clusters
From within the Services > Tasks screen, find the Container and navigate to the Network bindings tab.
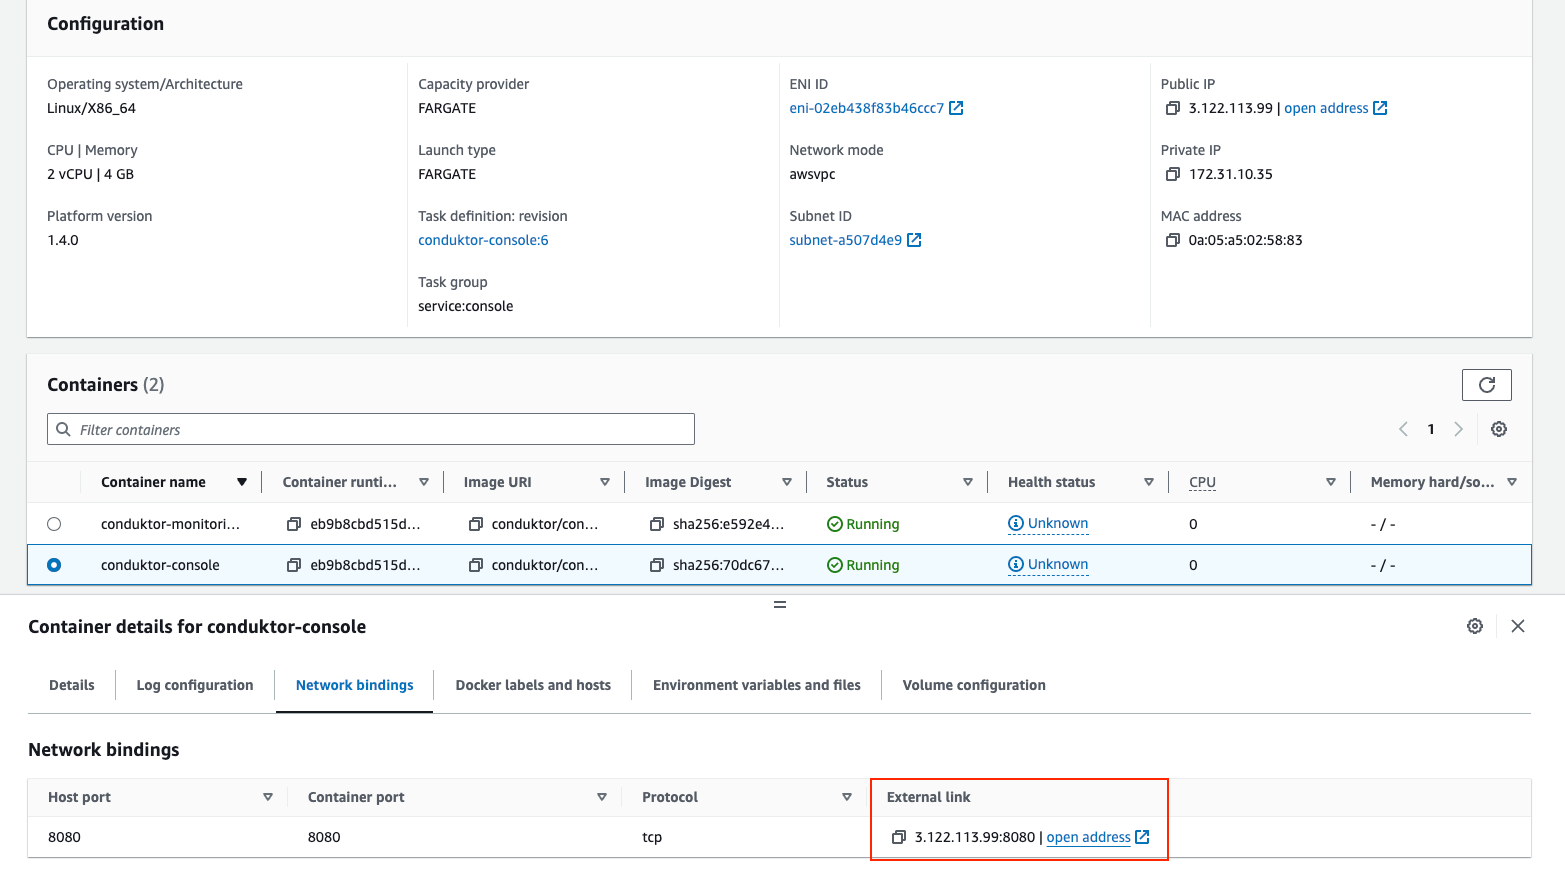
3.122.113.99:8080.
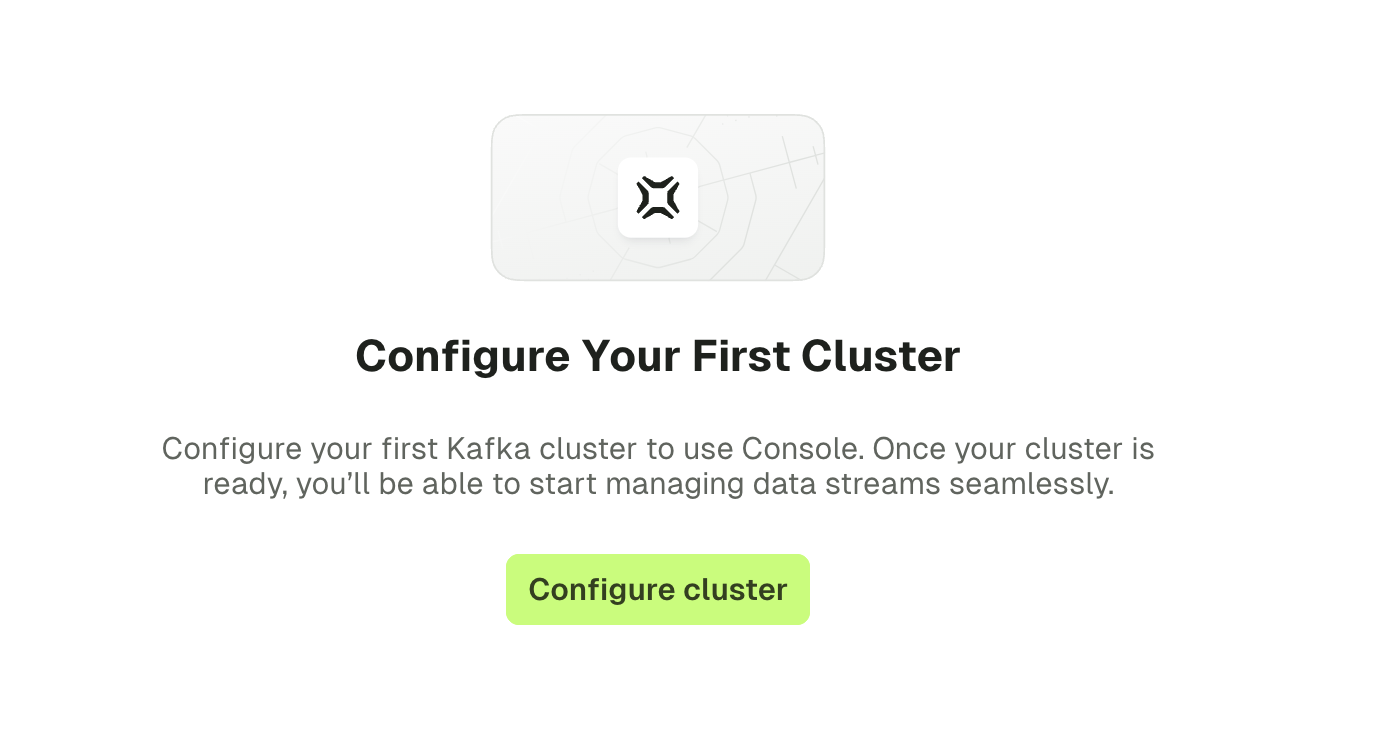
You can now log in as admin with the credentials previously defined in the environment variables, e.g. yourname@yourcompany.com / testP4ss!.
Step 5: Onboard your team
Now that you have an up-and-running deployment of Console, it’s time to invite your team!- Configure SSO to easily onboard users
- Configure local users, if you are not using SSO
Troubleshoot
Can't access database or Console
Can't access database or Console
You may need to add inbound rules.
For example, in the security group attached to the console service, ensure there is an inbound rule (TCP) for port 8080. In the security group attached to the RDS instance, ensure an inbound rule (Type = PostgreSQL) for port 5432.
For example, in the security group attached to the console service, ensure there is an inbound rule (TCP) for port 8080. In the security group attached to the RDS instance, ensure an inbound rule (Type = PostgreSQL) for port 5432.
Deploy Gateway on ECS
This section deploys a Gateway cluster of three Fargate tasks behind a Network Load Balancer. Clients connect withSASL_SSL through a single listener that uses Server Name Indication (SNI) routing, so the NLB only needs one port:
- Clients connect to
bootstrap-main.gateway.example.com:9092. A wildcard DNS record sends every*.gateway.example.comhostname to the NLB. - The NLB forwards TCP to any Gateway task without terminating TLS. Gateway reads the hostname from the TLS handshake and routes the request to the right broker.
- Gateway’s internal load balancing is off, so every task serves every broker and the NLB spreads connections across them.
gateway.example.com with a domain you control. Before you start, make sure you have:
- a VPC with private subnets in at least two Availability Zones, with outbound access to your Kafka cluster, Docker Hub, AWS Secrets Manager and Amazon CloudWatch Logs (through a NAT gateway or VPC endpoints)
- a Kafka cluster, such as Amazon MSK, and a Kafka user for Gateway
- a Route 53 hosted zone for your domain
- a Gateway license key
- an ECS cluster with Fargate, such as the
conduktor-ecscluster from the Console section
Step 1: Create the keystore
Gateway terminates TLS, so it needs a certificate whose Subject Alternative Names (SANs) cover the bootstrap and broker hostnames. A wildcard SAN covers all of them:Step 2: Store the keystore and secrets in Secrets Manager
Fargate can’t mount a file from your machine, so store the keystore as a binary secret. A container in the task writes it to disk before Gateway starts (see step 4).gateway-secrets.json
Step 3: Create the IAM roles and security groups
The task definition uses two AWS Identity and Access Management (IAM) roles. Both trustecs-tasks.amazonaws.com.
Create two security groups in your VPC:
Step 4: Register the task definition
The task runs two containers:fetch-tlsuses the AWS CLI image to write the keystore from Secrets Manager to a volume shared by the task, then exitsgatewaystarts oncefetch-tlshas succeeded and reads the keystore from the shared volume
Save the task definition as
gateway-task.json, replacing the values in angle brackets:
gateway-task.json
stopTimeout gives open Kafka connections up to 120 seconds, the Fargate maximum, to close when ECS stops a task. If your Kafka cluster uses a private certificate authority, store its truststore the same way as the keystore and set KAFKA_SSL_TRUSTSTORE_LOCATION.
Register the task definition:
Step 5: Create the Network Load Balancer
Create a target group that sends traffic to port 9092 and checks Gateway’s health on the admin API:--scheme internal if all your clients are inside the VPC or a connected network:
A record named *.gateway.example.com as an alias to the NLB.
Step 6: Create the ECS service
Run three tasks across your private subnets, registered with the target group:Step 7: Check the deployment
When the service is stable, every target ishealthy:
/ecs/conduktor-gateway CloudWatch log group. The fetch-tls stream shows keystore errors and the gateway stream shows Gateway’s startup.
Step 8: Connect clients and Console
-
Create a service account for each client and give it ACLs. Clients use
bootstrap-main.gateway.example.com:9092as their bootstrap server. -
Add Gateway to Console as a Kafka cluster. To use the Gateway provider, Console also needs a stable address for the admin API on port 8888. Create a target group on port 8888 (
--target-type ip, same health check as above) and a TCP listener on 8888 on an internal NLB, then attach it to the service alongside the first target group:
--force-new-deployment.
Before you go live, review secure Gateway before going live, including HTTPS and authentication for the admin API.
Deploy Console with AWS CloudFormation
You can deploy Console using AWS CloudFormation . This guide contains a brief overview of the marketplace listing architecture followed by the steps on how to deploy Console in your AWS environment with all the mandatory dependencies. It will deploy Conduktor as a Docker container on an ECS service with Fargate and configure it alongside a PostgreSQL database via RDS.This Conduktor marketplace offering is Community Edition and this guide is intended to help you get started. Additional configurations might be required to ensure your deployment is production ready.
In this configuration, all the resources are on a public subnet. However, the DB instance is available on both private and public subnets. Keep this in mind as part of any security concerns for the database.
Deployment steps
- Visit the Marketplace listing page .
-
Select
View purchase options.
-
Accept the terms of service.
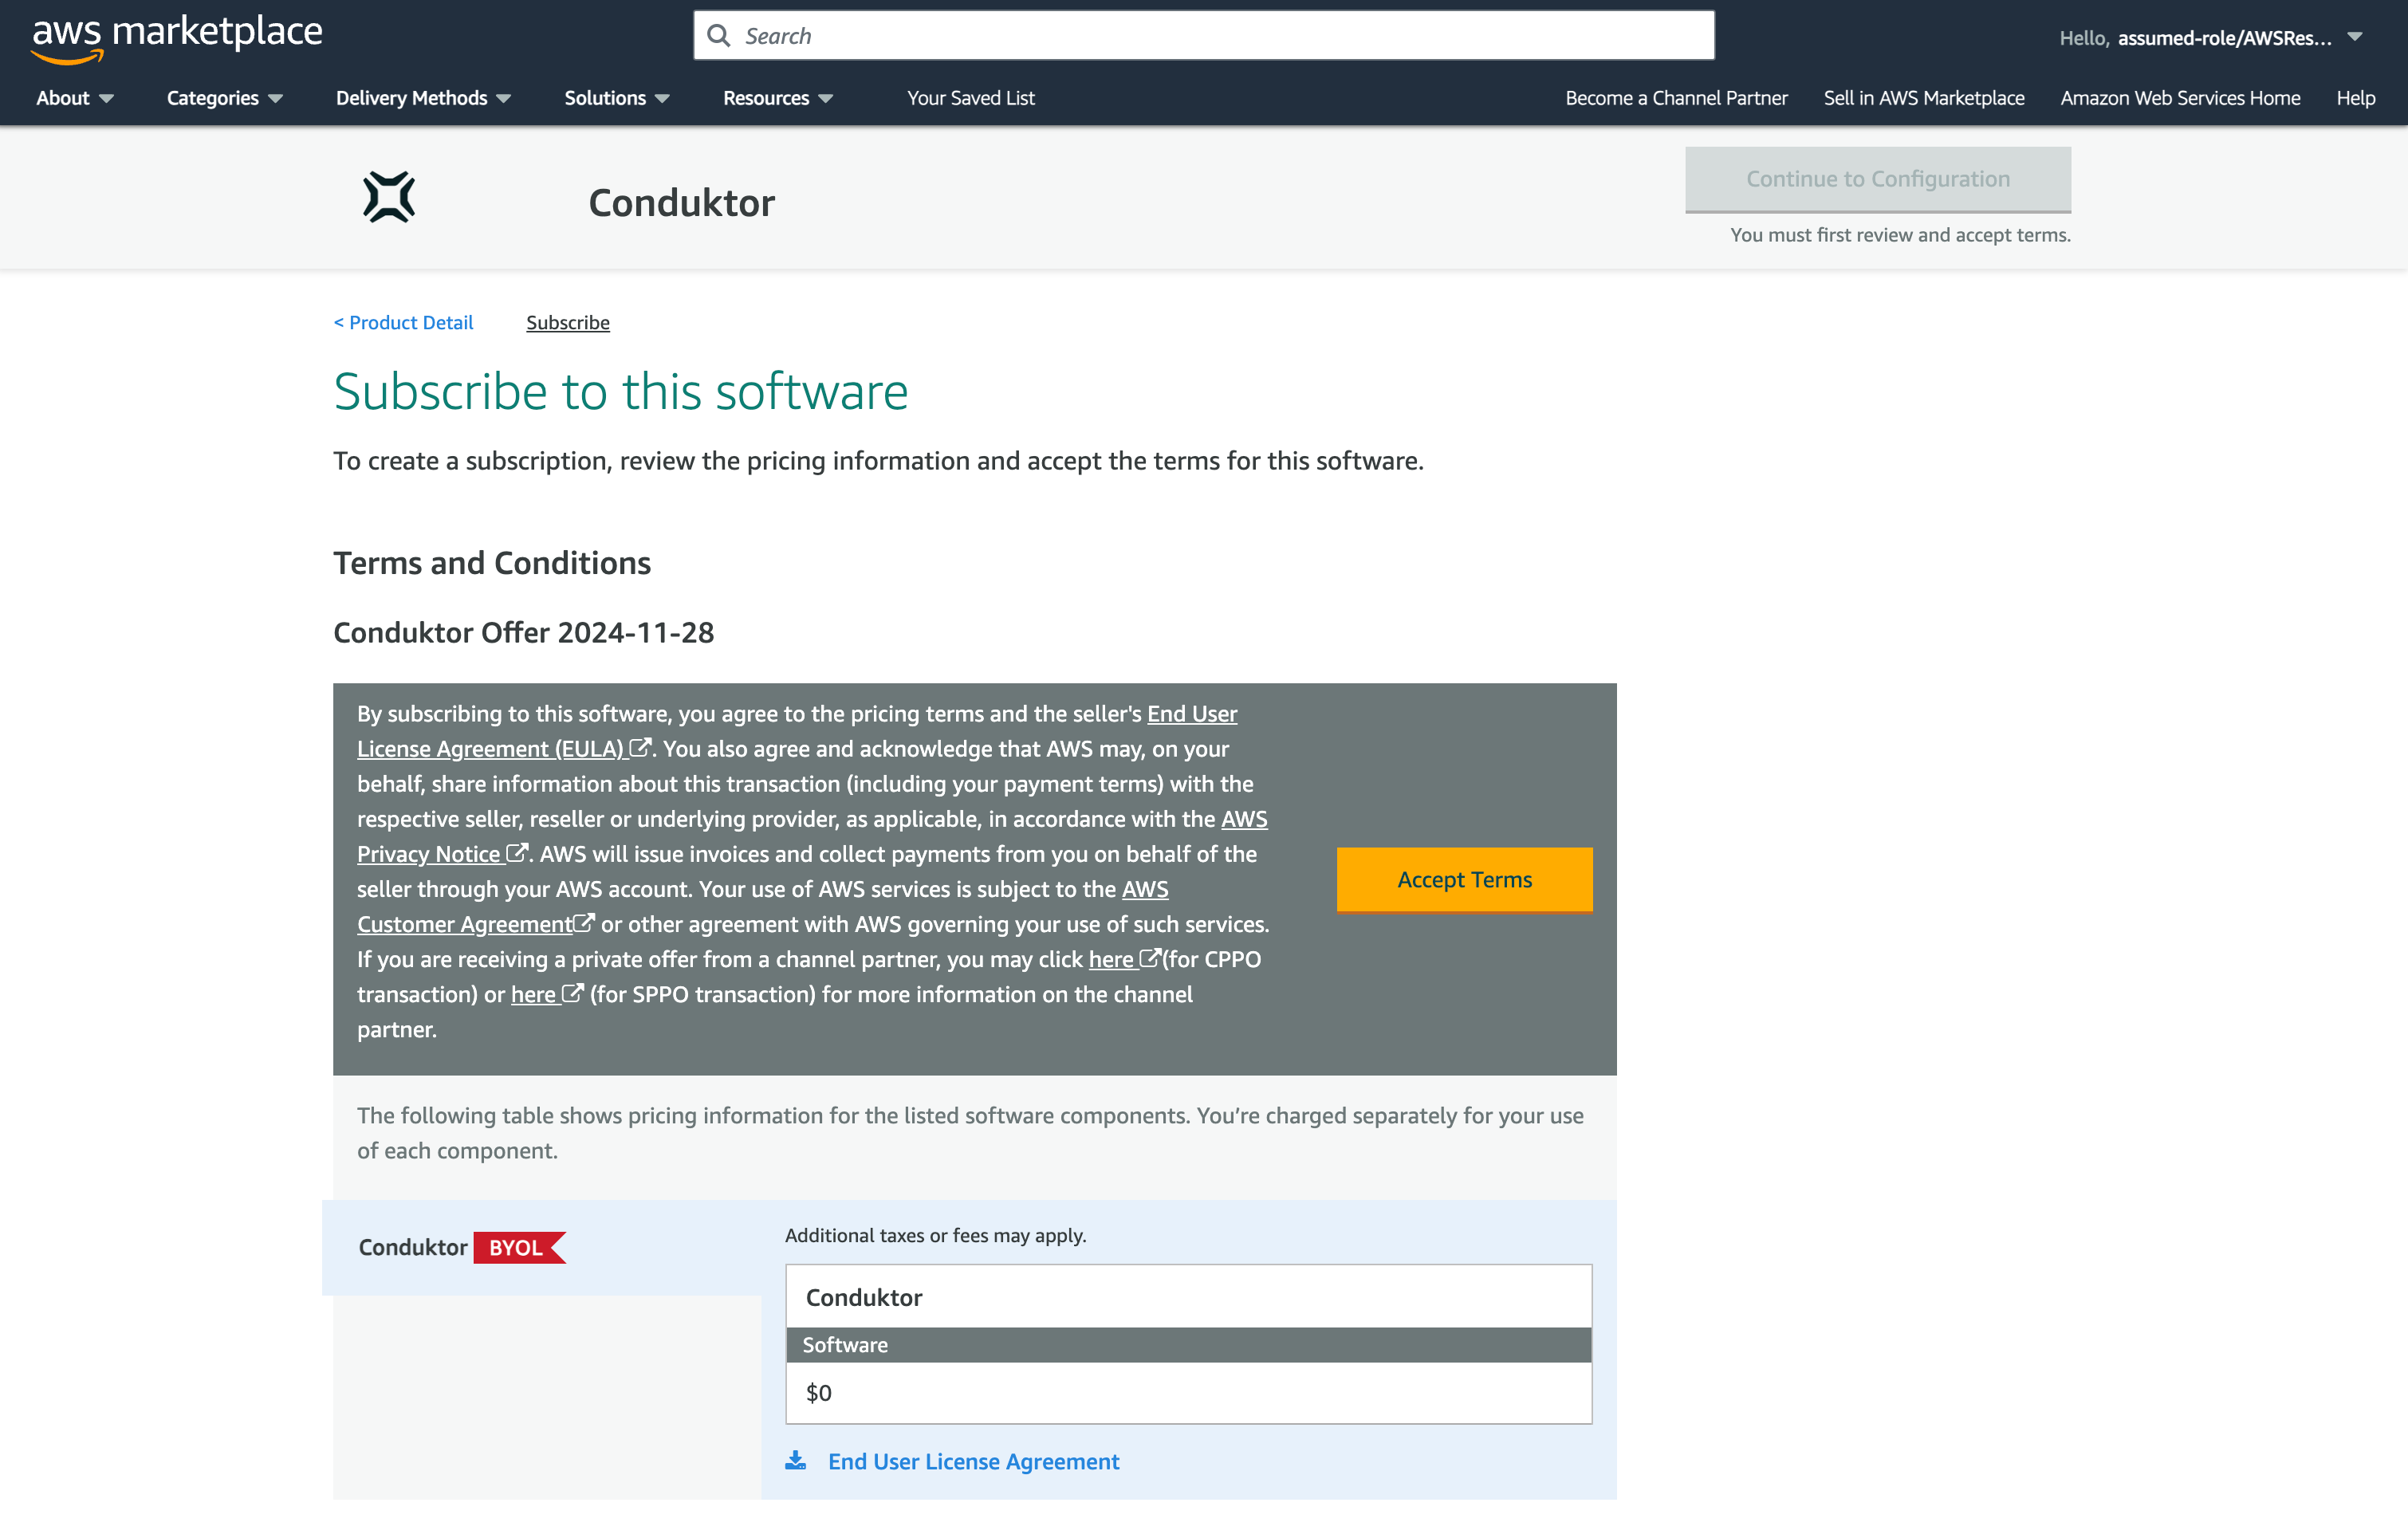
-
Select
Continue to Configuration.
-
Continue to Launch. There is only one supported Software Version and fulfillment option available.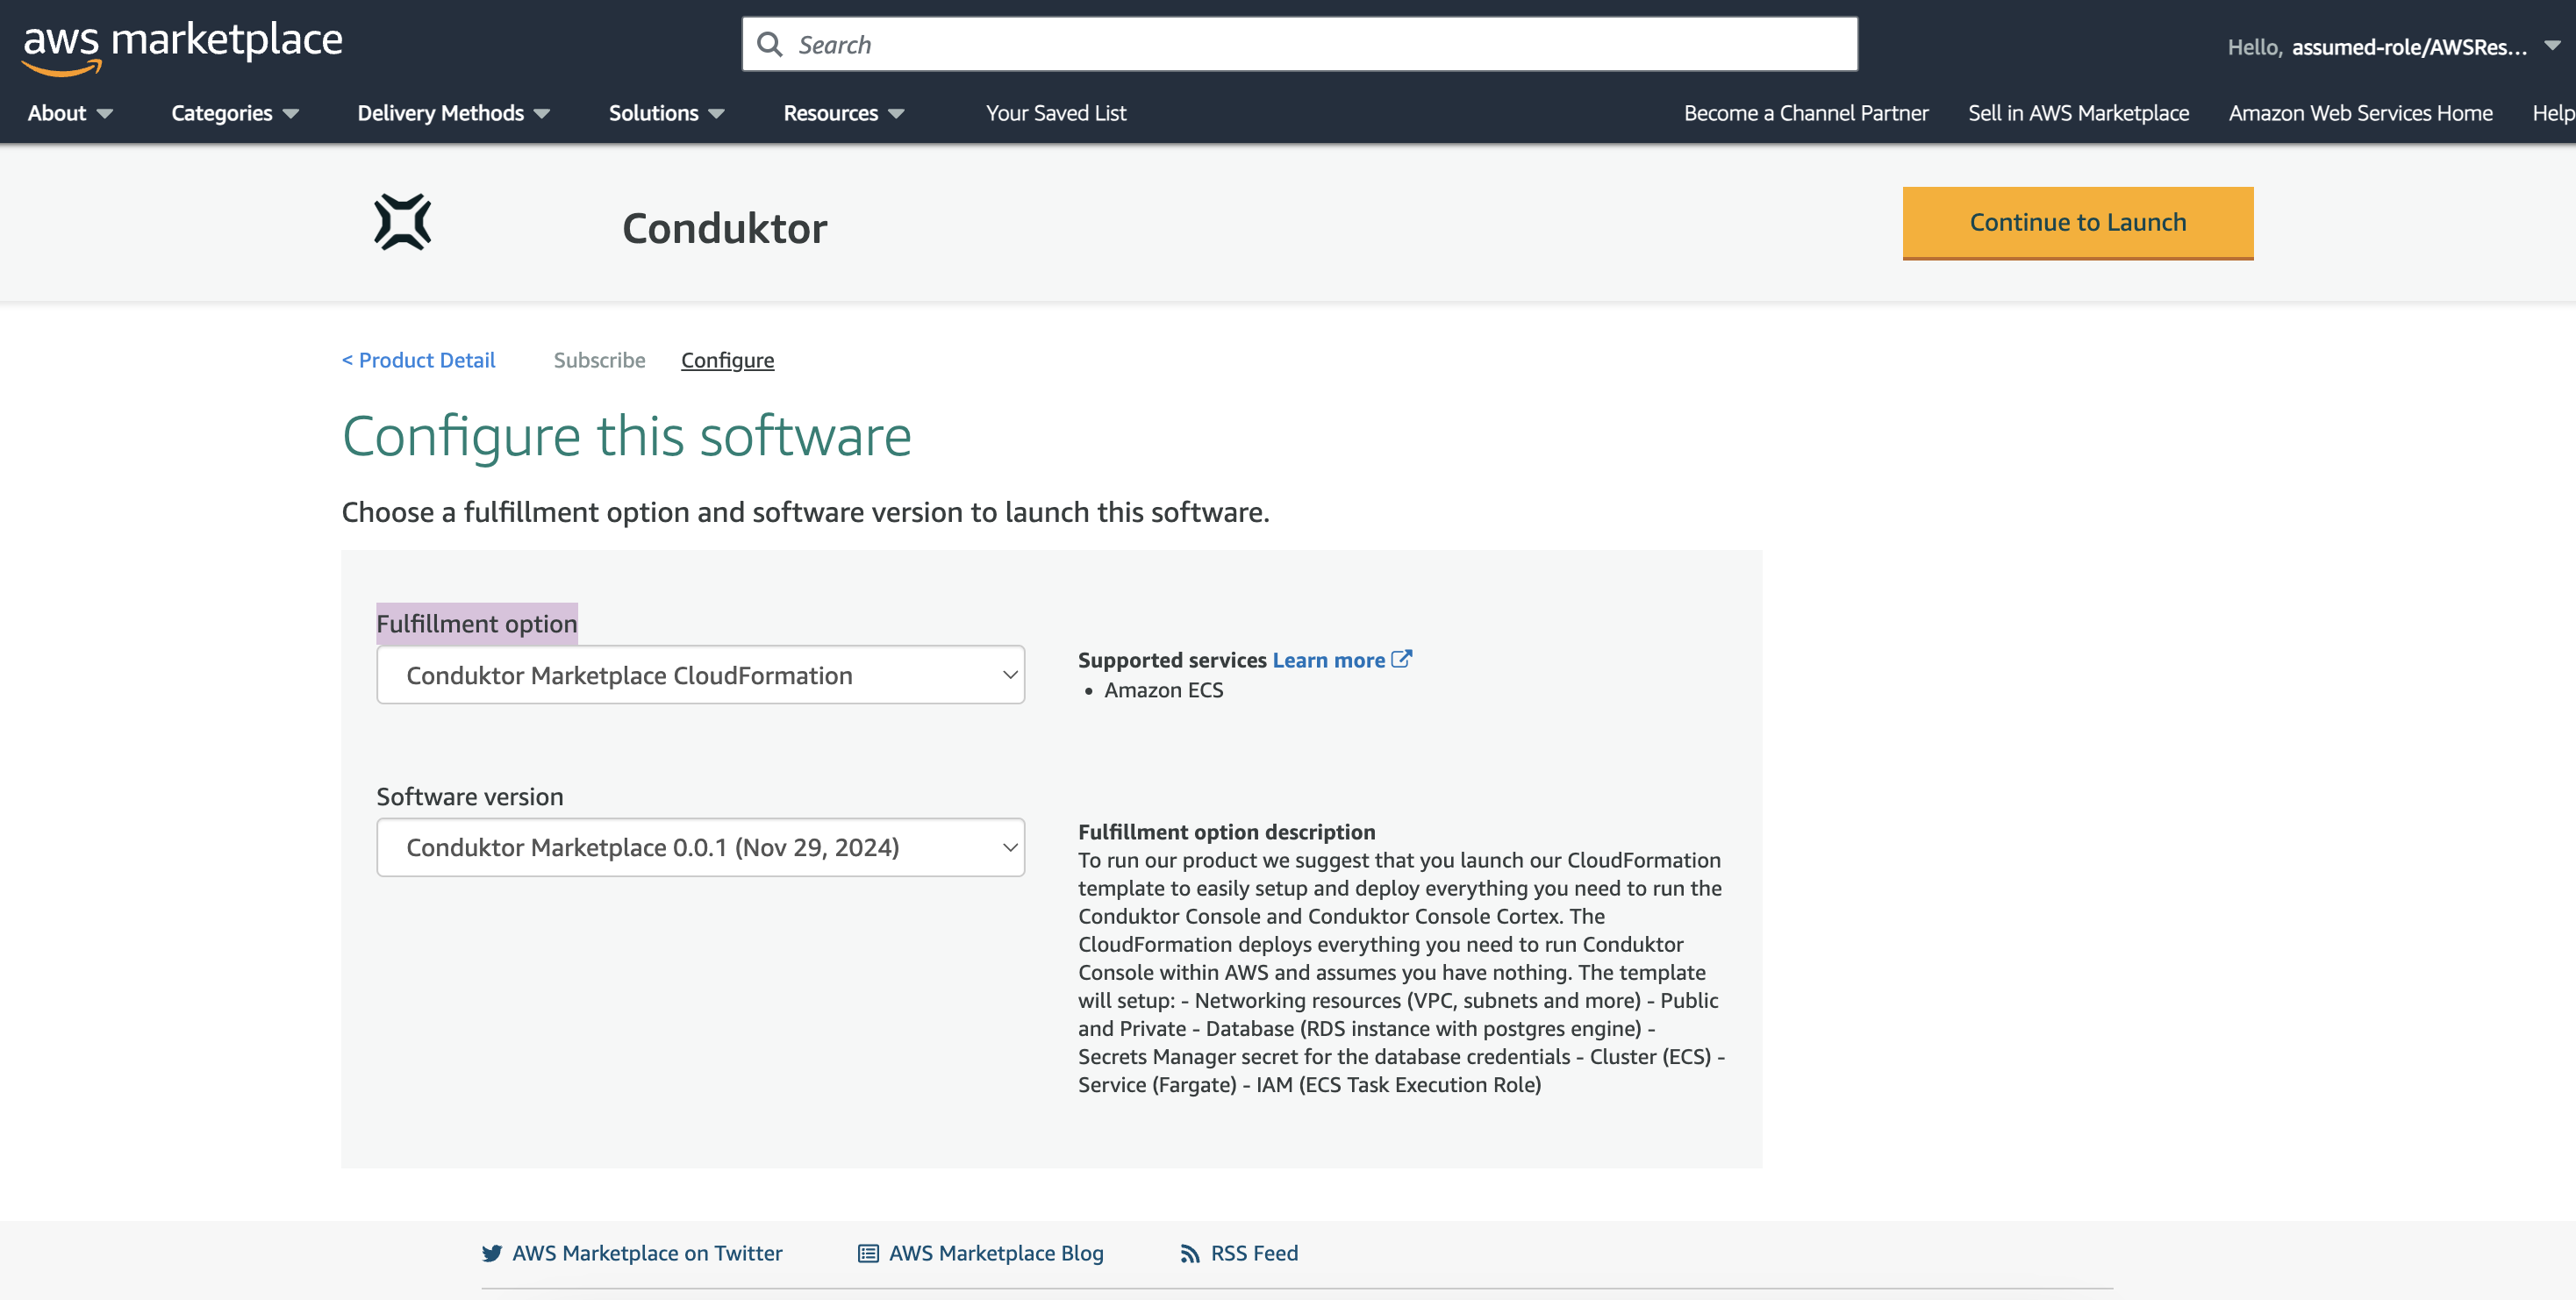
-
You now can choose how you want to deploy the CloudFormation template. We offer a quicklink that will take you directly to the CloudFormation console with the template pre-filled on your last previously used region (What this guide will be covering). We also offer the raw CloudFormation template that you can download and deploy manually. Select
Quick launch CloudFormation template.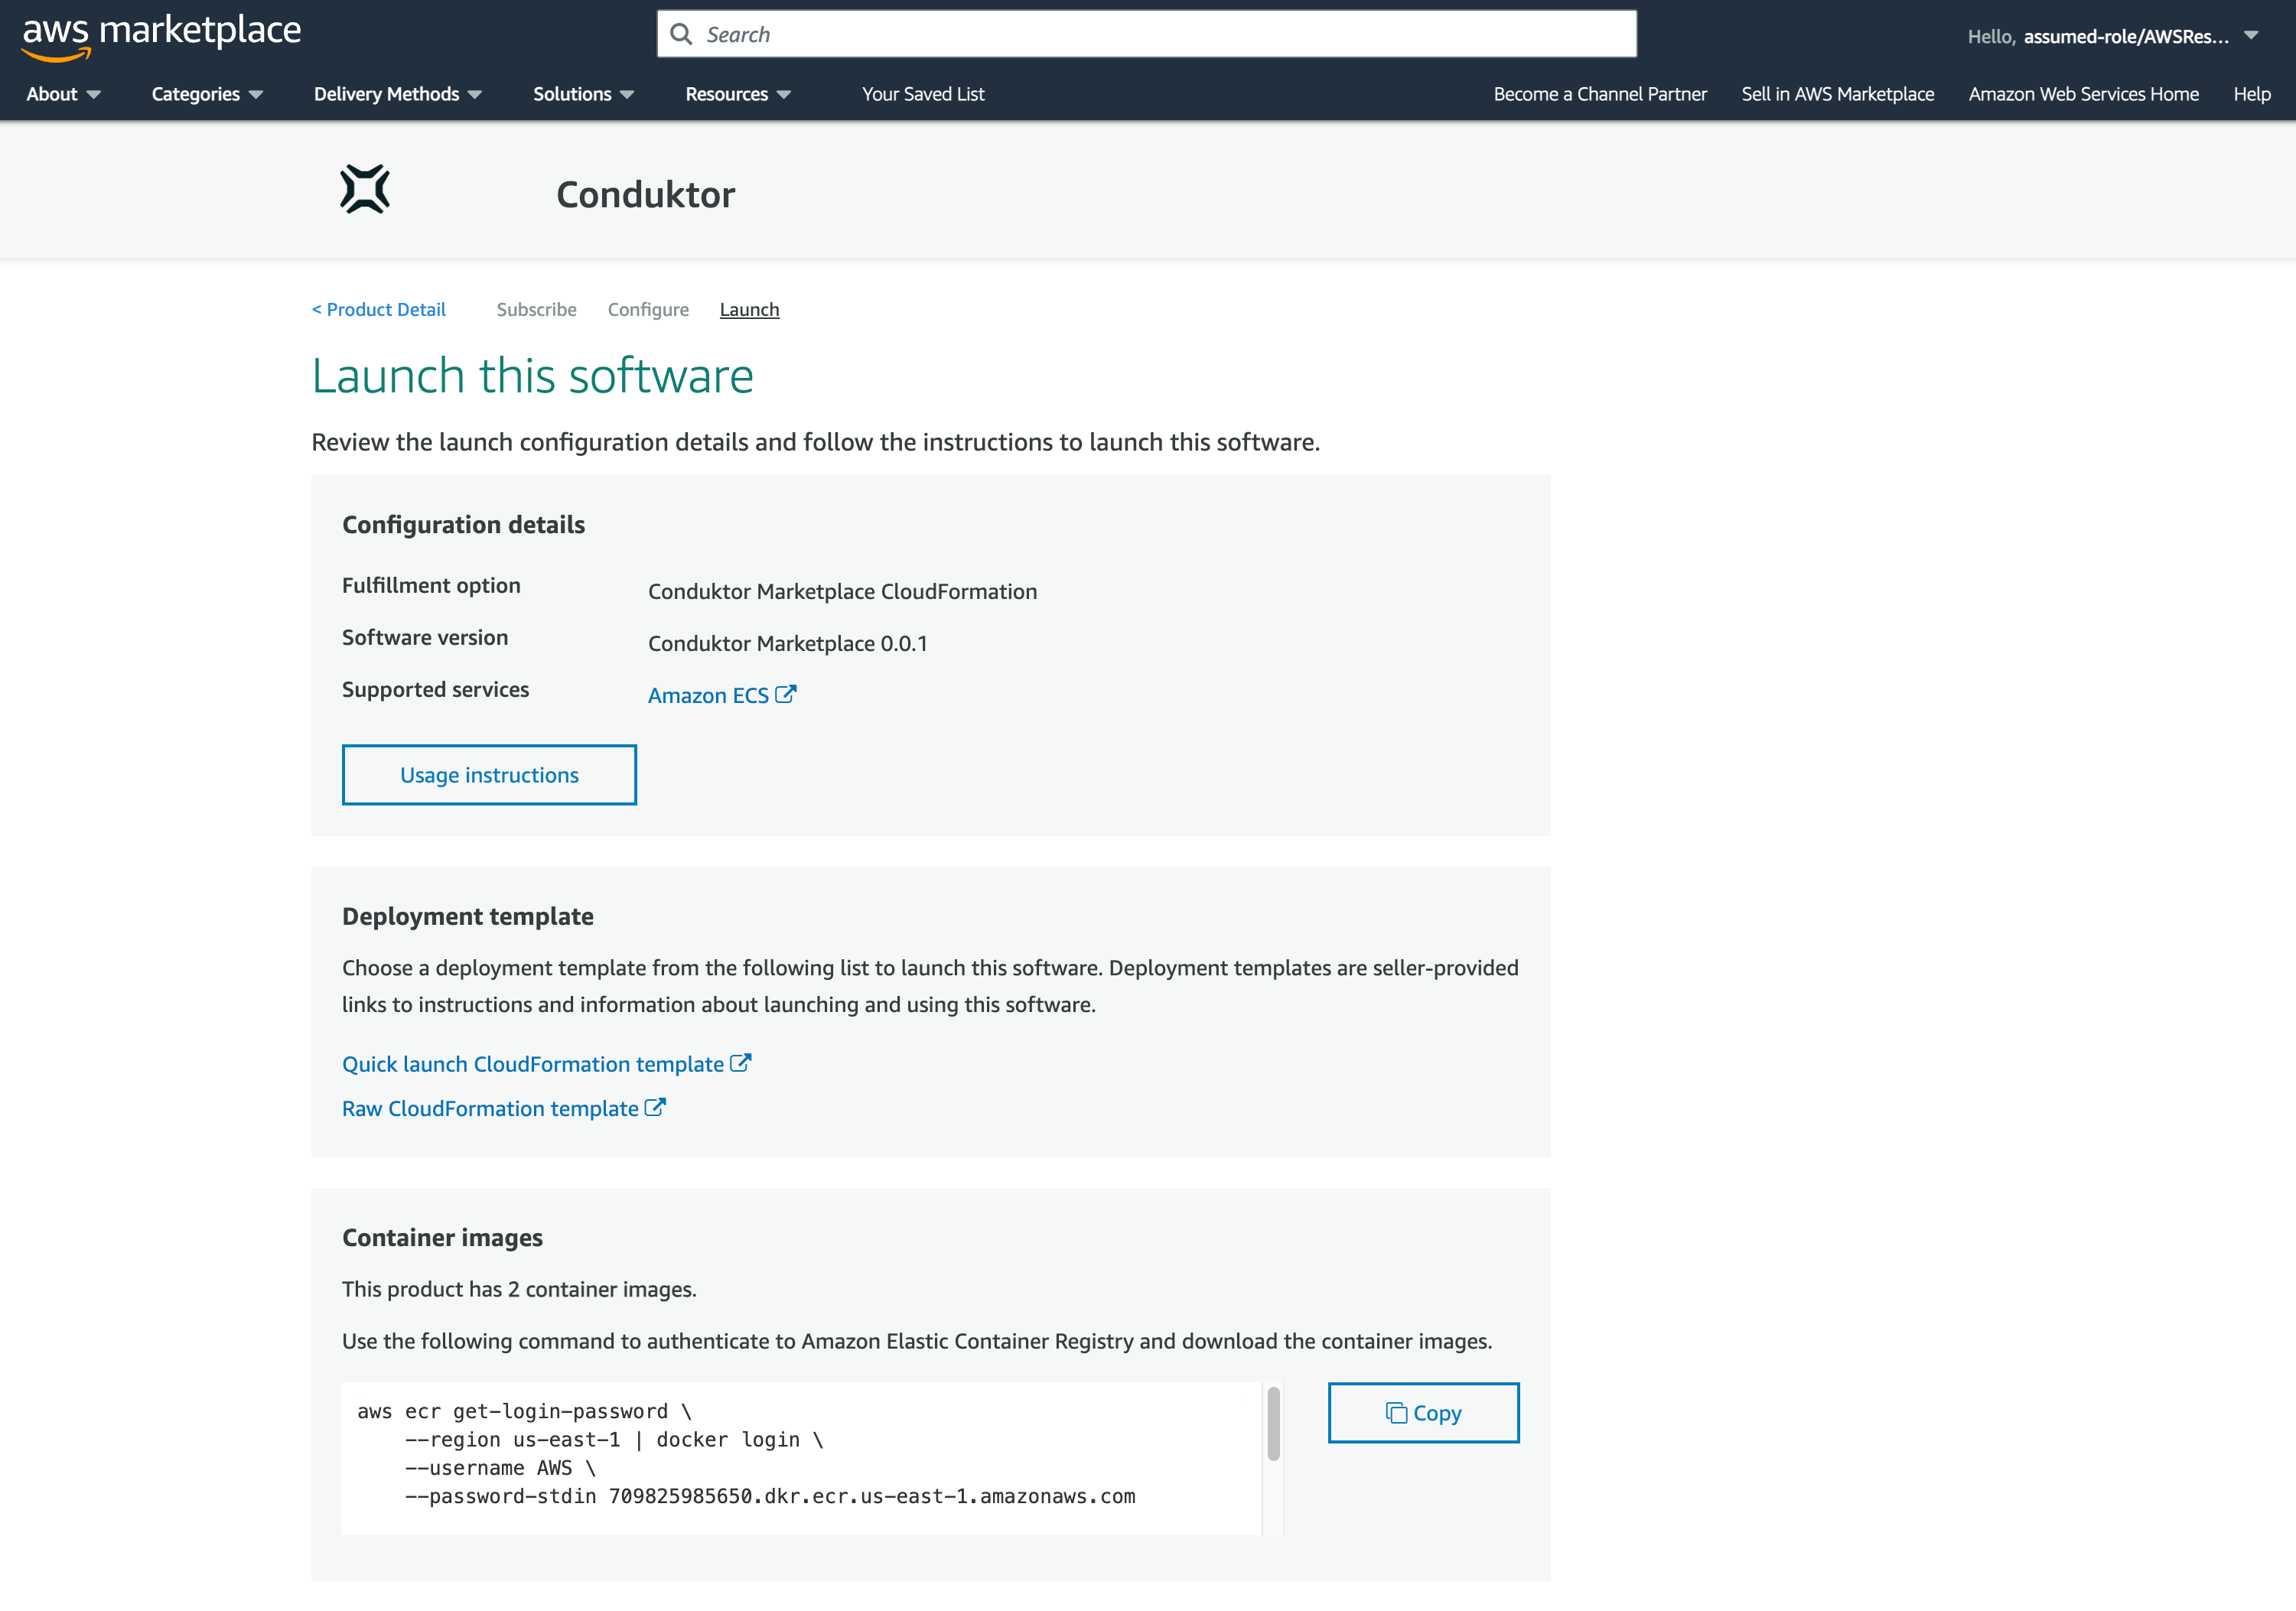
-
This will open you up to the CloudFormation page with the template pre-filled. Press
Next.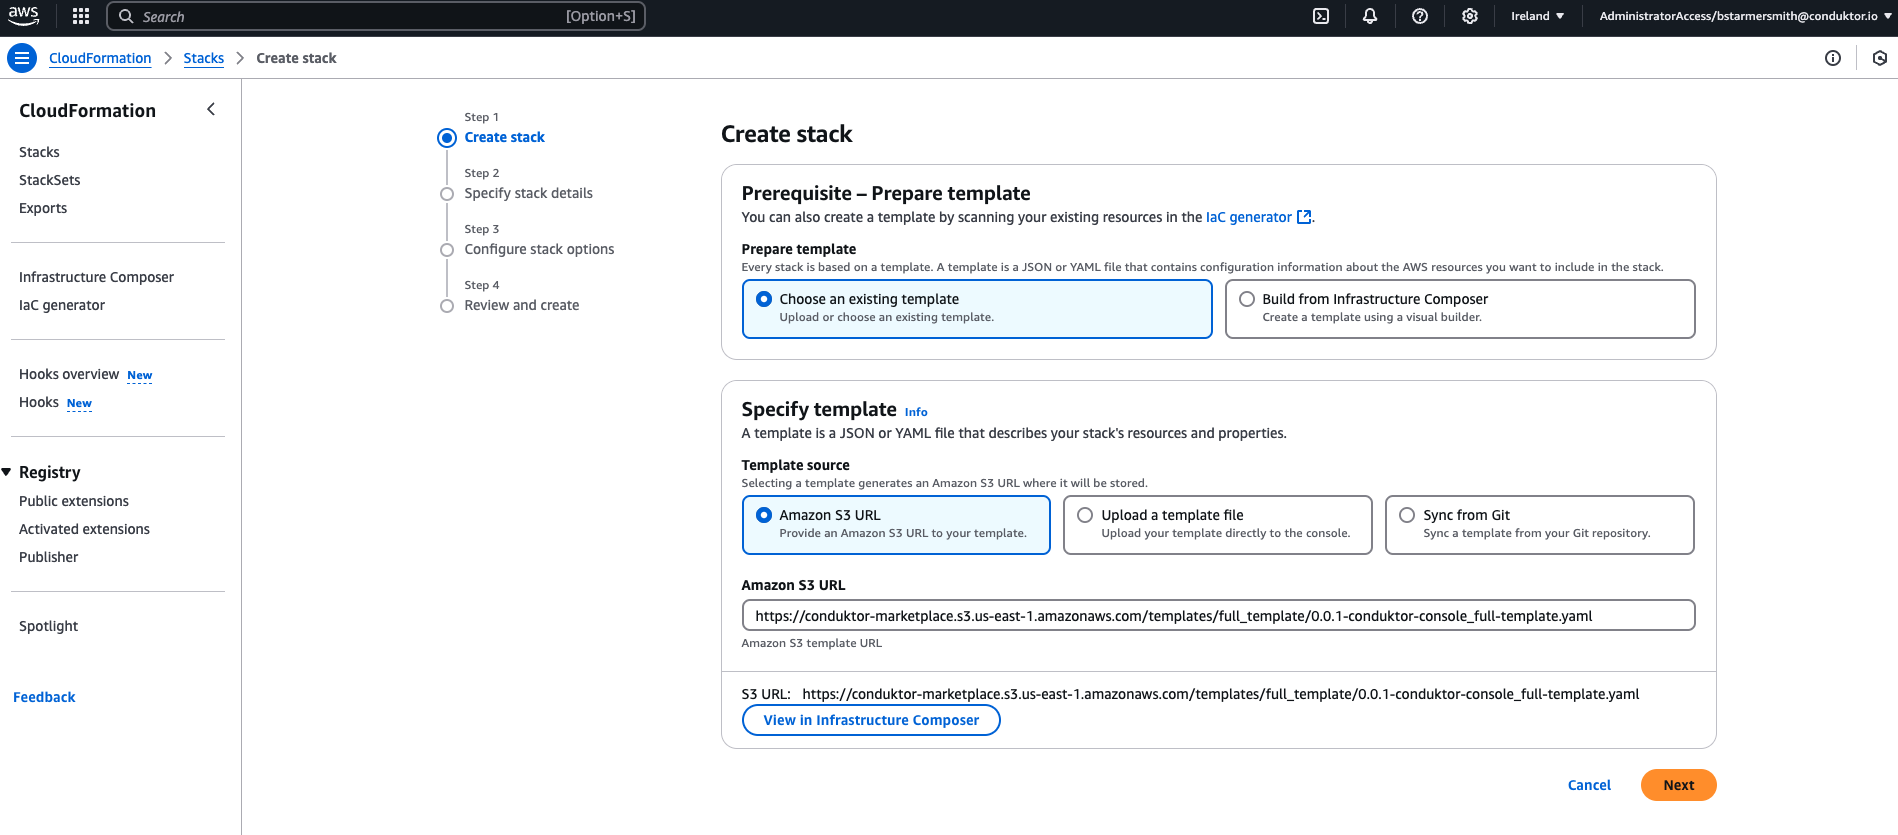
-
You will then be given the option to change the stack name or any of the other default values from our template. You will need to provide values for the missing CIDR properties towards the bottom of the page. Once you are happy with the parameters, press
Next.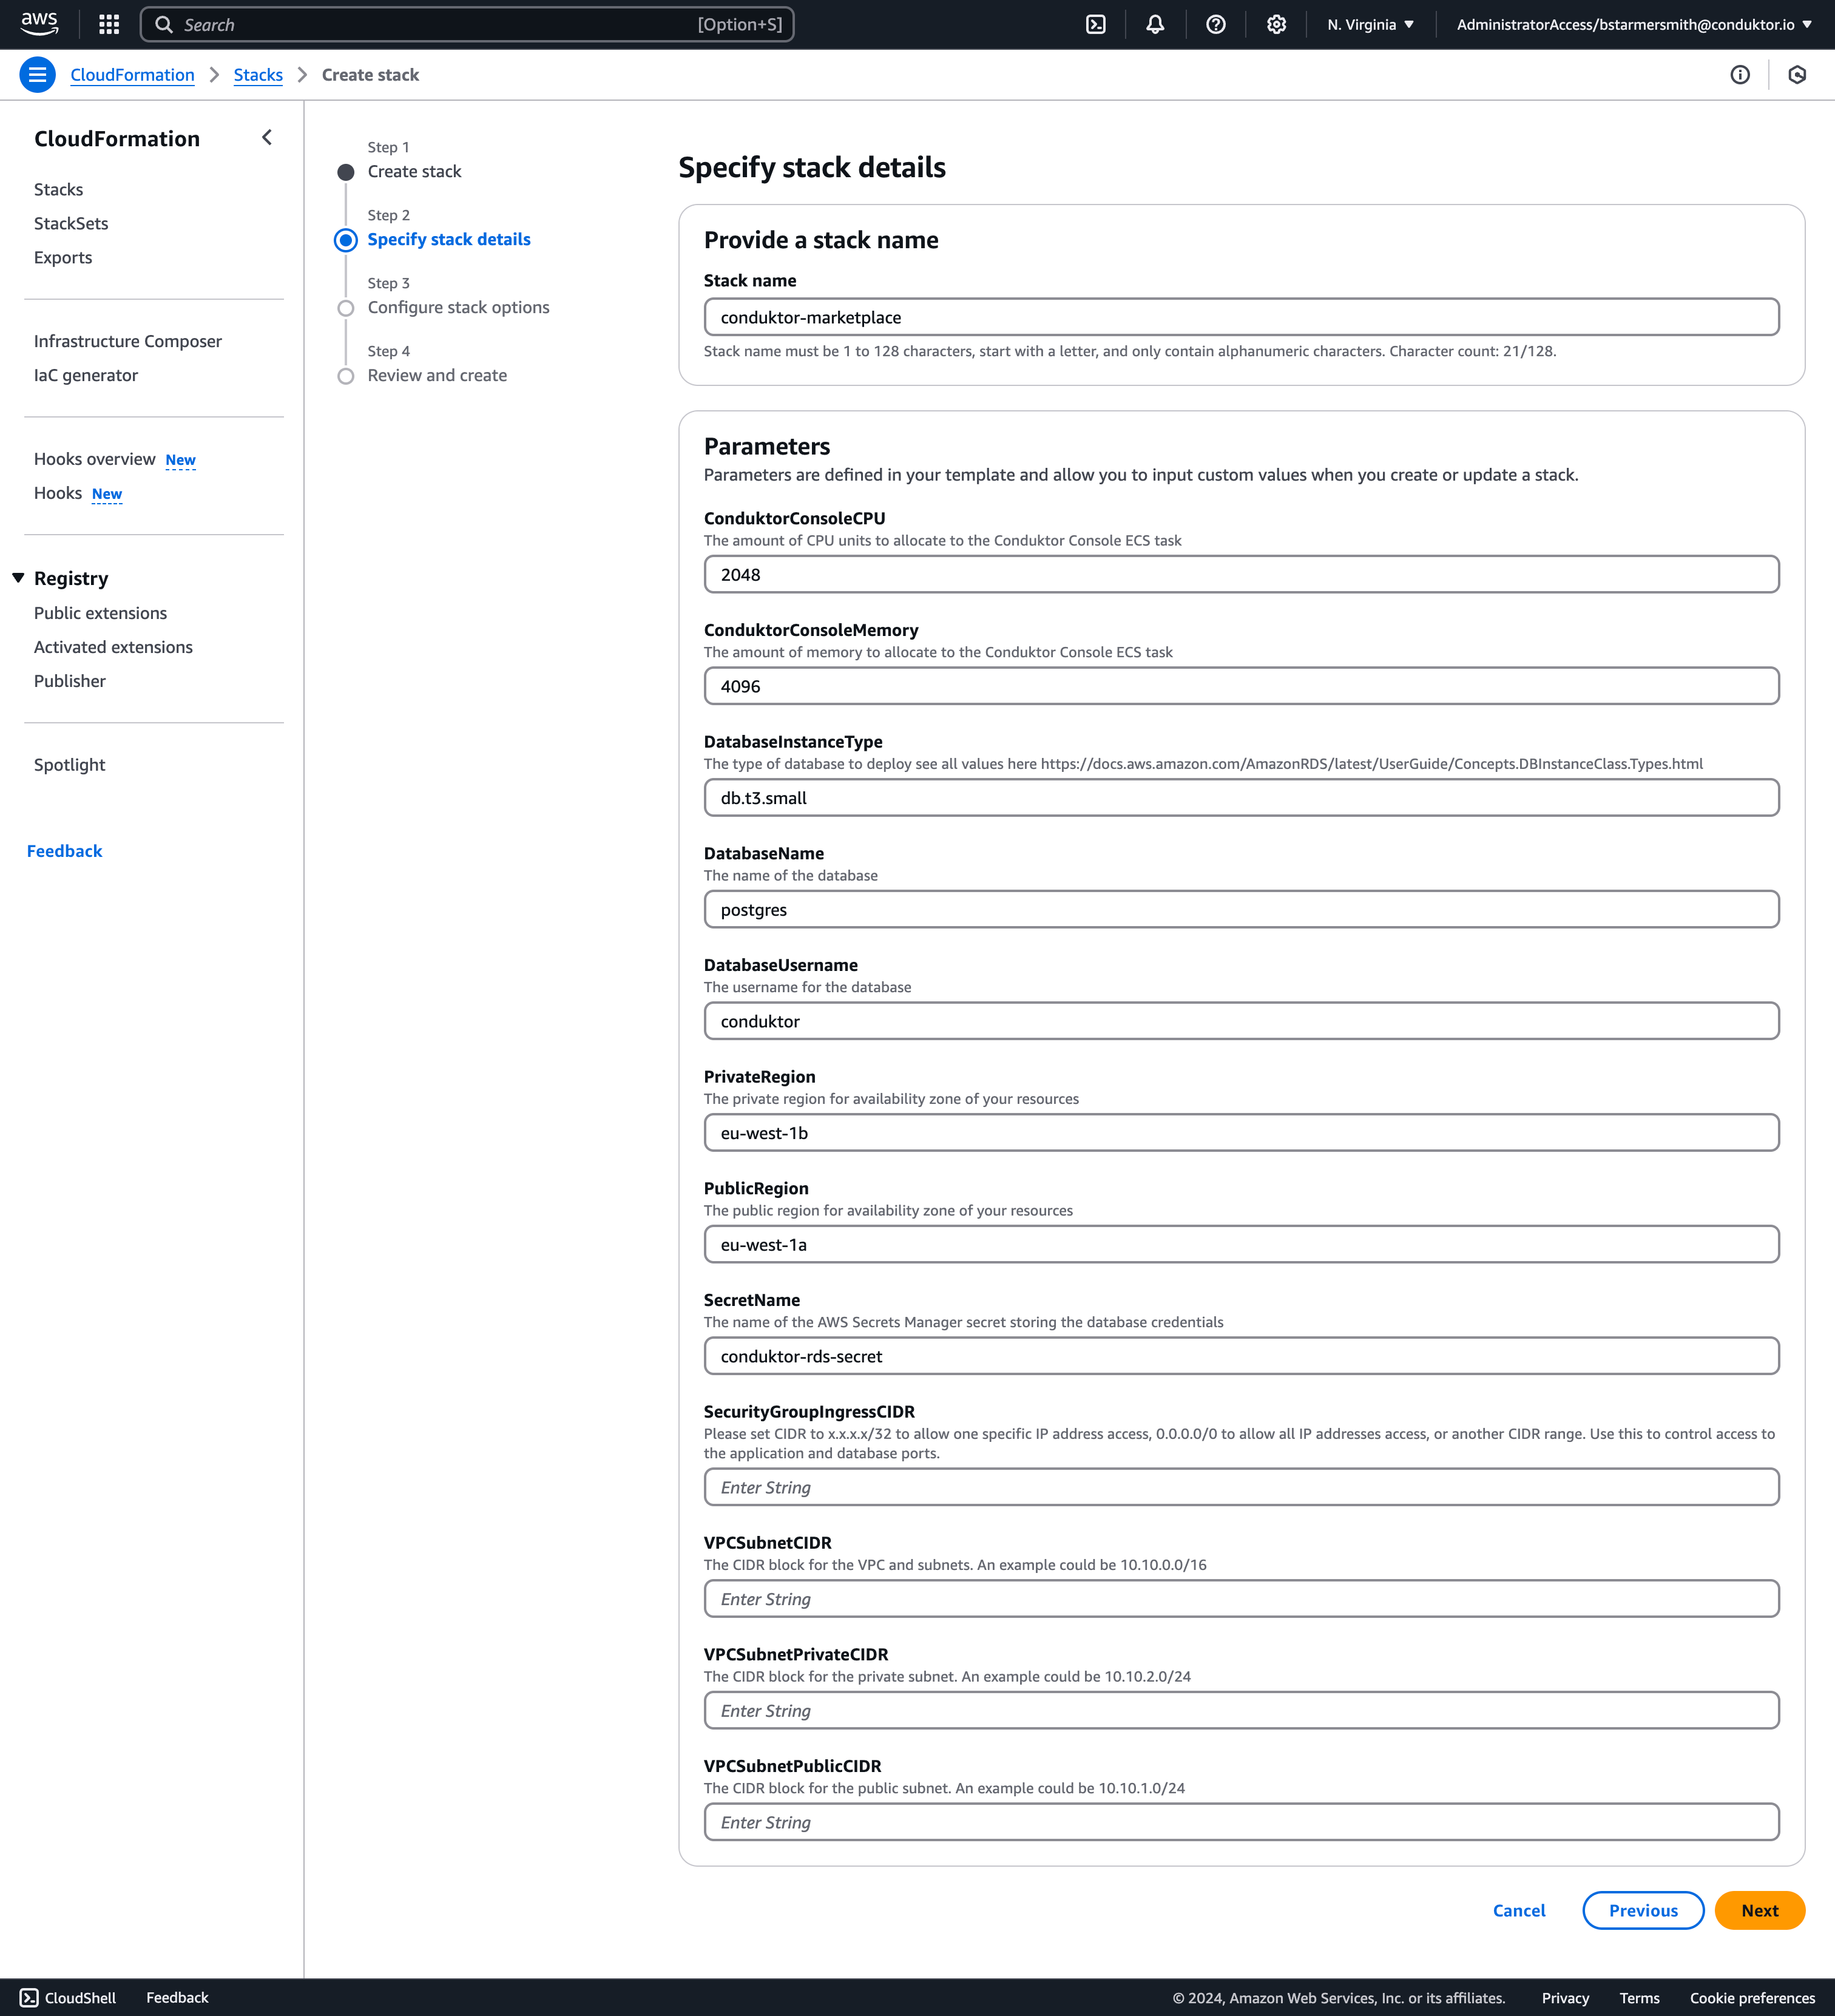
-
Configure your stack options and acknowledge that the CloudFormation template will create IAM resources and click Next.
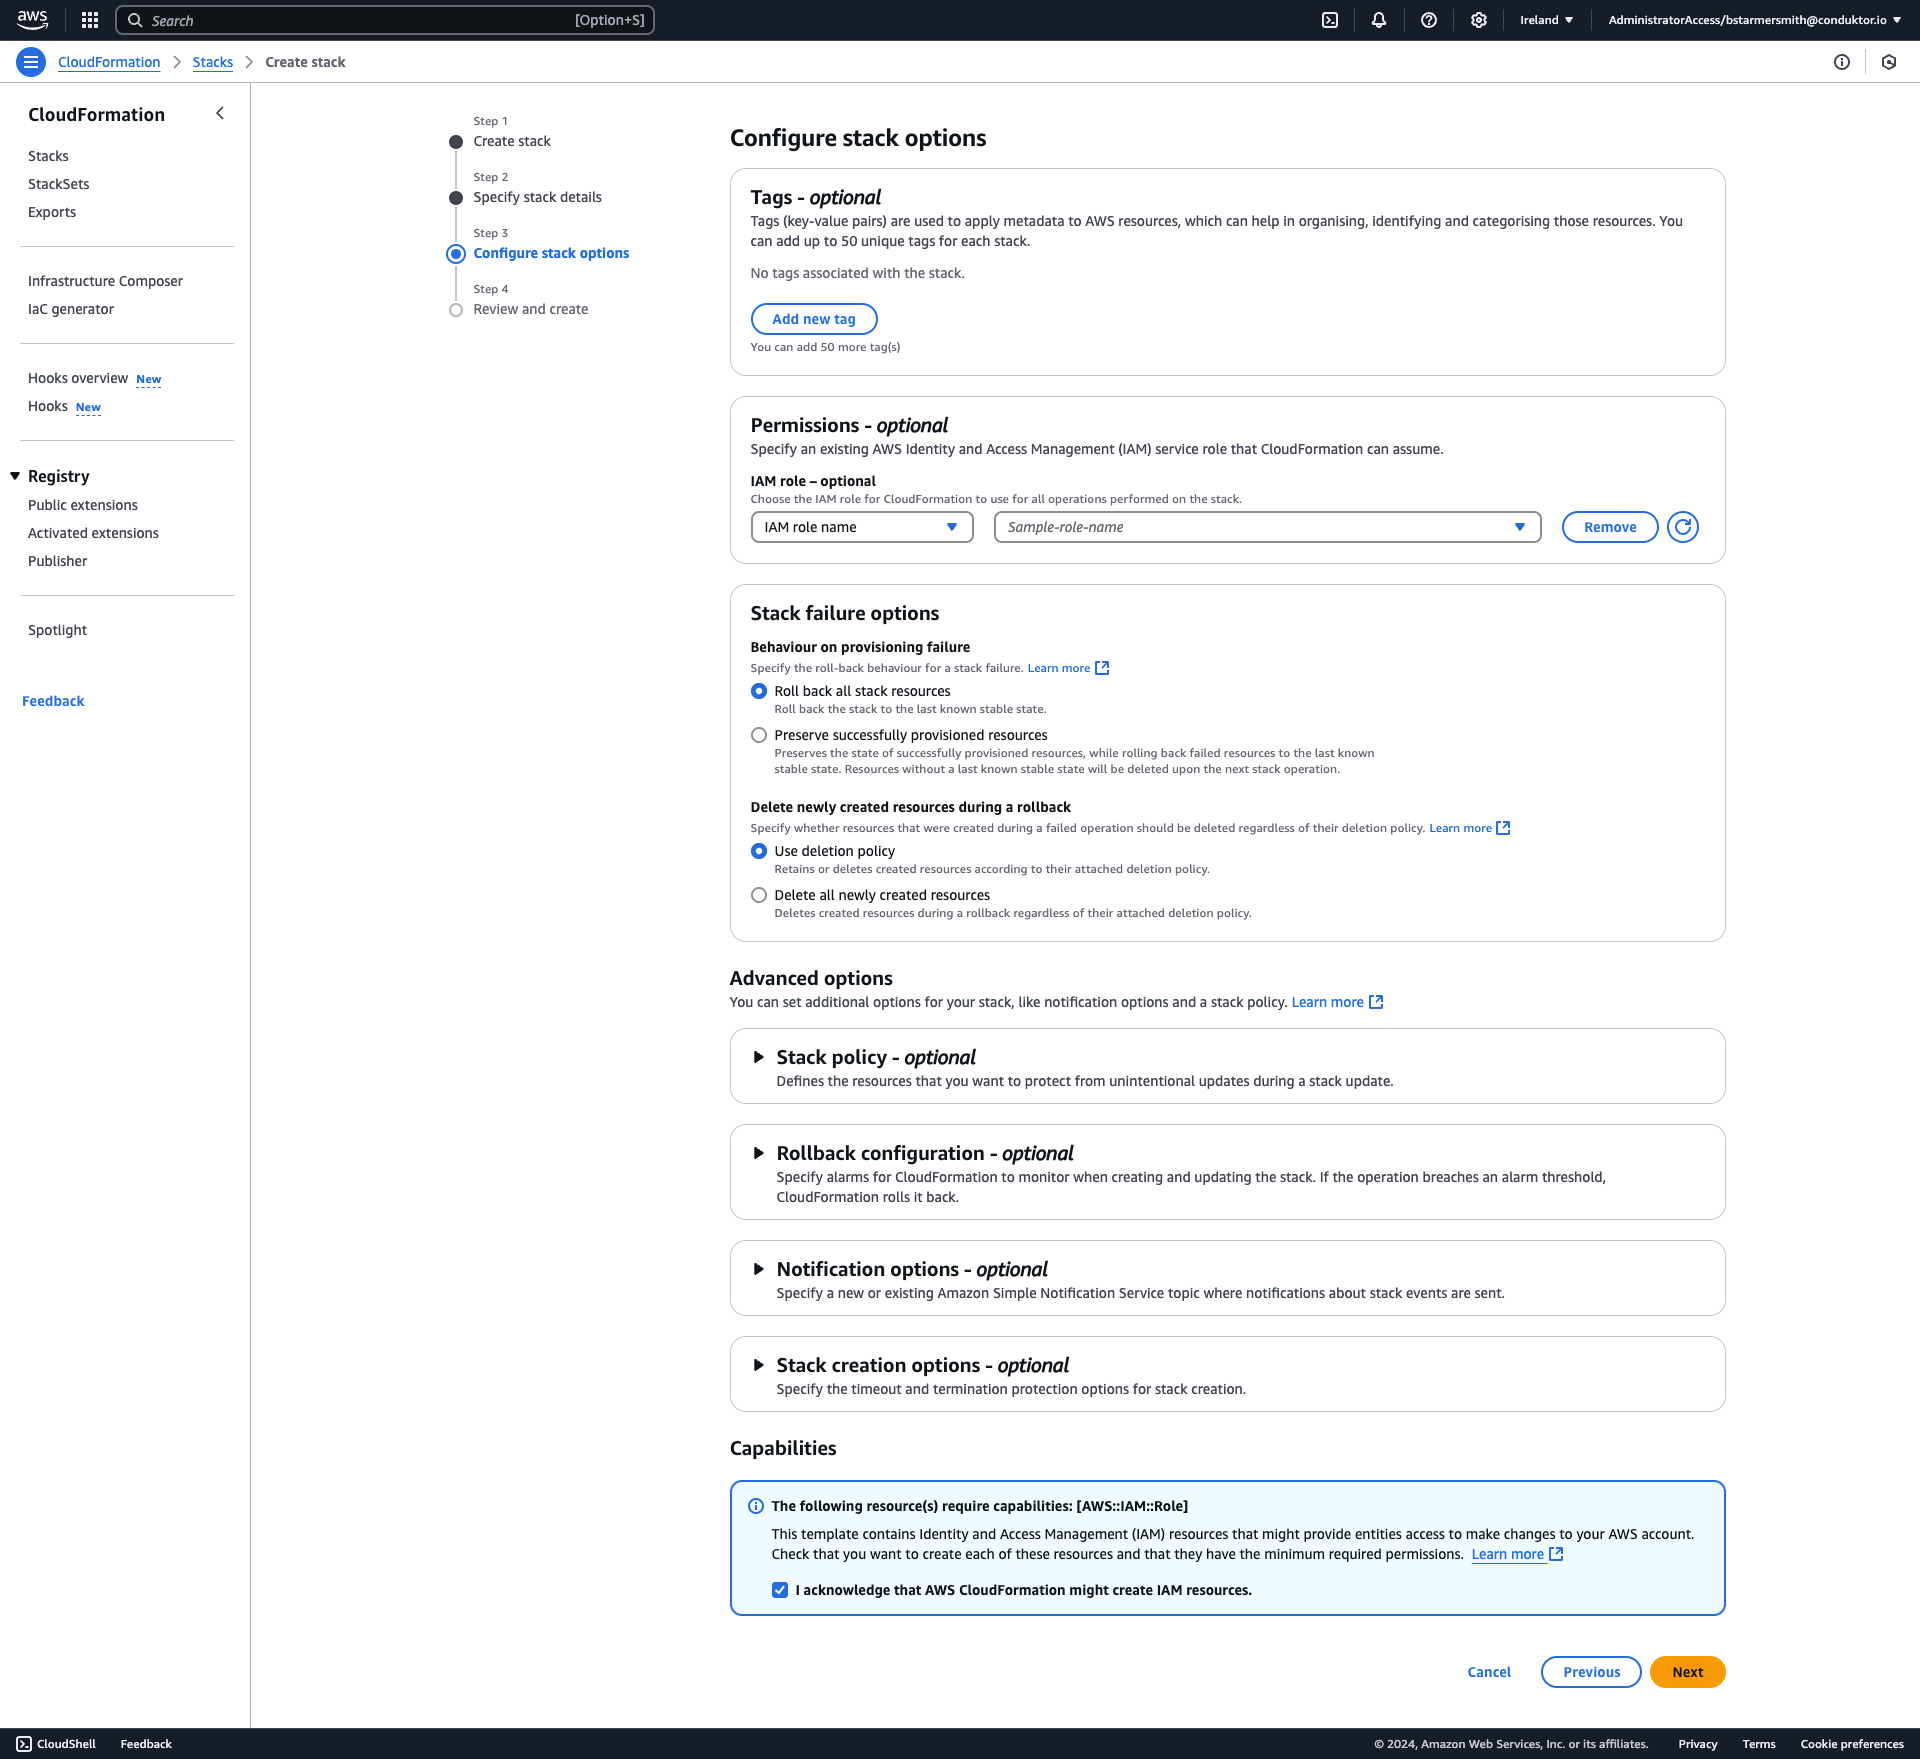
-
You can then review the CloudFormation stack and then click Submit.
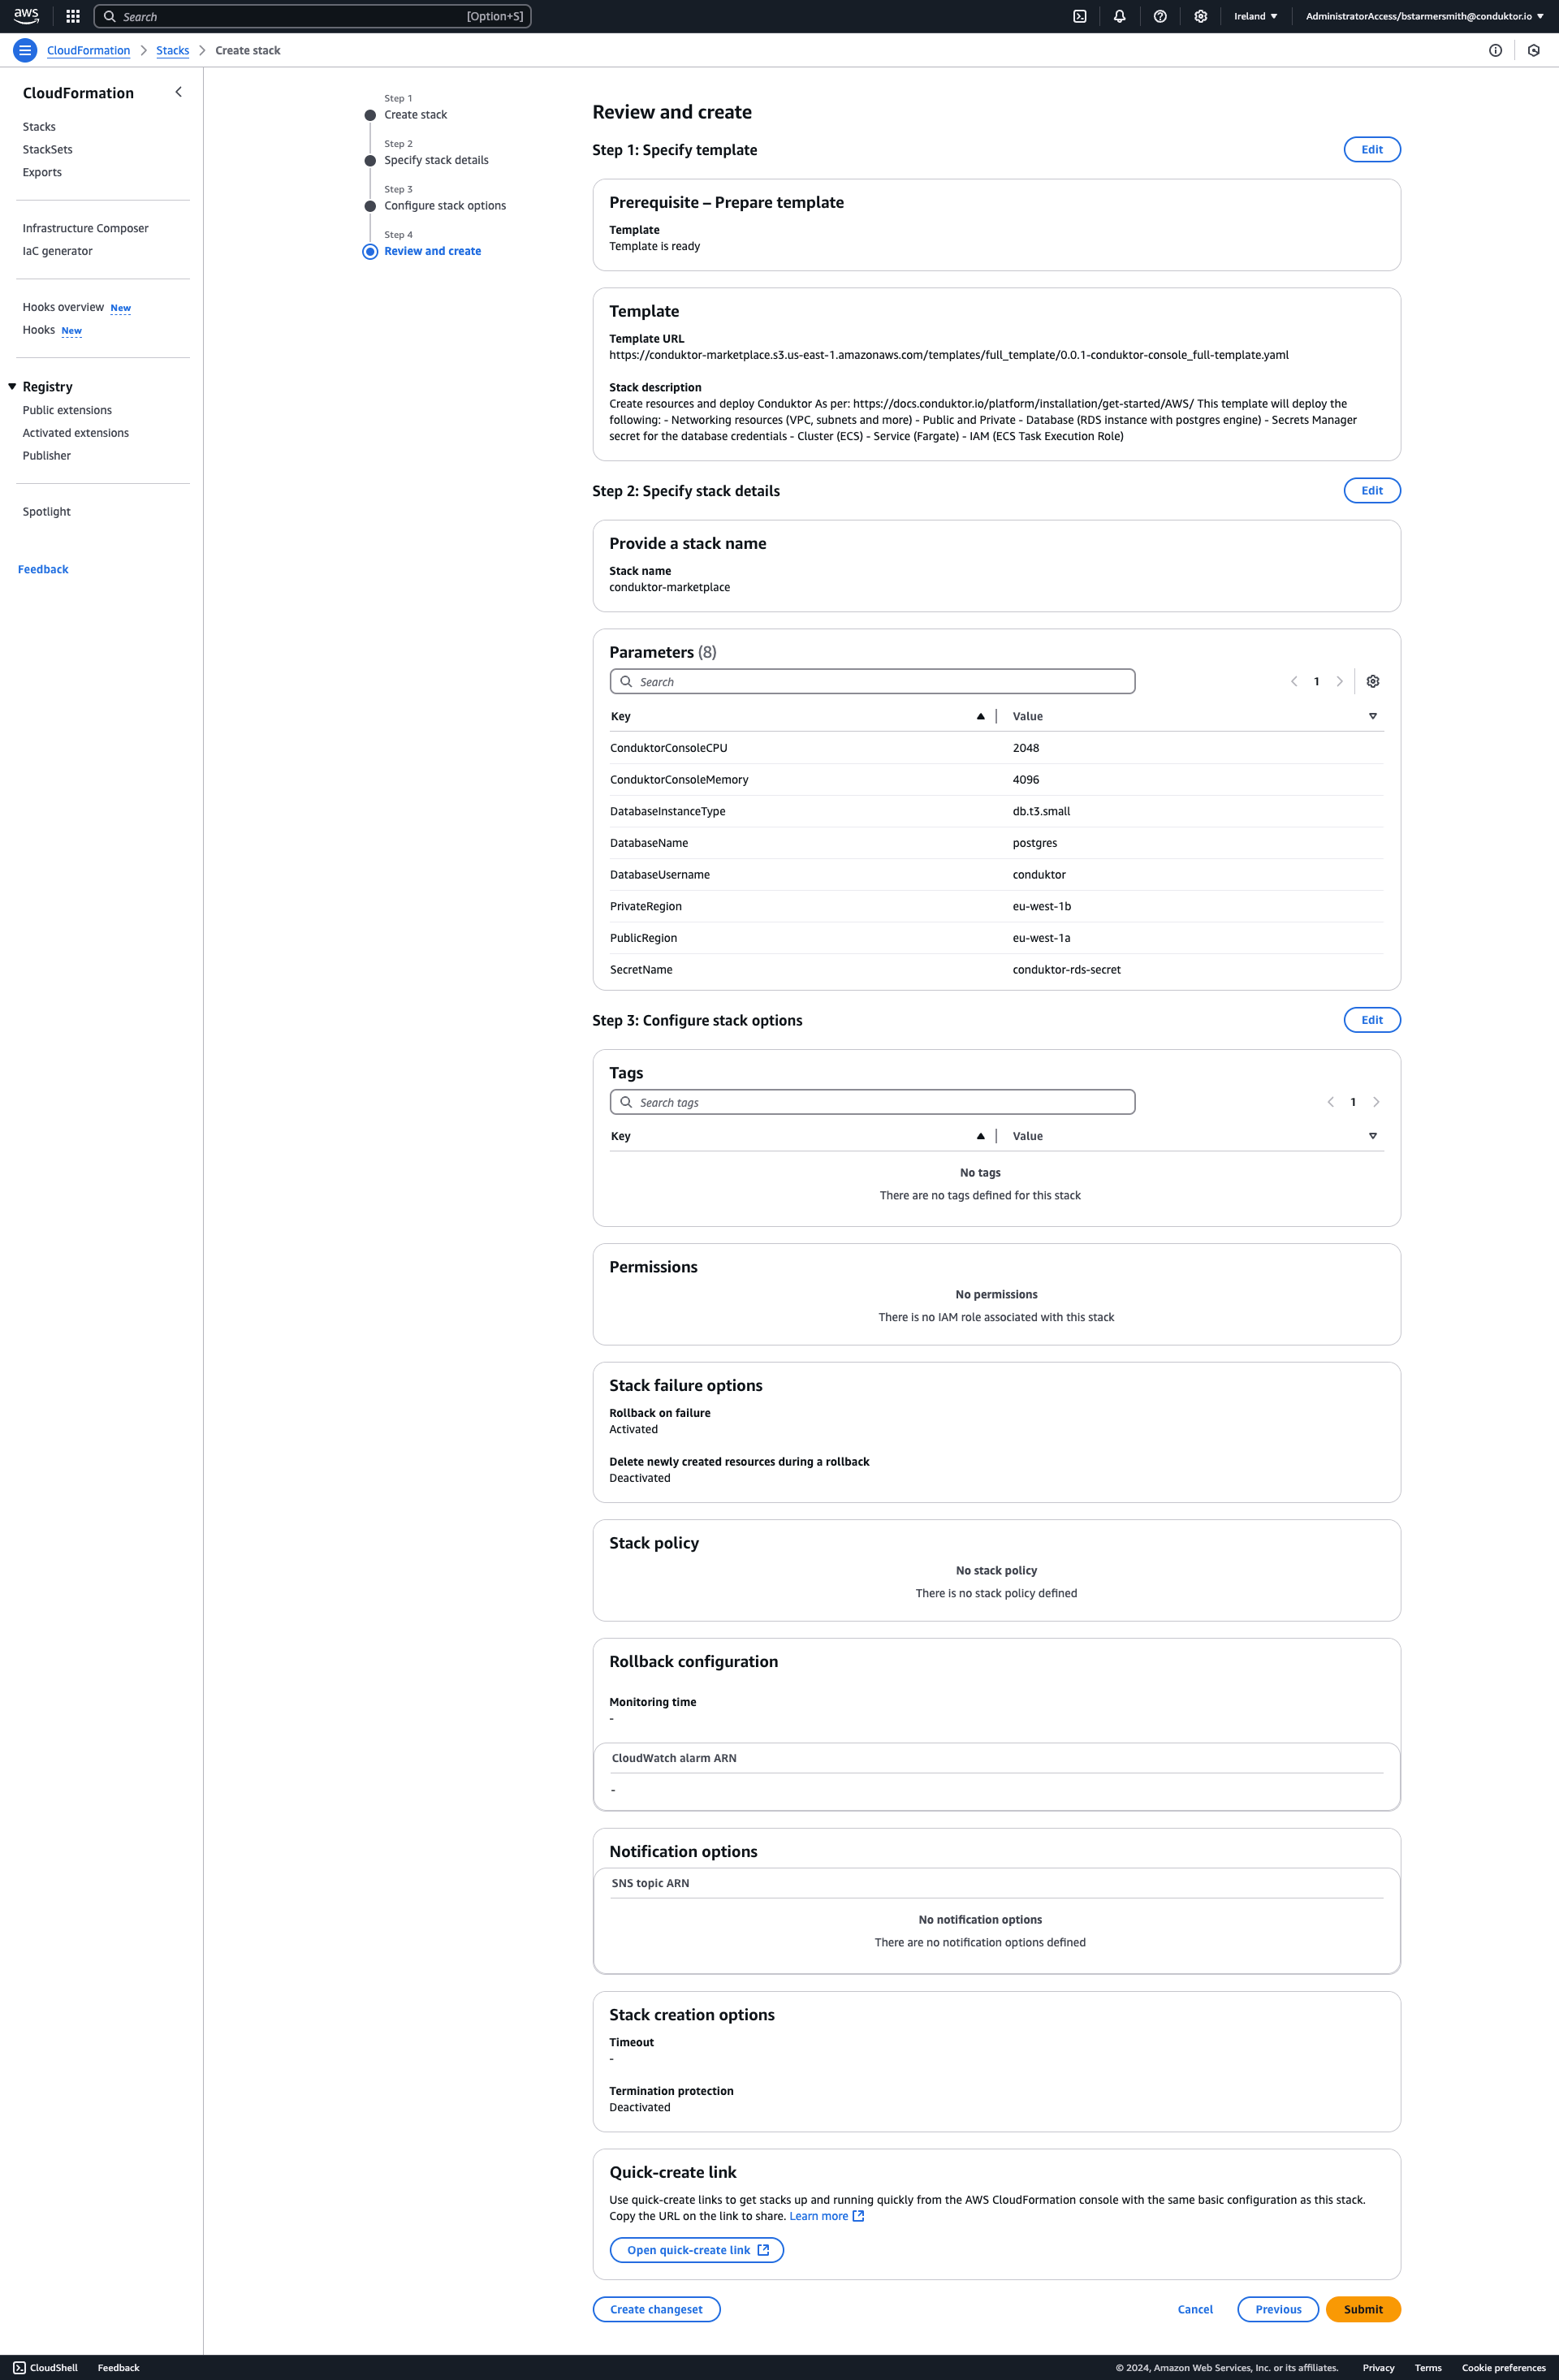
-
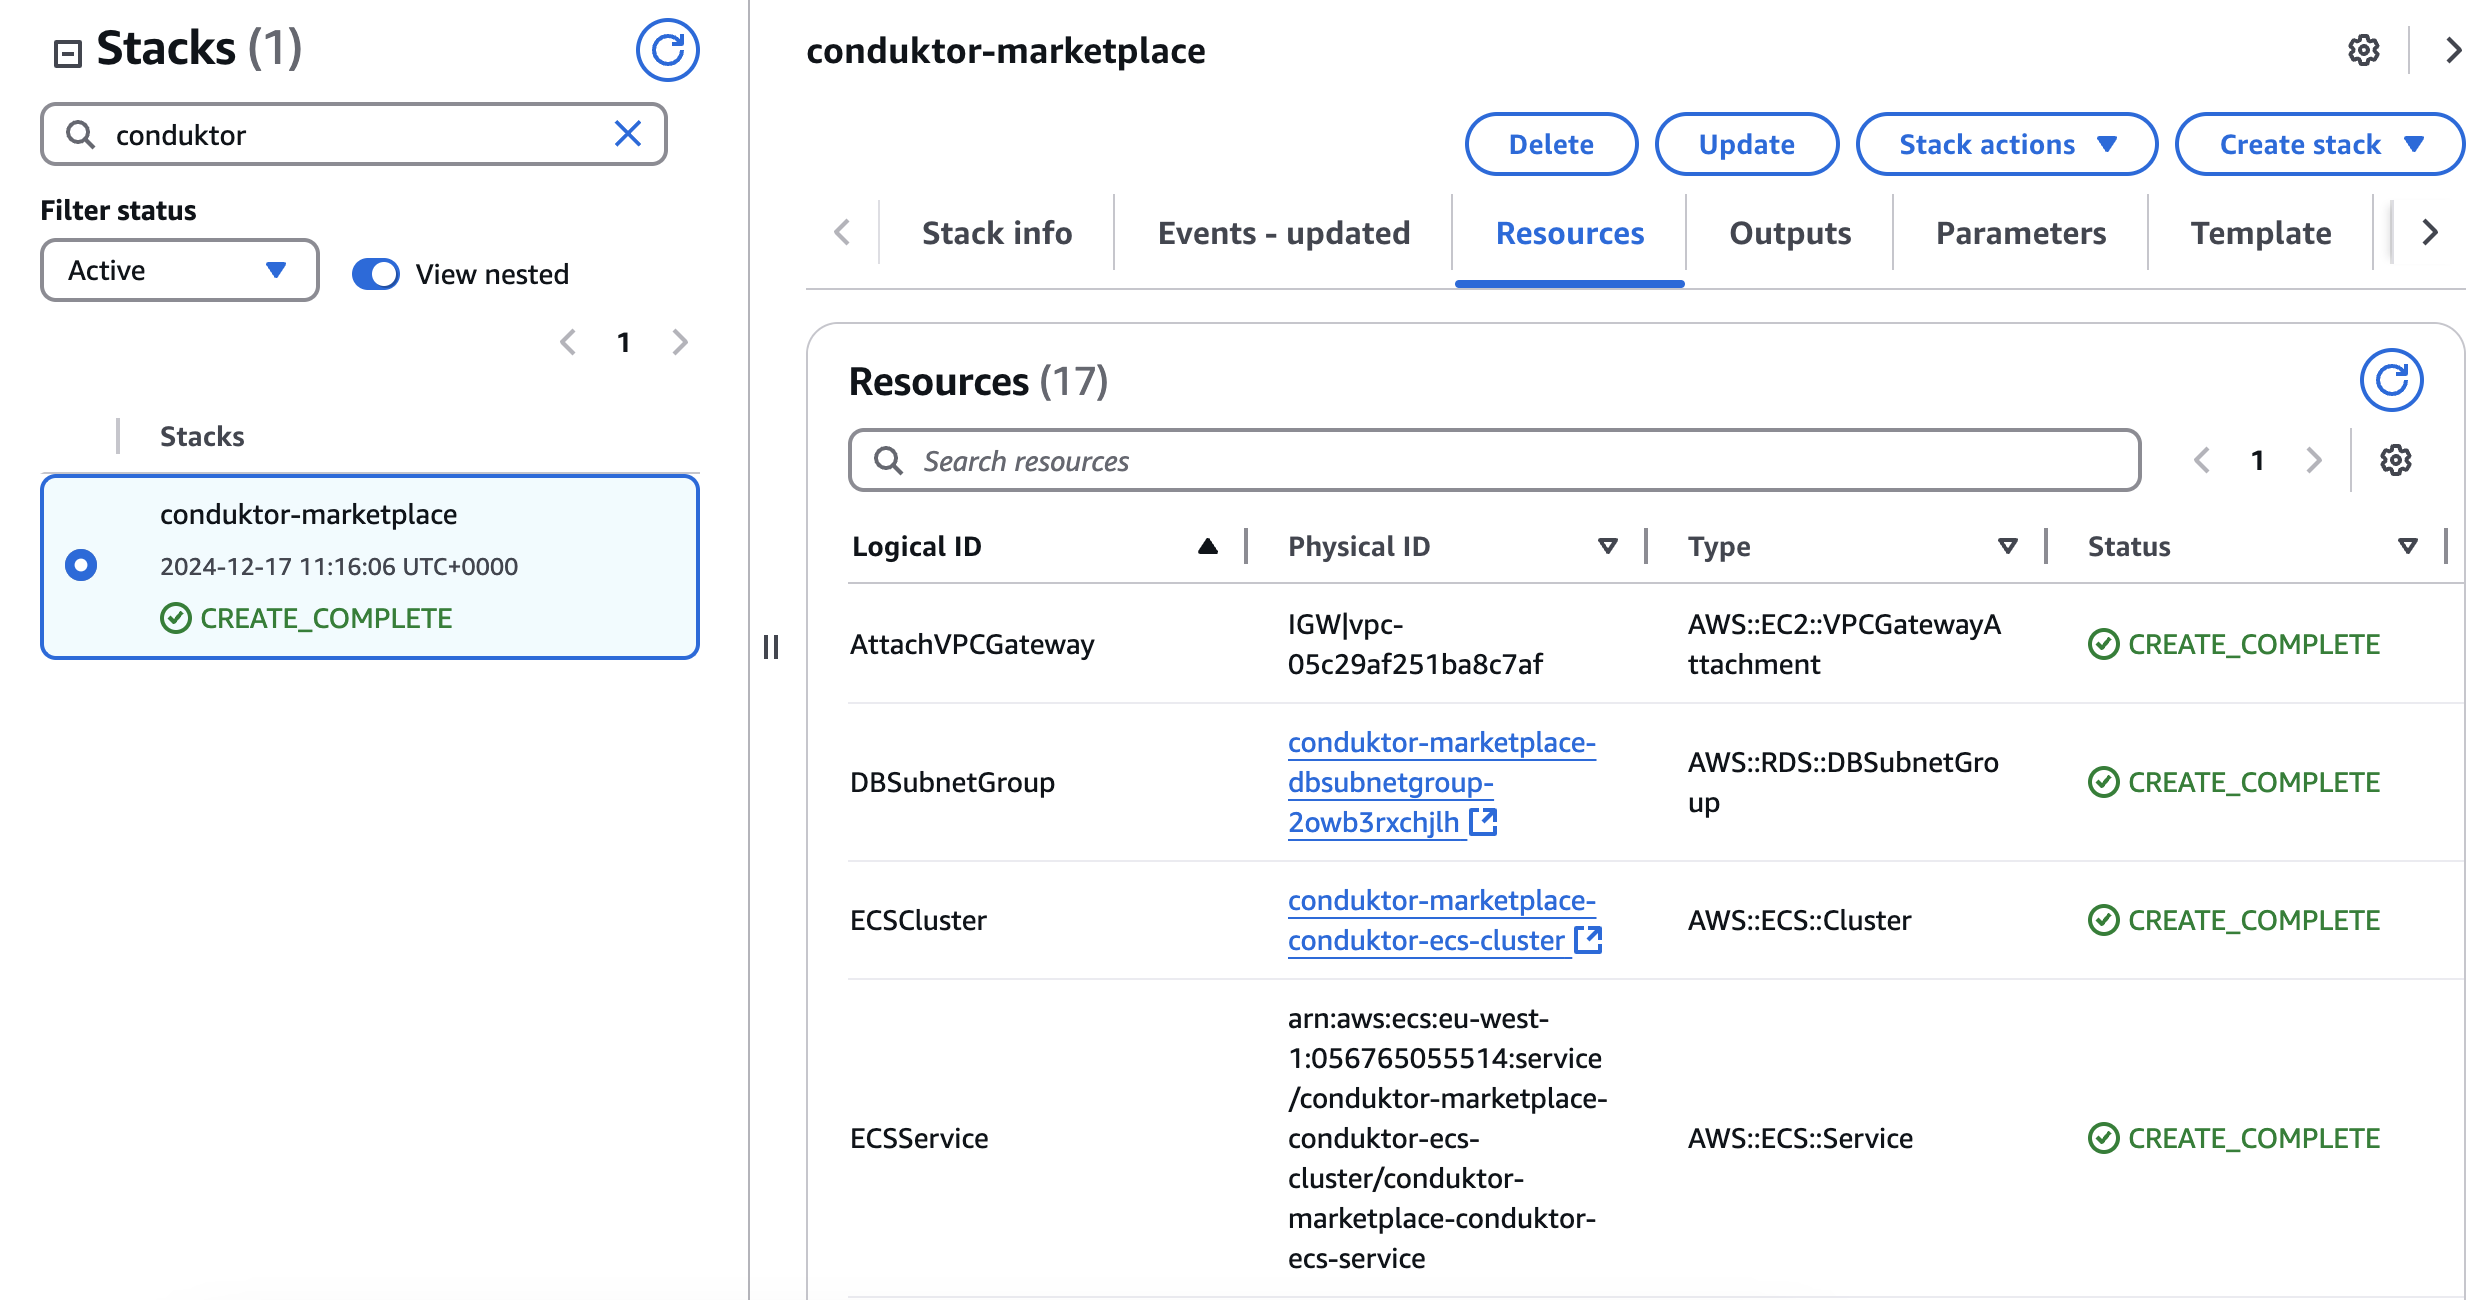
Wait for all resources to be created. This may take some time, about 10 minutes depending how quickly AWS deploys RDS.
-
From the Resources tab, click on
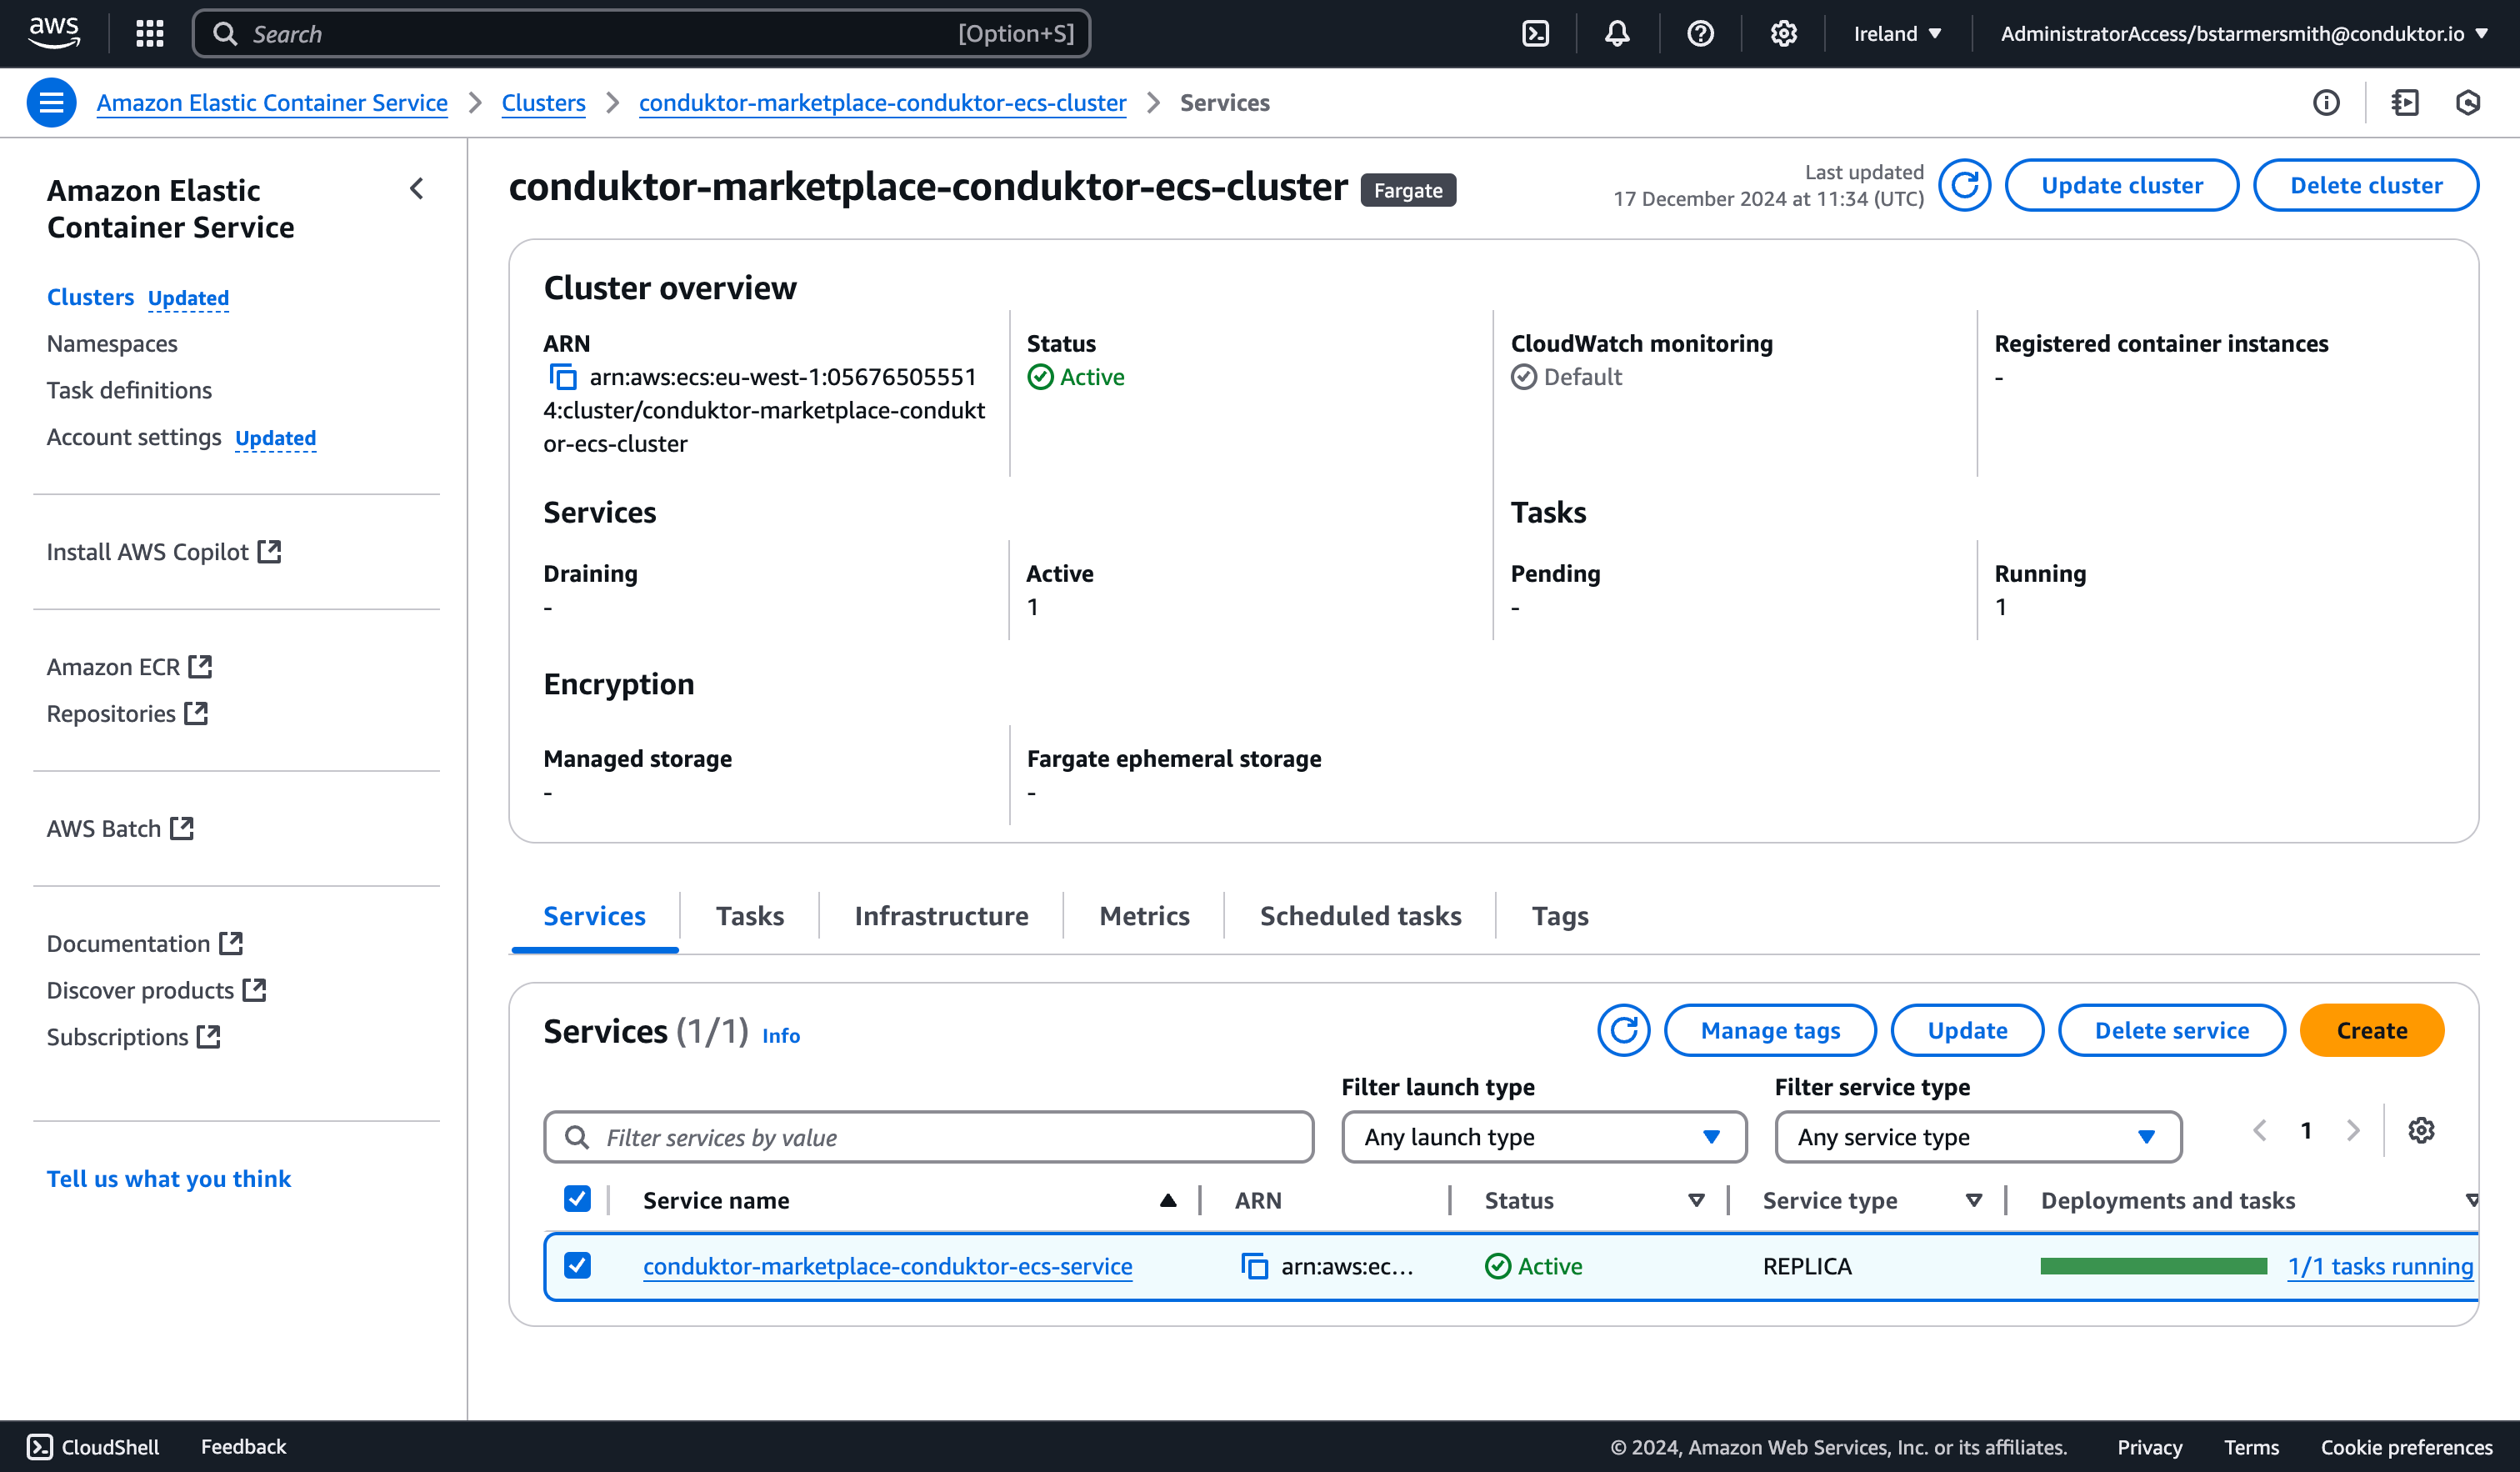
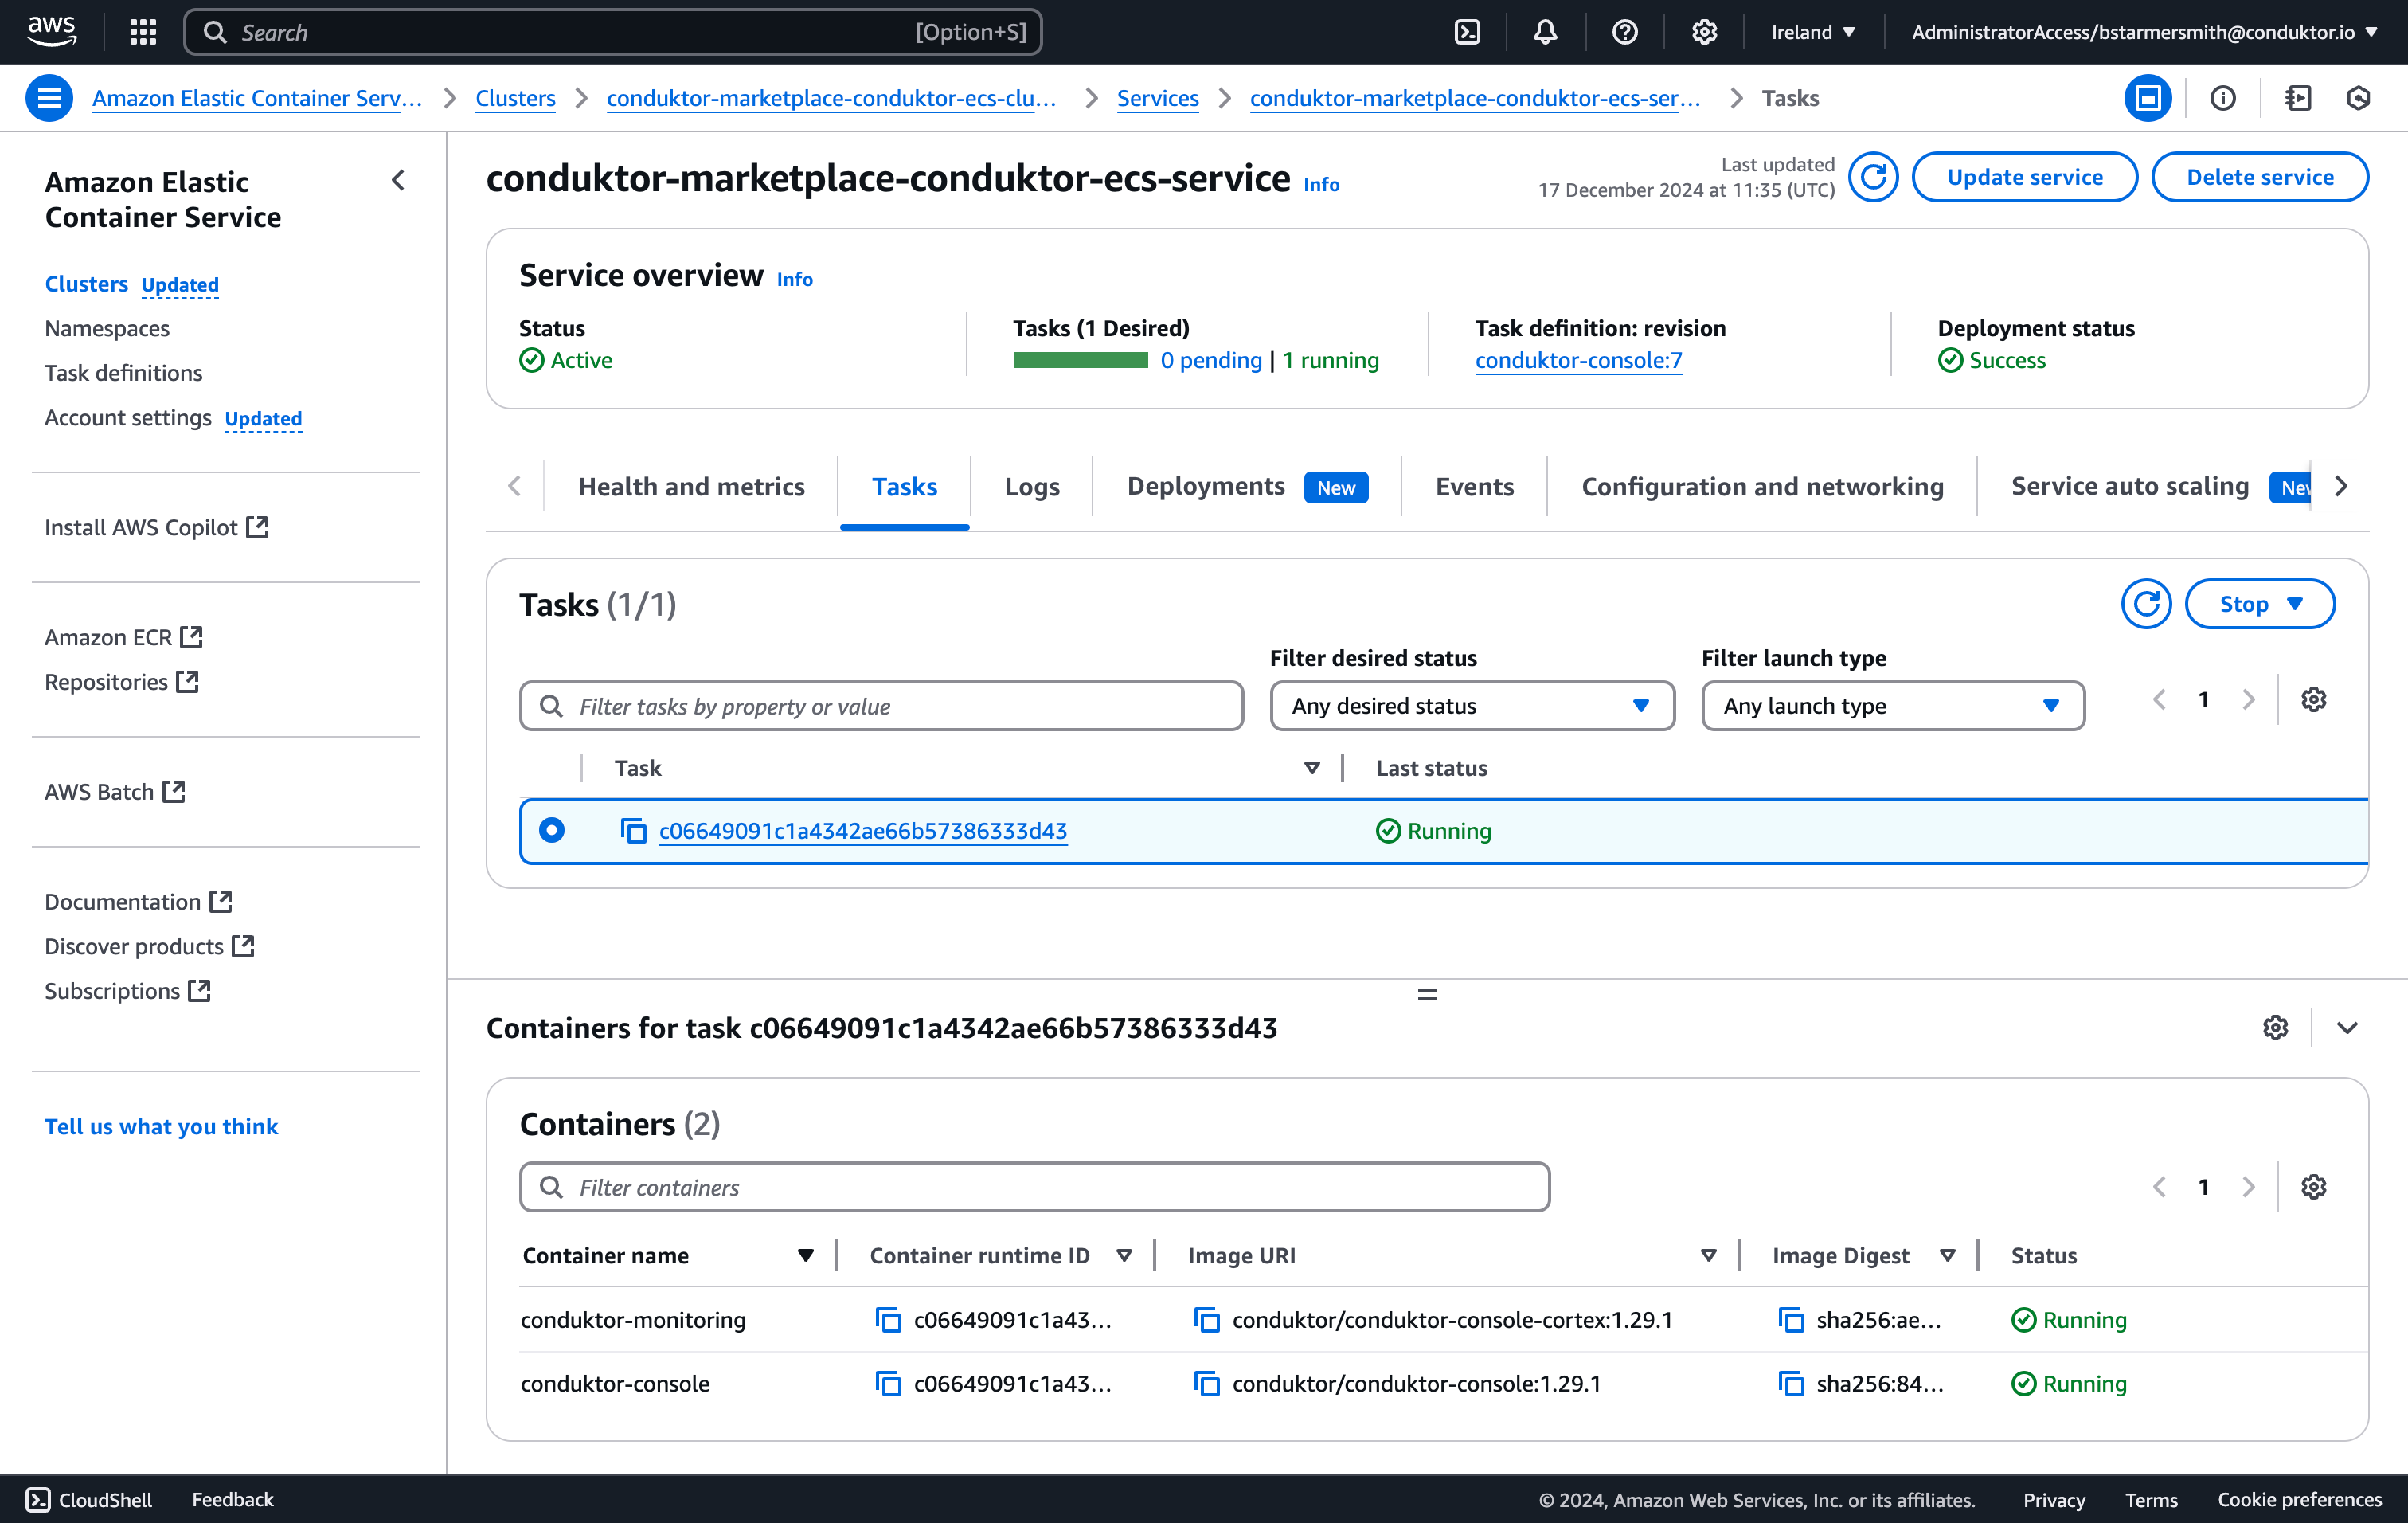
${AWS::StackName}-conduktor-ecs-cluster. From Cluster, navigate to your newly created Service and then to the Task. Be sure to click on the links.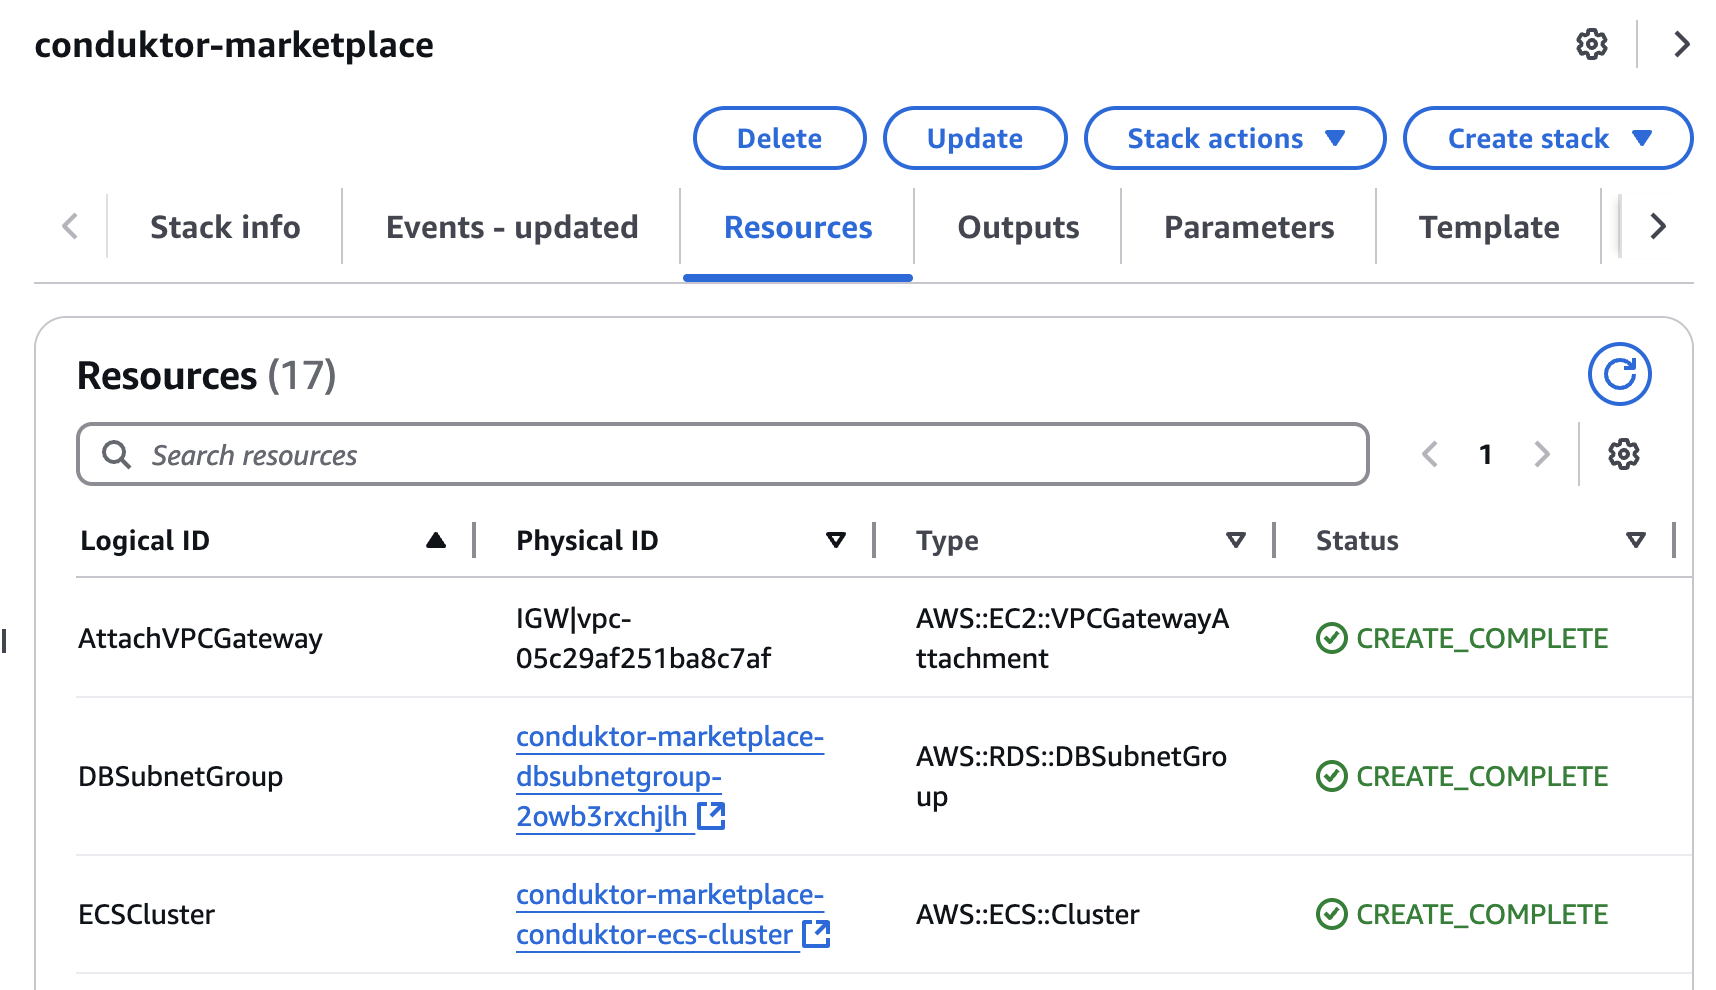
-
Find the
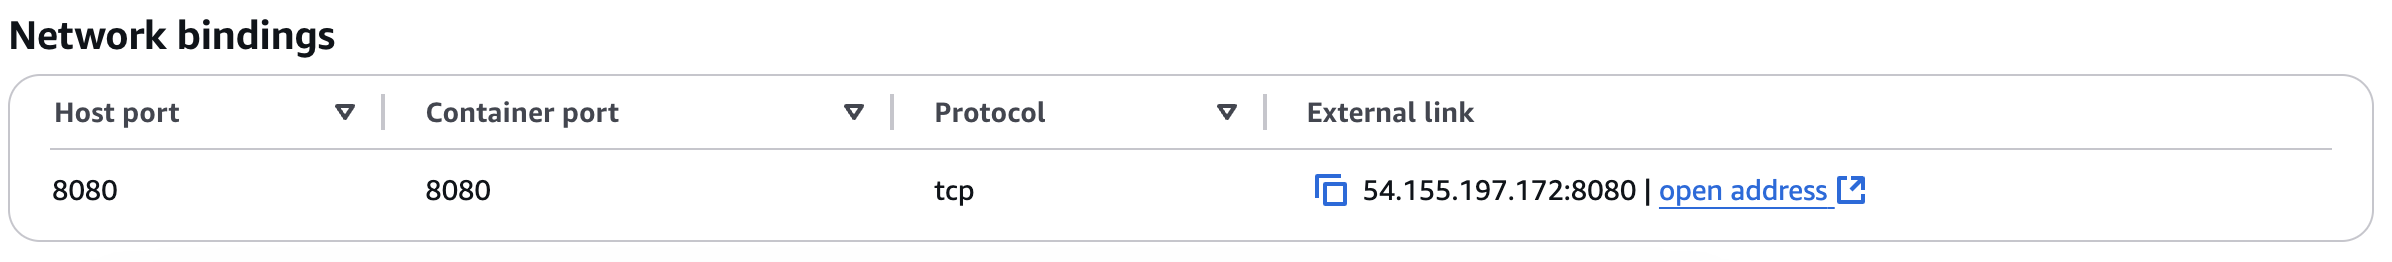
conduktor-consoleContainer and (not the conduktor-console-cortex one) and navigate to the Network bindings tab.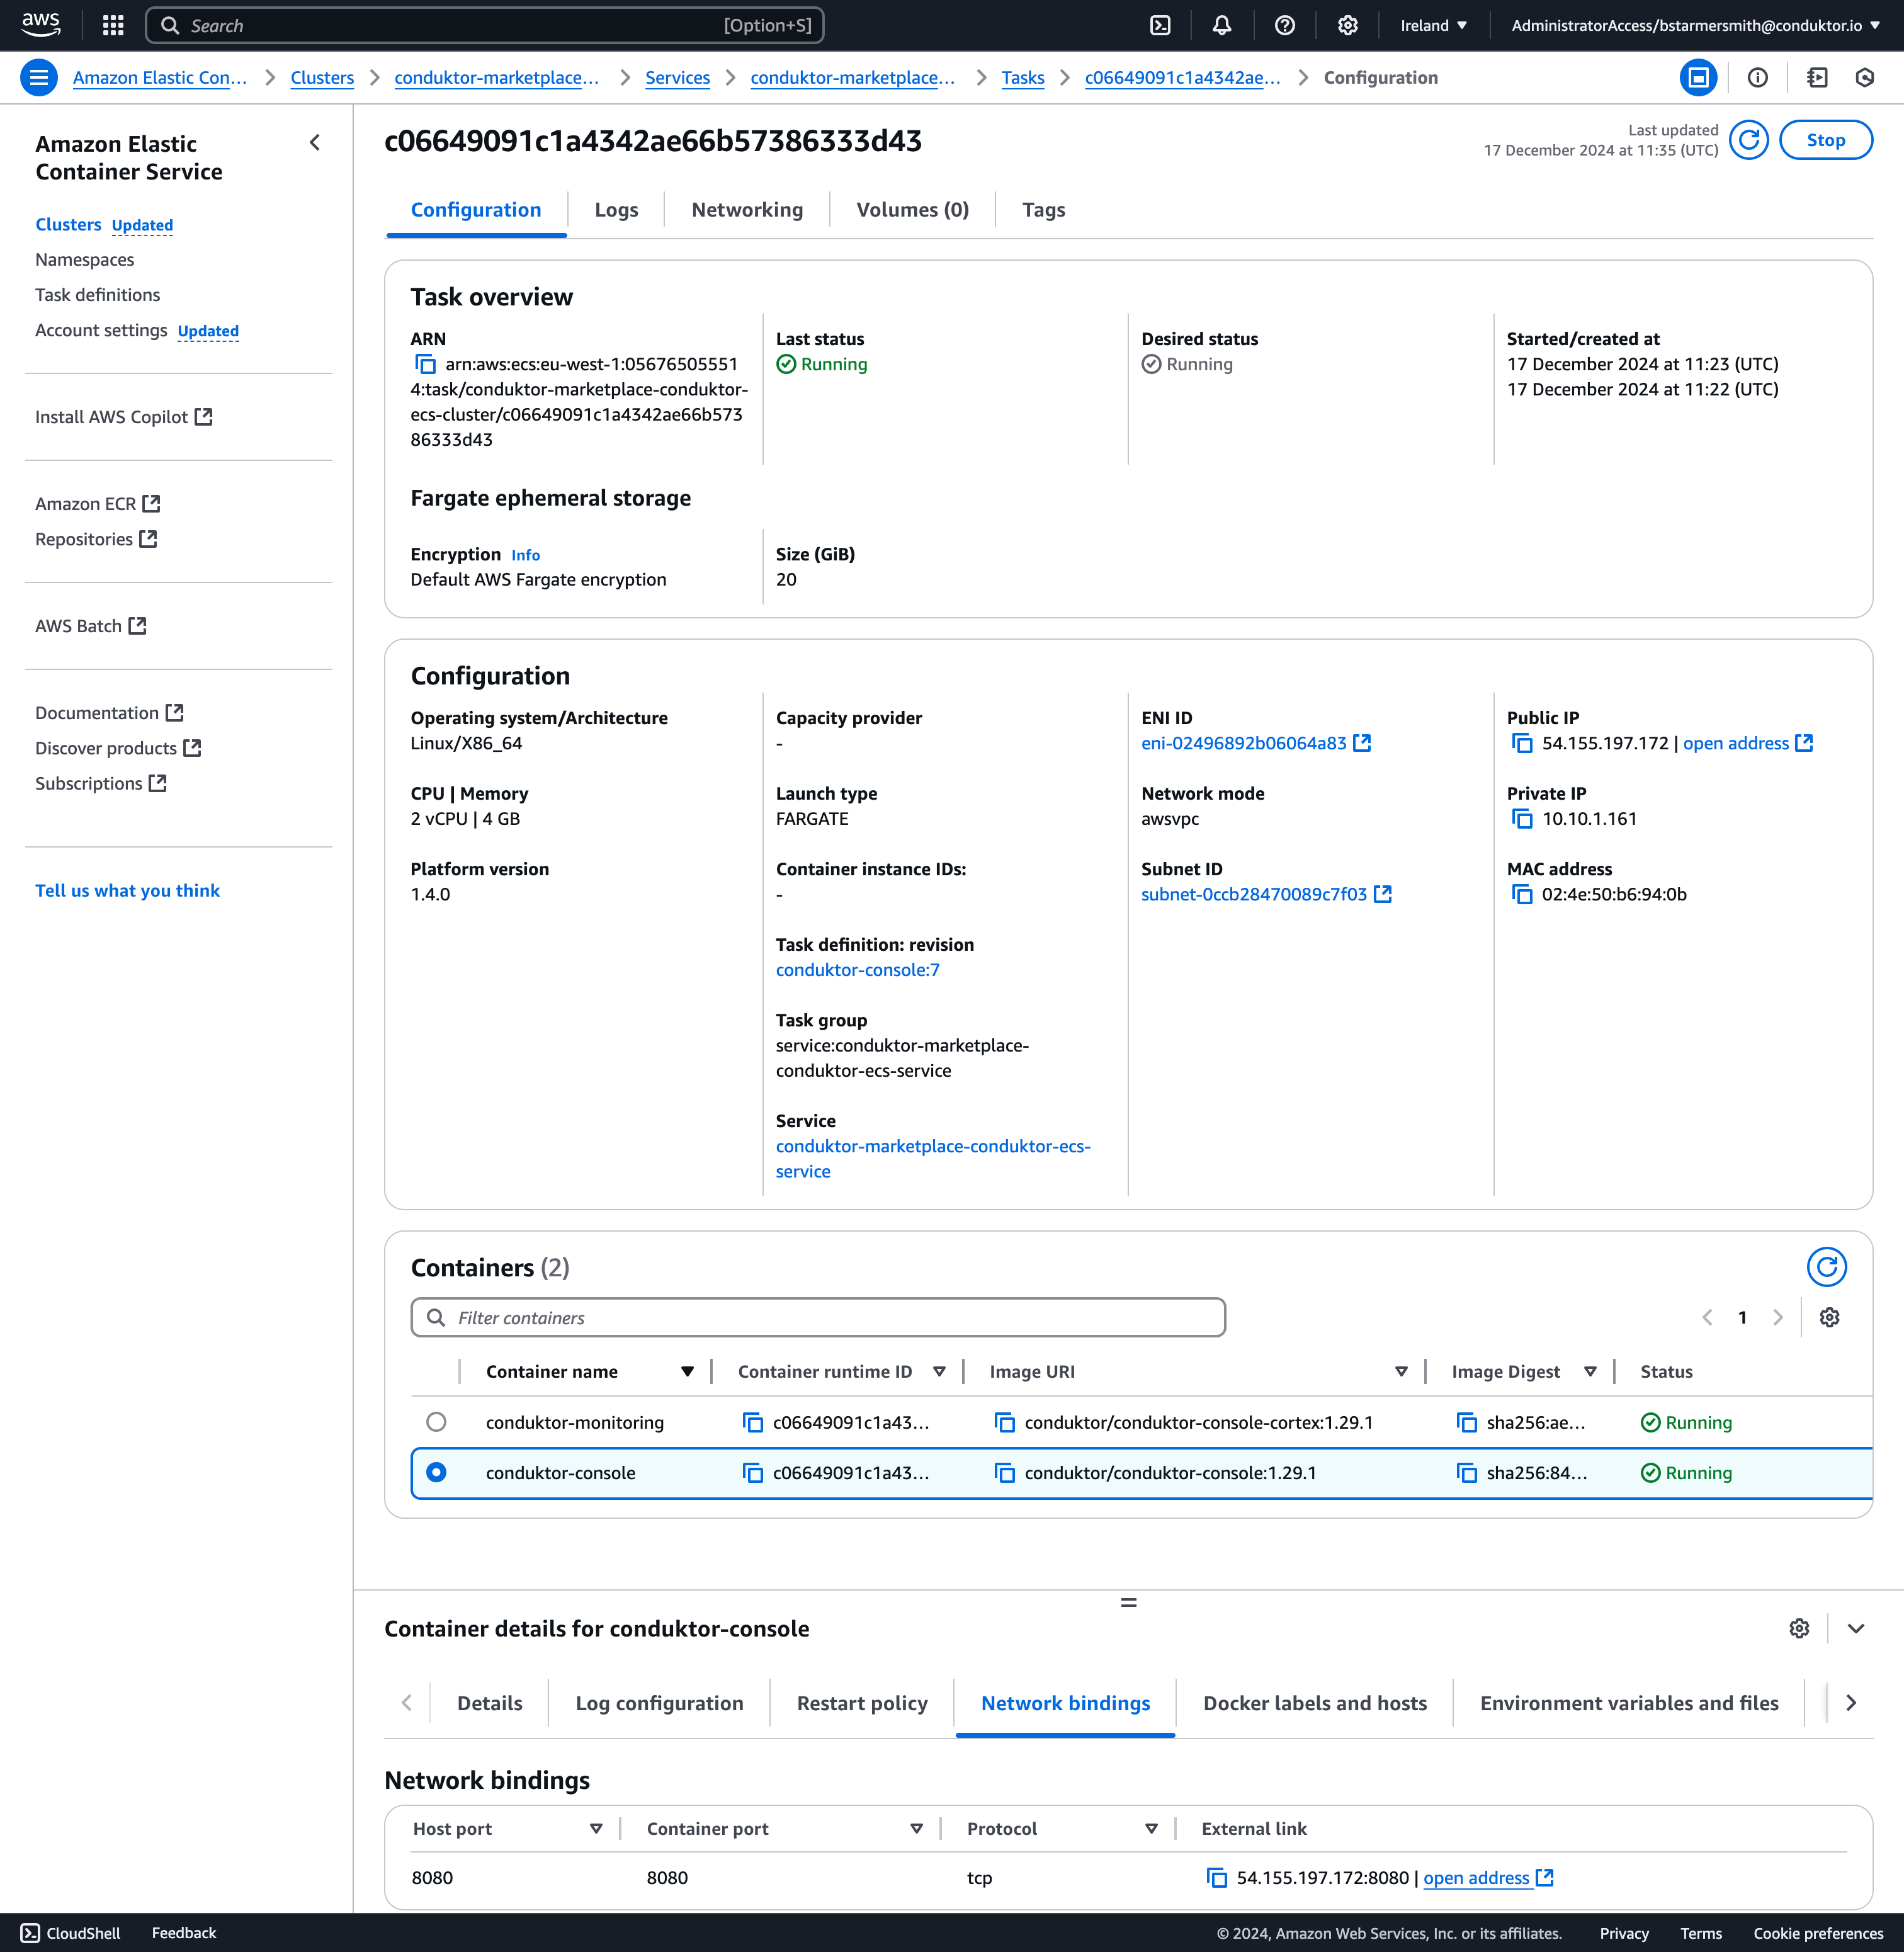
-
Click on the External link to open the Console application. In this example, our application is running at 54.155.197.172:8080.
Access Conduktor
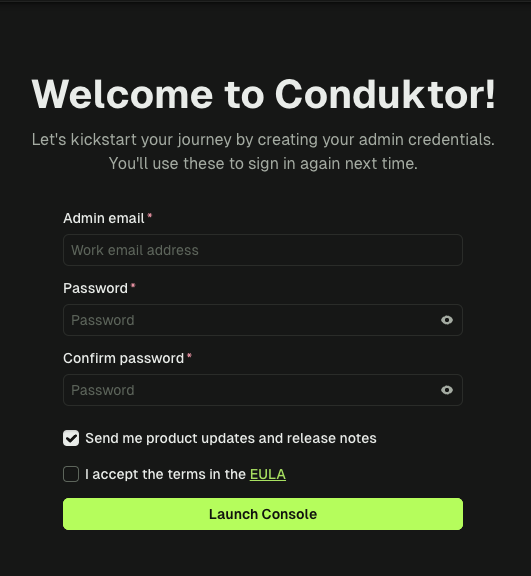
You will now be greeted with the create admin login. Create credentials and make a note/save them as they are for this instance. If lost, Conduktor cannot remotely reset these credentials. From here, you can add additional local users if needed. When you’re ready for a production level deployment, you’ll want to connect to SSO for importing your organization’s existing users and groups.