

- Breaking changes
- Preview features
- New and updated features
- Behavior changes
- Quality of life improvements
- Fixes
- Security advisories
Breaking changes
The MCP server no longer accepts admin API keys
The Conduktor Model Context Protocol (MCP) server now only accepts personal access tokens and machine identities. Admin API keys and application instance API keys are refused with a401 Unauthorized response. An admin API key holds every permission in Console, which is more than an AI assistant should be given.If you connected an MCP client with an admin API key, replace it before you upgrade: a machine identity with only the permissions the client needs is best practice. Personal access tokens can still be used, but should be limited to local personal experimentation use cases.The Console API and the CLI still accept admin API keys.Find out how to connect an AI assistant to Conduktor MCP.The list-interceptors MCP tool is removed
We removed the list-interceptors tool from the MCP server, so MCP clients can no longer call it. To see the Interceptors deployed on a Gateway cluster, use the Interceptors tab of the Kafka Gateway page.Preview features
Agents
Conduktor Agents are now available to all users with permissions and are turned on by default. This release adds:Permissions for agents. Agents are no longer limited to Console administrators. Four new permissions, which you assign to users and groups in their Service access tab, control who can use them: Can view Agents, Can manage and run Agents, Can view Agent identities and Can manage Agent identities.- To run or enable an agent you have to own its machine identity or be an administrator.
- Only the user who owns an agent’s identity can edit the agent. An agent’s identity can’t be changed after it’s created.
- Administrators and the agent’s owner can open the agent’s outputs, and this access is subject to a full RBAC check.
- Click Run once on an agent’s page to run a scheduled agent straight away.
- A run that finds nothing to act on now ends with a No action needed result, instead of an approval or a recommendation to review.
- The Models page shows how many agents use each model connection, and flags agents that still point to a connection you removed.
- Without a model connection, Console doesn’t queue any agent run, and creating an agent tells you to configure a model first.
- Machine identities can still be used for MCP calls without a configured model connection.
Client metrics
Console now reads the metrics Kafka clients push through Kafka Improvement Proposal 714 (KIP-714), via Gateway or your brokers and an OpenTelemetry Collector. It groups them by service account, flags clients that need attention, such as chatty producers, silent retries, unstable consumer groups or unowned clients, and suggests client settings. Client metrics is turned off by default.Find out how to set up and use client metrics.Ask
Ask is an assistant that opens in a panel next to any Console page. Open it from the top bar or withCmd+J (Ctrl+J on Windows and Linux), and ask about your Kafka platform in plain language. Ask answers with Console’s own tools, under your permissions, and with the Conduktor documentation. It can read and work with the page you have open, and run the tasks of the agents catalog on demand.- Attach, paste or drop up to four screenshots with a question.
- Choose which model connection answers.
- The next steps that Ask suggests only link to Console pages its tools returned and to documentation pages.
interactive_agents.enabled: true (CDK_INTERACTIVEAGENTS_ENABLED=true). In this release, only Console administrators can use Ask.Find out how to turn on Ask.New and updated features
Search across Console with the command menu
PressCmd+K (Ctrl+K on Windows and Linux) on any page, or click the search field in the top bar, to open the command menu. Search for topics, consumer groups, subjects, connectors, applications, users and groups across all your clusters, or jump to a Console page. Results only include the resources you have permission to see.The menu opens filtered to the kind of resource on the current page, such as topics when you’re on a topic. Press Backspace in the empty search field to search everything. A search starts once you’ve typed three characters, and the menu lists the resources you viewed recently.Global search is turned on by default. To turn it off, set global_search.enabled: false (CDK_GLOBALSEARCH_ENABLED=false). Find out how to configure global search.Change topics, subjects and connectors through MCP
The Conduktor MCP server now has new tools that let an AI assistant create or change resources, with the permissions of the token it connects with:- apply-topic: create a topic or change its configuration overrides.
- apply-subject: register a new schema version, creating the subject if needed, or change the subject’s compatibility.
- apply-connector: create a Kafka Connect connector or change its configuration.
dryRun to false, Console checks permissions, policies and validity, returns the changes and writes nothing. The preview of a topic change warns when it can delete records, and secret values are redacted in connector changes.These tools are for MCP clients. Conduktor Agents don’t use them in this release.Find out more about Conduktor MCP tools.Control which tokens can reach the MCP server
Two new settings let you control whether users can issue personal access tokens, and if they can whether these can be used for the MCP server endpoints. If enabled, personal access tokens are always valid on the Console API. Disabling personal access tokens for the MCP server will mean only machine identities can be used to access the Console MCP.To turn the MCP server off altogether, setenable_mcp: false (CDK_ENABLE_MCP=false).Find out how to choose which tokens MCP accepts and how to turn off MCP.Import user attributes from your identity provider
Console can now copy extra attributes from your identity provider onto each Console user, such as a department or a cost center. List the claims to import withimported-claims (OIDC) or the attributes with imported-attributes (LDAP). Console refreshes them, and the user’s first and last name, at each login.The attributes are returned by the users API to users with the userView permission and to the user themself. Find out how to import user attributes.Show JSON fields as columns when you consume a topic
On the topic Consume tab, turn on Value fields to replace the Value column with one column per field of the JSON value. Console starts with the top-level fields that every record has. Open the field settings to search the field tree and pick other fields, including nested ones. Console remembers your selection for each topic in your browser. Values that aren’t JSON objects stay in the Value column.Find out more about browsing records.Behavior changes
Agents are turned on by default
Theenable_agents setting now defaults to true. After the upgrade, administrators see the toggle at the top of the sidebar that switches from Console to Agentic, with a Preview badge. Agents don’t run until you configure a model connection.To hide the agents UI and API, set enable_agents: false (CDK_ENABLE_AGENTS=false). See what’s new for Agents in this release.Stricter permission checks
Two operations now check a permission they didn’t check before, so users who relied on the previous behavior get a permission error:- To reset a consumer group’s offsets on a topic the group has no committed offsets for, you now need permission to view that topic, as well as permission to reset the consumer group. Resetting the topics the group already has offsets for still only needs the permission on the group.
- To reset a subject’s compatibility to the Schema Registry’s global level, you now need the permission to edit the subject’s compatibility, as you already did to set it.
Console checks license limits at startup
Console now counts the users and clusters that already exist before it creates the local users and clusters declared in your configuration. If the total goes over a hard limit of your license, Console stops at startup with a message that names the limit. Check the Console logs if an instance doesn’t start after the upgrade.Database connections have a socket timeout
Console now opens its PostgreSQL connections withsocketTimeout=900, tcpKeepAlive=true and keepaliveTime=300000 by default. A connection that the network dropped silently is now closed and replaced instead of holding a slot in the pool until Console restarts. As a result, a single statement that runs for more than 15 minutes now fails. Database migrations at startup aren’t affected.To change these values, set them in the database properties.Quality of life improvements
Configurable timeouts
Console now puts a time limit on the calls it makes to Kafka, Schema Registry, Kafka Connect, Confluent Cloud, Gateway and its own database during indexing and other background work. A call that never returns can no longer stall indexing for a cluster or leave Console waiting until it’s restarted. An instance also gives up its leader role when it can’t renew it in time.The defaults suit most deployments. Raise a value if the logs show timeouts against a slow or distant system.Find out how to tune them in the timeout properties.Turn off the latest version check
To show when a newer release is available, the Console UI askscdn.conduktor.io for the latest version from the user’s browser. In environments without internet access, set enable_latest_version_check: false (CDK_ENABLE_LATEST_VERSION_CHECK=false) to stop these requests. See the global properties.Limit concurrent live consume sessions
You can now cap how many live consume sessions run at the same time, per instance and per user, so a burst of consume activity can’t take a large share of an instance’s resources. Both limits are off by default, so upgrading changes nothing until you set one.You may find this useful if a high volume of users consume topics in Console. Read more in the guide, and see the consume rate limit settings.Faster permission checks
Console’s permission system (role-based access control, or RBAC) answers who can do what. A round of performance work means the majority of API calls should feel faster.Other improvements
- Topic consume is faster and uses less memory, most noticeably on topics with large records.
- The Members list loads faster in organizations with thousands of users.
- New users see a short welcome flow the first time they sign in. Existing users aren’t shown it.
- A dry run of a connector, from the CLI, the API or MCP, now validates the configuration with Kafka Connect.
- Service account errors are clearer: linking a service account that already belongs to another application instance explains the conflict, and ACL validation errors no longer suggest
Unknownas a valid value. - Durations, sizes and other Kafka settings that hold a special value, such as
-1for unlimited, are now shown as such instead of as a quantity like0ms.
Fixes
- Fixed topic sizes not being recorded for idle topics on Confluent Cloud, and changes to a broker’s host, port or rack not being picked up
- Fixed Flink statements being refused when the same Confluent Cloud cluster is registered twice in Console
- A topic deleted while Console indexes a cluster no longer fails that cluster’s topic and consumer group lag indexing, or fills the logs with warnings
- The consumer group list no longer stays on Indexing in progress when a topic has partitions without a leader
- Improved indexing of Confluent Cloud ACLs and role bindings to batch calls to the Confluent Cloud APIs to reduce the likelihood of a time out on the indexer run
- Fixed assuming an AWS Identity and Access Management (IAM) role for Amazon Glue when the region is set in Console but not in the environment
- Checking a server’s TLS certificate no longer hangs when the server doesn’t answer the handshake
- Fixed a live consume that stops at the latest offset failing intermittently with an error
- Tightened the validation of the redirect address at the end of a single sign-on (SSO) login
- Creating several users at once no longer leaves a user created but outside the organization when the batch goes over the license’s user limit
- Fixed the Topic Size column of the Insights topic catalog showing a number of messages as a size, and topics with unlimited retention showing a retention of zero days
- Insights percentage tiles no longer round a small share to 0% or a large one to 100%, and their risk badges match the value
- Byte sizes are shown with three significant digits, so 1.5 GiB is no longer rounded to 2 GiB
- Fixed chart axis units, bar heights, heatmap colors and stacked totals that didn’t match the underlying numbers
- Fixed the search in ksqlDB tables showing No data found for rows that match
Security advisories
Application instance API keys could change application groups across environments
An application instance API key is scoped to one environment of a Self-service application, such asorders-dev. Before this release, that key could create and change application groups, and an application group grants permissions on any instance of its application. So a key issued for a development environment could grant access to a production environment of the same application.This release adds an application API key as the correctly scoped credential for managing application groups from continuous integration (CI), a diagnostic under Settings > Diagnostics > App group security to check whether an instance key reached beyond its environment, and an opt-in application_group_strict_security setting that stops instance keys changing application groups. The setting is off by default, so upgrading changes nothing until you turn it on.Action required: you’re only affected if application owners have distributed instance keys to lower-privileged environments where those keys also manage application groups. Run the diagnostic, move affected pipelines to application API keys, then turn on strict security. See Secure application groups across environments for the full guide.- Breaking changes
- Behavior changes
- Topic ID support is now on by default
- Changes to topic views
- The large message Interceptor downloads S3 objects by part number
- Gateway blocks more cluster administration APIs
- Topic policies skip rules on configs Kafka ignores
- Topics hidden by Gateway ACLs return an authorization error
- Internal load balancing keeps each client on one Gateway node per broker
- New and updated features
- New topic view SQL features
- New KMS provider: Thales CipherTrust Manager
- Vault Kubernetes authentication on a custom mount path
- The alter topic config policy covers the same configs as the create topic policy
- Large message Interceptor for heavier traffic
- Internal load balancing in more deployments
- Keep the HTTP management API off public networks
- Preview features
- Quality of life improvements
- Fixes
- Security advisories
Breaking changes
Legacy network configuration has been removed
The legacy network configuration, deprecated in v3.20.0, has been removed. Gateway now doesn’t start if any of these environment variables is set, and logs which ones it found:GATEWAY_PORT_START, GATEWAY_PORT_COUNT, GATEWAY_BIND_HOST, GATEWAY_ADVERTISED_HOST, GATEWAY_HOST, GATEWAY_ADVERTISED_SNI_PORT, GATEWAY_ROUTING_MECHANISM, GATEWAY_SECURITY_PROTOCOL, GATEWAY_SSL_CLIENT_AUTH, GATEWAY_ADVERTISED_HOST_PREFIX, GATEWAY_SNI_HOST_SEPARATOR, GATEWAY_TENANT_IN_HOSTNAMESQL topics and CEL topics Interceptors have been removed
These Interceptors have been removed in this release. We deprecated SQL topics in v3.19.0 and CEL topics in v3.17.0:- SQL topics (
io.conduktor.gateway.interceptor.VirtualSqlTopicPlugin) - CEL topics (
io.conduktor.gateway.interceptor.CelTopicPlugin)
UNKNOWN_TOPIC_OR_PARTITION.Replace each Interceptor with a topic view, then delete the old one, preferably before you upgrade. See the migration steps for SQL topics and CEL topics, and delete a removed Interceptor for how to remove them.context. is reserved in topic view SQL
Gateway now reserves the context. prefix in a topic view statement, whatever case it’s written in. Before this release, such a path read a field in the record’s value.A stored view that uses one now filters on the consumer instead of the record, and doesn’t load at all if the path isn’t a supported client context value. To keep reading the record field, write it with the payload prefix as $.context.<name>.Check your views for a context. path before you upgrade. See filter by client context. Service accounts move to a new storage topic
Gateway now stores service accounts in the_conduktor_${GATEWAY_CLUSTER_ID}_serviceaccounts topic instead of _conduktor_${GATEWAY_CLUSTER_ID}_usermappings.You’re affected if you create Gateway’s internal topics yourself and Gateway’s Kafka user can’t create topics. Gateway creates this topic at startup, and fails to start if it can’t. Create it before you upgrade, with the required topic configuration. If you enabled SCRAM credentials on v3.21.0 or v3.22.0, the topic already exists.If you enabled SCRAM credentials on v3.21.0 or v3.22.0, SCRAM no longer needs GATEWAY_FEATURE_FLAGS_SERVICE_ACCOUNTS, but keep it set as long as you might roll back. Without it, the earlier version can’t read SCRAM credentials and every SCRAM login fails. Gateway migrates service accounts automatically at startup. During a rolling upgrade, don’t create, update or delete service accounts or group memberships until every Gateway node runs v3.23.0. Before you upgrade, see how to migrate Gateway service accounts storage, including what a rollback does. Behavior changes
Topic ID support is now on by default
Topic ID support (Kafka Improvement Proposal 516 (KIP-516)) is now generally available and enabled by default. To keep the previous behavior, setGATEWAY_FEATURE_FLAGS_TOPIC_ID_SUPPORT to false. Changes to topic views
- Missing or unexpected values no longer trigger the view’s
onErrorsetting. Before, withFAIL_FETCH, consumers couldn’t read past these records. Gateway now filters the record out or serves the value asnull: see missing and null fields. - Gateway rejects more invalid SQL when you create or update a view, such as a number, date, time or timestamp compared with a different one of these. For example,
record.timestamp > {ts '2026-01-01 00:00:00'}compares a number with a timestamp. If a view stored by an earlier release has invalid SQL, correct its statement. Gateway may stop loading it after the upgrade, or reject it the next time you change it.
The large message Interceptor downloads S3 objects by part number
The large message Interceptor now downloads objects withGetObject requests that use partNumber by default. If your S3-compatible storage doesn’t support them, consumers can’t read offloaded records and Gateway logs Failed to download from cloud storage. To avoid this, set multipartEnabled to false once every Gateway node runs 3.23.0. Earlier versions reject an Interceptor configuration that contains it. Gateway blocks more cluster administration APIs
Gateway now rejects the Kafka APIs that manage the KRaft quorum or unregister a broker, whatever the value ofGATEWAY_FEATURE_FLAGS_BLOCK_UNSUPPORTED_APIS. Tools that rely on them, such as kafka-metadata-quorum, now fail through Gateway with UnsupportedVersionException. Run these operations directly against the backing cluster. Topic policies skip rules on configs Kafka ignores
The create topic and alter topic config policies now skip a rule when Kafka ignores the config the rule governs. What changes when you upgrade:- Gateway reads the topic’s current configs from Kafka. Gateway’s Kafka user needs
DescribeConfigspermission. If Gateway can’t read them, every rule applies, as before. - Some alters that used to succeed can now be rejected. For example, switching a topic’s
cleanup.policyfromcompacttodeletenow checks its existingretention.msagainst your rule, because Kafka starts using it. To pass the rule, set a validretention.msin the same alter.
Topics hidden by Gateway ACLs return an authorization error
With Gateway ACLs enabled, a client that asks by name or topic ID for a topic it isn’t allowed to describe now getsTOPIC_AUTHORIZATION_FAILED for that topic, as on Kafka. Before, Gateway left the topic out, as if it didn’t exist.As a result, a consumer that subscribes by name to a topic it can’t describe now fails on poll() with TopicAuthorizationException, where before it ignored that topic and read the others. Grant the consumer describe access on the topic or remove it from the subscription. Subscriptions by regular expression (regex) are unchanged. Internal load balancing keeps each client on one Gateway node per broker
With internal load balancing, the default strategy now gives each client the same Gateway node for a given broker. Before, the node could change between requests, which made non-Java clients, such as librdkafka and Sarama clients, drop connections and fail in-flight requests.To keep the previous behavior, set the newGATEWAY_INTERNAL_LOAD_BALANCING_STRATEGY to ROUND_ROBIN, or choose another assignment strategy. New and updated features
New topic view SQL features
Topic view statements support these new features:- Client context: a
WHEREcondition can now read what Gateway knows about the client making a fetch, such as its username, groups or OAuth token claims. One view can then serve different records to different consumers. See filter by client context. MEMBER OF: a new condition that matches a value against a list held in a record field or a context value, such asdesk MEMBER OF context.groups. See filter by a list.- Timestamps: topic views can now compare more kinds of timestamp, including a record’s own. See date and time values.
New KMS provider: Thales CipherTrust Manager
If your keys live in CipherTrust Manager, you can now use them to encrypt your Kafka data with Gateway, as you already could with AWS KMS, Azure Key Vault, GCP KMS, HashiCorp Vault and Fortanix. See how to configure it.Vault Kubernetes authentication on a custom mount path
If your Vault exposes Kubernetes authentication somewhere other thanauth/kubernetes, for example one mount per environment, Gateway can now log in to it. See how to configure it. The alter topic config policy covers the same configs as the create topic policy
You can now apply the same rules to topic changes as to topic creation, so users can’t bypass a creation rule by altering the topic afterwards. See how to configure it.Large message Interceptor for heavier traffic
- Tune the S3 connection pool and timeouts, and upload large objects in several parts, for large payloads or high throughput. See how to configure it.
- Run without a local disk: turn off the disk cache if you have no volume for it. See how to configure it.
Internal load balancing in more deployments
If your listeners use different advertised hosts, or your Gateway nodes use different port ranges for the same listener, you can now use internal load balancing. See how to configure it.Keep the HTTP management API off public networks
If a Gateway node has several network interfaces, you can now make the HTTP management API listen on only one of them, for example a private network. Before, it listened on every interface. See how to configure it.Preview features
KIP-848 consumer group protocol
Consumers can now use the KIP-848 consumer group protocol through Gateway, including on topics in Virtual Clusters, aliases and topic views. Requires Kafka 4.0 or later.The protocol is off by default. Find out how to enable it, and its prerequisites and limitations.Produce records over REST
Produce Kafka records withPOST /gateway/v2/topics/{topic}/records, without a Kafka client. Gateway produces as the caller, so the caller’s ACLs, Virtual Cluster and Interceptors apply. The request and response fields follow Confluent REST Proxy v3. Gateway serves the endpoint on its own listener, on port 8889 by default.The endpoint is disabled by default. Find out how to produce records over REST or see the API reference. Quality of life improvements
- Improved the performance of field-level encryption and reduced its log noise.
- Steadier Vault sessions, with clearer errors: Gateway handles Vault outages and token problems better. While Vault is unavailable, produce errors and audit events say so.
Fixes
- Fixed requests on a topic view that changed the physical topic it reads. Requests such as delete topic, add partitions or change configs now fail with
INVALID_TOPIC_EXCEPTION. - Fixed listing consumer groups when Gateway ACLs are enabled:
- Filtering by state, for example
kafka-consumer-groups --list --state Stable, no longer fails. - A user with an ACL allowing
DESCRIBEon the cluster now sees every group, as they would on Kafka, instead of only the groups their group ACLs cover.
- Filtering by state, for example
- Gateway now ends an OAUTHBEARER session when its token expires, as Kafka does.
- Fixed clients hanging without a response when a request failed in the Gateway.
- Fixed the Gateway admin API documentation page rendering blank.
- Improved the reliability and performance of the large message handling Interceptor:
- Tombstones (records with a
nullvalue) now pass through on produce. - Gateway uses less memory when it fetches large records. To stop a fetch of many offloaded records running Gateway out of memory, turn on
GATEWAY_FEATURE_FLAGS_LARGE_MESSAGE_FETCH_CEILING(preview). - A missing offloaded object now fails the fetch instead of being served as an empty value. See recover from a missing offloaded object.
- Tombstones (records with a
- Fixed Gateway writing authorization failure events for requests that more than one permission allows, when the client had only one of them. For example, a producer starting with
WRITEon a topic but noIDEMPOTENT_WRITEon the cluster. - Fixed field-level decryption of Avro records changing the values of some unencrypted fields, for example setting nullable enum fields to
null. - Fixed several issues in traffic control policies:
- Consumer group policy: the
rebalanceTimeoutMsrule now works withaction: OVERRIDE. - Create topic and alter topic config policies: an
OVERRIDErule on a boolean ormessageTimestampTypeconfig now always sets the rule’svalue. - Produce policy:
acceptTimestampInFuture: falsenow blocks only records stamped in the future, and applies its configured action. - Producer rate limiting and limit commit offset policies now throttle clients that are far over their limit.
- Fetch policy: a
versionrule withaction: THROTTLEnow throttles. - Topic required schema ID policy: a record without a schema ID now triggers the action wherever it is in the produce request.
- Consumer group policy: the
- Fixed the schema payload validation policy blocking every record when an Avro schema uses
exclusiveMinimumorexclusiveMaximum. - Fixed the SQL data quality producer policy throttling valid produces.
Security advisories
This release resolves CVE-2026-90559 (snappy-java).The
token command now supports Application tokens: create them with an optional --expires-at expiry, list them and revoke them with token revoke. Revoking only applies to Application tokens; other token kinds can only be deleted.Find out more.Security advisories
This release resolves CVE-2026-114938 (Java4Shell), a heap buffer overflow in the Java Virtual Machine (JVM) Base64 decoder that can crash Schema Registry Proxy and, under some conditions, allow remote code execution. Schema Registry Proxy now runs on a Java runtime with the fix.Are you impacted?You’re impacted if you run Schema Registry Proxy 1.0.1 or earlier on x86-64 (Intel or AMD) processors. Schema Registry Proxy on Arm (aarch64), such as AWS Graviton, isn’t impacted.What to doUpgrade to Schema Registry Proxy 1.0.2. If you can’t upgrade yet, add-XX:-UseBASE64Intrinsics to JAVA_TOOL_OPTIONS and restart Schema Registry Proxy. This mitigates the vulnerability but your security scanner will still flag the Java runtime. See how to apply and verify the mitigation.Security advisories
This release resolves CVE-2026-114938 (Java4Shell), a heap buffer overflow in the Java Virtual Machine (JVM) Base64 decoder that can crash Gateway and, under some conditions, allow remote code execution. Gateway now runs on a Java runtime with the fix.Are you impacted?You’re impacted if you run Gateway 3.22.3 or earlier on x86-64 (Intel or AMD) processors. Gateway on Arm (aarch64), such as AWS Graviton, isn’t impacted.What to doUpgrade to Gateway 3.22.4. If you can’t upgrade yet, setJAVA_TOOL_OPTIONS=-XX:-UseBASE64Intrinsics and restart Gateway. This mitigates the vulnerability but your security scanner will still flag the Java runtime. See how to apply and verify the mitigation.Security advisories
This release resolves CVE-2026-114938 (Java4Shell), a heap buffer overflow in the Java Virtual Machine (JVM) Base64 decoder that can crash Console and, under some conditions, allow remote code execution. Console now runs on a Java runtime with the fix.Are you impacted?You’re impacted if you run Console 1.48.1 or earlier on x86-64 (Intel or AMD) processors. Console on Arm (aarch64), such as AWS Graviton, isn’t impacted.What to doUpgrade to Console 1.48.2. If you can’t upgrade yet, setCONSOLE_JAVA_OPTS=-XX:-UseBASE64Intrinsics and restart Console. This mitigates the vulnerability but your security scanner will still flag the Java runtime. See how to apply and verify the mitigation.Security advisories
CVE-2026-111943 — eMudhra CA key compromise
There are no code changes in this release.On October 20, Mozilla disclosed that the private keys of eight eMudhra intermediate certificate authorities were compromised (CVE-2026-111943). Any system trusting those CAs could accept fraudulently issued certificates.This release rebuilds the Schema Registry Proxy image on an updated base image that removes the affected eMudhra root certificates from the CA bundle, so Schema Registry Proxy no longer trusts certificates issued by the compromised CAs.Who is affected: all Schema Registry Proxy versions prior to this release running with default TLS settings.Action required: upgrade to this release. If you maintain a custom CA truststore derived from the Schema Registry Proxy image’s certificate bundle, regenerate it from the updated image.Security advisories
This release resolves CVE-2026-91403 (eMudhra certificate authority compromise, also tracked as CVE-2026-111943 and CVE-2026-114406):- Gateway now runs on Java Runtime Environment (JRE) 25.0.5.0.2, which blocks the compromised intermediate certificates whatever truststore a connection uses, including truststores you set yourself. Its default truststore also no longer includes eMudhra’s
emSign ECC Root CA - G3root certificate. - Google API Client for Java, which the GCP Key Management Service (KMS) client uses, is upgraded to 2.9.2. It now checks the default JRE truststore first, and its bundled fallback no longer trusts the compromised certificates.
- Connect Gateway to Kafka over Transport Layer Security (TLS) without setting a truststore (
KAFKA_SSL_TRUSTSTORE_LOCATIONorKAFKA_SSL_TRUSTSTORE_CERTIFICATES) - Authenticate Gateway to Kafka with OAUTHBEARER without setting
ssl.truststore.locationinKAFKA_SASL_JAAS_CONFIG - Connect an Interceptor to a schema registry over HTTPS without setting
schema.registry.ssl.truststore.locationin itsschemaRegistryConfig.additionalConfigs - Use a HashiCorp Vault KMS external connection without setting its
TRUST_STORE_PATH - Use AWS, Azure, Fortanix or GCP KMS
- Offload large messages to Amazon S3 or Azure Blob Storage
- Use Gateway-managed OAUTHBEARER authentication with an HTTPS JWKS (JSON Web Key Set) URL
- Set
GATEWAY_PRINCIPAL_RESOLVERtoCONFLUENT_CLOUD
-Djavax.net.ssl.trustStore in JAVA_OPTS, also leaves you impacted if it includes emSign ECC Root CA - G3 or Sectigo’s AAA Certificate Services.
This is likely if you built it from a copy of a Java Development Kit (JDK) default truststore. Gateway 3.22.3 blocks the compromised intermediate certificates even when your truststore includes these roots.If you run Gateway 3.22.2, you’re still impacted if you use GCP KMS.What happened?The private keys of several eMudhra intermediate certificate authorities were compromised.
An attacker holding these keys and able to intercept Gateway’s connections could impersonate the servers Gateway connects to.
With Kafka, schema registry, KMS or storage traffic intercepted, the attacker could read or alter your data and encryption keys.The identity endpoints carry extra risk:- A spoofed JWKS endpoint would let the attacker forge tokens that Gateway accepts with Gateway-managed OAUTHBEARER authentication, and so impersonate any service account, with its Virtual Cluster, access control lists (ACLs) and Interceptor policies
- A spoofed OAuth token endpoint would expose the client credentials Gateway uses to authenticate to Kafka
- A spoofed Confluent Cloud API would expose your Confluent Cloud API key and secret, and could map a client to another Gateway service account, applying that account’s Interceptor policies instead of its own. Kafka ACLs still apply to the client’s real identity.
Security advisories
CVE-2026-111943 — eMudhra CA key compromise
There are no code changes in this release.On October 20, Mozilla disclosed that the private keys of eight eMudhra intermediate certificate authorities were compromised (CVE-2026-111943). Any system trusting those CAs could accept fraudulently issued certificates.This release rebuilds the Console image on an updated base image that removes the affected eMudhra root certificates from the CA bundle, so Console no longer trusts certificates issued by the compromised CAs.Who is affected: all Console versions prior to this release running with default TLS settings.Action required: upgrade to this release. If you maintain a custom CA truststore derived from the Console image’s certificate bundle, regenerate it from the updated image.Security advisories
This release partially resolves CVE-2026-91403 (eMudhra certificate authority compromise, also tracked as CVE-2026-111943 and CVE-2026-114406) by moving to Java Runtime Environment (JRE) 25.0.5, whose default truststore no longer includes eMudhra’semSign ECC Root CA - G3 root certificate.
GCP Key Management Service (KMS) and truststores you set yourself can still trust the compromised certificates.Security advisories
Critical: OAUTHBEARER identity spoofing in Kafka-managed mode
Are you impacted?You’re impacted if all of these apply:- You run Gateway 3.8.0 to 3.22.0
- Gateway runs in Kafka-managed security mode:
GATEWAY_SECURITY_MODE: KAFKA_MANAGED, or the deprecatedDELEGATED_SASL_PLAINTEXTandDELEGATED_SASL_SSLsecurity protocols - Clients authenticate with the OAUTHBEARER SASL mechanism
- You rely on per-identity Interceptor policies, such as field-level encryption or data masking
- New and updated features
- More tools for the Conduktor MCP server
- Produce records with a schema GUID in their headers
- See your Gateway deployment from Console
- See Self-service ownership on the topic details page
- Turn off Insights for your organization
- Approved access requests show the granted permissions
- Service accounts no longer have a Quotas tab
- Deprecated features
- Quality of life improvements
- Fixes
New and updated features
More tools for the Conduktor MCP server
The Conduktor Model Context Protocol (MCP) server now has 31 tools, up from 12. AI assistants can read topic configurations and individual records, schemas and compatibility checks, consumer group members and offsets, Kafka Connect connectors, Access Control List (ACL) bindings and service accounts, stream lineage, Self-service applications, Chargeback, the audit log and trusted certificates. The new set-topic-labels tool is the first that changes data: it adds or updates labels on a topic.The existing tools return smaller, paged responses. The Insights tools are only available when Insights is enabled.Find out more about Conduktor MCP tools.Produce records with a schema GUID in their headers
Console 1.47.0 started reading records that reference their schema with a globally unique identifier (GUID) in the record headers. Console now writes them too. When you produce an Avro or JSON Schema record with a Confluent Schema Registry, set Write schema identity in to Record header instead of Payload prefix. Console writes the GUID to the reserved__key_schema_id or __value_schema_id header and leaves the payload unprefixed. The subject needs a GUID, which requires Confluent Schema Registry 8.0 or later. Protobuf records are still produced with a payload prefix from the UI.When you re-process a record that carries a schema GUID header, Console keeps the header format. The GUID is also shown on the subject details page, in the subject list, in the consumed record details and in the produced messages panel.Find out more about schema IDs in record headers.See your Gateway deployment from Console
The Kafka Gateway page of a Gateway cluster now shows the Gateway version, the number of Interceptors and Gateway nodes, and the fleet state, across three tabs:- Gateways: the listeners with their protocol, routing and advertised addresses, the authentication mode, and each Gateway node with its admin endpoints. Node information requires Gateway 3.22 or later.
- Interceptors: the Interceptors deployed on the cluster. Create new ones from here.
- Settings: a read-only view of the Kafka cluster, provider and Gateway configuration, and the Gateway feature flags.
See Self-service ownership on the topic details page
For topics owned by an application instance, the topic details page now shows the owning application and instance, and a Public or Private badge for the topic’s visibility in the Topic Catalog. Click Public to open the topic in the Topic Catalog. The page also shows the topic’s description, which you can edit if you have permission to.Turn off Insights for your organization
You can now disable Insights for your whole organization with the newenable_insights setting (CDK_ENABLE_INSIGHTS environment variable). When it’s off, Insights and label insights are removed for all users, the MCP Insights tools are unavailable, and admins see a notice explaining how to turn Insights back on.Find out more about disabling Insights.Approved access requests show the granted permissions
In the Access requests tab of the Application Catalog, and on the application details page, approved requests now show the permissions that were granted, which can differ from the ones requested. Pending and declined requests still show the requested permissions.Service accounts no longer have a Quotas tab
We removed the Quotas tab from service accounts. It didn’t show quota data, only an invitation to register your interest in quota management. Service accounts now open on the ACLs tab.Deprecated features
Kafka SQL
Kafka SQL is deprecated and will be removed by Console 1.51.0. The SQL pages now carry a Deprecated label.Quality of life improvements
Resource policy conditions are compiled when you save them
Console now compiles the Common Expression Language (CEL) conditions in a ResourcePolicy when you create or update it, instead of only checking their syntax. A condition that references an undeclared variable, such asold or a bare foo instead of spec.foo, is rejected with an Invalid policy error. Previously, these policies were saved and then rejected every create and update with the rule’s own error message, as if the resource broke the rule. If you apply policies through the CLI or Terraform, check that their conditions compile: re-applying an existing policy with an invalid condition now fails.Consumer group details in the public API
GET /public/v1/clusters/{clusterName}/consumergroups/{consumerGroup} now also returns the group’s members and its offsets and lag per partition in offsetPerPartition. The new fields are optional, so existing clients keep working. In the OpenAPI specification, the operation ID changed from consumer-group-stats to consumer-group-details and the response schema from ConsumerGroupStats to ConsumerGroupDetails, so regenerate any client you generated from it.New topics use the cluster’s default replication factor
When you create a topic in Console, the Replication factor field is now in Advanced configuration and is empty by default, so the topic gets the cluster’sdefault.replication.factor. Previously, Console set it to the lower of three and the number of brokers. Enter a value to override it. The replication factor is also optional in the Topic resource for the API, CLI and Terraform. Leave out spec.replicationFactor, or set it to -1, to use the cluster default. If Console can’t read default.replication.factor from the cluster, it rejects the topic and asks you to set the replication factor explicitly.Find out more about creating a topic.Other improvements
- Redesigned the Resource access tabs of users, groups and application groups. Each resource is a collapsible row that summarizes its read, write and manage permissions, and you can search and filter by permission, cluster and how the access was assigned.
- The Resource access tab, and the
/users/{userId}/v2/resourcesAPI, now only show inherited roles that are in effect for the user - Added headers to topic consume: show any header key as a table column, and filter records on a header key or value.
- Topic consume now shows its progress next to Records: the number of records consumed and matching your filter, and the elapsed time.
- Header values that aren’t valid UTF-8 are now shown as base64 instead of garbled text, and re-processing a record keeps them byte for byte.
- Added the Chargeback endpoints to the API reference.
- Added support for the Console Enterprise listing on AWS Marketplace.
Fixes
- Indexing now resumes automatically when the Console database comes back after an outage
- Testing a Confluent Cloud connection with credentials that can’t read organization details, such as Flink-scoped API keys, now reports that access was denied instead of a connection error
- Fixed connector actions (pause, resume, restart and delete) being unavailable to users with permissions on specific connectors. Bulk actions are offered when every selected connector allows them
- Access request and approval forms no longer ask for a service account permission when the target application instance has no service account
- Fixed a subject’s Schema tab staying blank, for example when you open it from a record’s schema link
- Opening a record that carries a schema GUID header no longer shows an error when Console looks up the subjects that use its schema
- Fixed outgoing access requests not appearing for users who can request access but not approve it
- Fixed owner groups created by the 1.45.0 migration getting connector permissions on the wrong Kafka Connect cluster when a Kafka cluster has several. Owner groups now get connector permissions on every Kafka Connect cluster of their Kafka cluster, and existing owner groups are repaired when Console starts
- Fixed connector permissions that differ only by Kafka Connect cluster being merged when an application group is read and applied again
- Fixed the does not contain and not equals header filters matching records that had any non-matching header. They now match records where no header matches, including records without headers
- Fixed consuming stopping early or never finishing on partitions that end with transaction markers, aborted records or compacted offsets
- The field list in Search in a specific field now populates when a consume doesn’t finish, such as on compacted topics, and no longer hangs on large records
- Fixed a blank screen after login with a
console-monthlylicense. Expiry warnings for this license start seven days before it expires
This is the first public release of Conduktor Schema Registry Proxy (SRP), a lightweight proxy that sits between your Kafka client applications and a Confluent-compatible schema registry. It exposes the same REST API the Confluent serializers and deserializers use, and adds authentication, per-subject authorization and observability: Prometheus metrics, OpenTelemetry tracing and structured JSON logs. Only Confluent-compatible schema registries are supported.SRP is explicitly and only a proxy for application clients — producers, consumers and their serializers and deserializers, plus read-only tooling — connecting to Schema Registry. It doesn’t implement the entire Confluent Schema Registry API and doesn’t support administrative operations: subject and schema deletion, compatibility and mode writes (
Deprecated in:
PUT/DELETE on /config and /mode) and schema-linking /exporters endpoints aren’t routed and return 404. For administrative work, use Conduktor Console, which connects to the Schema Registry directly to manage subjects, schemas and compatibility settings.The Docker image is conduktor/conduktor-schema-registry-proxy:1.0.0. See the deployment guide, the configuration examples and the environment variables reference to get started.If you run the 0.1.0-rc1 release candidate distributed to early-access users, read the breaking changes and fixes below before you upgrade.Breaking changes
A Conduktor license is now required
SRP now refuses to start without a valid license in theCDK_LICENSE environment variable. A Conduktor Scale or Gateway license is required — the same license token works for both.The license is checked once at startup and never during a run: a running proxy keeps serving after its license expires, and the next restart fails. License expiry is exported as the license_expiry_timestamp_seconds Prometheus metric (a Unix timestamp; not exported for licenses without an expiry), so you can alert before a restart would fail.AUTH_PROVIDER is now required
AUTH_PROVIDER no longer has a default — the release candidate fell back to a built-in testing provider when it was unset. SRP now refuses to start until you set it to jwt or basic. If you relied on the release candidate’s default, pick one of the two providers before you upgrade.New features
New authorization modes
The newAUTHORIZATION_MODE variable selects how SRP authorizes schema operations. The default stays reactive, matching the release candidate’s behavior. Each mode is documented in depth, with architecture diagrams, in the deployment guide’s authorization modes section.Every mode implements the same contract: there are only two permissions, Read and Write. Schema registration (POST /subjects/{subject}/versions) requires Write, every other proxied endpoint requires Read and a denial returns HTTP 403.reactive(default): permissions are managed in Conduktor Console with Self-service — Application Instances and Application Instance Permissions applied with the Conduktor CLI — and distributed to SRP over Kafka topics (_conduktor_srp_commandsand_conduktor_srp_events), with Console discovering SRP instances through heartbeats. Choose this when you run Console and want schema permissions managed centrally alongside your other Self-service resources, updated in real time without restarting the proxy.topic-acl(new, standalone): SRP authorizes schema operations against the Kafka topic Access Control Lists (ACLs) already defined in the backing cluster, fetched through the Kafka Admin API. The subject maps to its topic with Confluent’s TopicNameStrategy (orders-value→ topicorders). Read requires a READ ACL and Write requires WRITE (ALL matches either; Write doesn’t imply Read here). The principal is checked asUser:{name}withUser:*wildcard support, LITERAL and PREFIXED bindings both apply, DENY beats ALLOW and everything fails closed: broker errors, timeouts and missing ACLs all deny. Results are cached per topic (default 500 ms; failed lookups are never cached). Choose this when your Kafka ACLs are already the source of truth for access control — a principal that can read or write a topic automatically gets the matching access to its schemas, with no second permission system to operate and no Console or Conduktor-specific topics needed.read-only(new, standalone): every authenticated read passes through and every write is rejected with 403. This mode needs no Kafka connection at all. Choose it as the simplest way to give consumers, dashboards and CI tooling authenticated read access to schemas while guaranteeing nothing can be modified through the proxy — paired withAUTH_PROVIDER=basic, the whole deployment is just the proxy, a mounted credentials file and the backend registry. The newAUTHORIZATION_SUPER_USERSvariable takes a semicolon-separated list of service account names that bypass all authorization checks in every mode, including DENY ACLs intopic-acland the write block inread-only. It’s empty by default and intended as a break-glass identity.
AUTH_USE_REACTIVE_CONFIG flag is deprecated in favor of AUTHORIZATION_MODE.See the environment variables reference for the authorization settings.HTTP Basic authentication
The newAUTH_PROVIDER=basic authenticates clients against credentials read from a JSON file mounted into the container (BASIC_AUTH_LOCATION, default /etc/srp/basic-auth.json) holding bcrypt-hashed passwords. The file is validated at startup (the proxy refuses to start on a missing or malformed file, a duplicate user or an invalid hash) and hot-reloaded on change (BASIC_AUTH_RELOAD_INTERVAL, default 30 s), so you can rotate credentials without a restart — a file that stops parsing is never applied, and the last good credential set keeps serving. Reload outcomes are exported as the basic_auth_credentials_reload_total metric. Plaintext passwords are rejected unless BASIC_AUTH_ALLOW_PLAINTEXT=true.One performance limitation to know about: bcrypt verification is deliberately expensive, so successfully verified username and password pairs are cached for two minutes (at most 1,024 entries; successes only, and the password itself is never stored). A wrong password always pays the full bcrypt cost — brute-force attempts stay expensive, but so does a workload that sends different or invalid credentials on every request. Revoked users take effect on the next file reload regardless of the cache, unknown usernames fail in the same time as wrong passwords so timing doesn’t reveal which usernames exist, and passwords over bcrypt’s 72-byte maximum are a plain 401.See the configuration examples for a complete Basic authentication setup.GUID schema IDs from Confluent Platform 8.x clients
Confluent clients from 8.1.1 onward can carry schema identity as a 16-byte globally unique identifier (GUID) — in the__key_schema_id/__value_schema_id record header or as a payload prefix — instead of the classic 4-byte ID. SRP now serves GET /schemas/guids/{guid} and authorizes it with the same Read-on-subject check as the classic ID route, by resolving the GUID to the subjects holding the schema (resolution is cached; AUTHORIZATION_GUID_SUBJECT_CACHE_TTL, default five minutes).Producers and consumers using header-based schema IDs work through SRP with no client configuration.Expanded API coverage for clients and tooling
Newly routed in this release:GET /subjects, filtered to the subjects the caller can read- compatibility checks:
POST /compatibility/subjects/{subject}/versions[/{version}] - subject metadata
- the read-only tooling endpoints UIs and CLIs call:
GET /schemas,/schemas/types,/schemas/ids/{id}/versions,/config[/{subject}],/mode[/{subject}]and/contexts
Deprecated features
AUTH_USE_REACTIVE_CONFIG is deprecated
Deprecated in: v1.0.0.The AUTH_USE_REACTIVE_CONFIG flag is replaced by AUTHORIZATION_MODE. Existing configurations keep working — true maps to reactive, and AUTHORIZATION_MODE wins when both are set. Switch to AUTHORIZATION_MODE — the flag will be removed in a future release.Quality of life improvements
- Pass-through routes now forward the client’s whole query string upstream — previously unlisted parameters such as
normalize,formatanddeletedwere silently dropped. Subject names containing special characters such as/and%are encoded correctly, and response bodies are always written as UTF-8. - Compatibility is validated end to end against the latest confluent-kafka Python client: every client-facing call is exercised against both SRP and a direct Schema Registry and has to produce the same result.
- Kafka ACL lookups in
topic-aclmode are cached with single-flight de-duplication to sustain high request rates (AUTHORIZATION_TOPIC_ACL_CACHE_TTL, default 500 ms;AUTHORIZATION_TOPIC_ACL_LOOKUP_TIMEOUT, default 5 s).
Fixes
- Updated dependencies and the runtime to address published vulnerabilities: Javalin 6 → 7 (Jetty 12), jackson-databind bumped for three denial-of-service vulnerabilities plus fixes for CVE-2026-8763 and CVE-2026-10050, an OpenSSL fix in the base image, and the runtime image now runs on a JRE 25 base built in a Temurin 21 stage.
- Breaking changes
- Behavior changes
- New and updated features
- Preview features
- Quality of life improvements
- Fixes
- Known issues
- Security advisories
Breaking changes
Cluster membership protocol requires new group ACLs
Gateway nodes now coordinate their cluster membership through a new group protocol that makes rolling restarts smoother but is incompatible with older versions.Every deployment joins the new group, including one with a single Gateway node. If your Kafka cluster doesn’t restrict group access with ACLs and you don’t setGATEWAY_GROUP_ID, the upgrade needs no change. Otherwise, your upgrade path depends on your configuration — and with internal load balancing, on whether you can tolerate downtime.Upgrade external load balancing
Gateway nodes using external load balancing now join a group where previously they did not. If you deploy Gateway with our Helm chart, this is your case: the chart turns internal load balancing off.If your Kafka cluster restricts group access with ACLs, grant the Gateway service accountRead on the group id conduktor_${GATEWAY_CLUSTER_ID}-fleet before you upgrade.Alternatively, grant the Gateway service account Read on a group id of your choice by setting GATEWAY_GROUP_ID.Upgrade internal load balancing with zero downtime
A rolling upgrade from a pre-v3.22.0 cluster using internal load balancing only works when the v3.22.0 nodes join under a different group id. What you change depends on your current configuration.- Grant the Gateway service account
Readon the new group id before you start the rolling upgrade. - You can drop the ACL on the old group id once every node runs v3.22.0.
- Client connections are unevenly distributed across the cluster until the last node restarts.
- If a v3.22.0 node ends up in the same group as a running older node, it exits with code
41.
Upgrade internal load balancing without changing ACLs
You can also upgrade a Gateway cluster using internal load balancing without ACL changes, if downtime is acceptable. Stop every pre-v3.22.0 node before starting any v3.22.0 node. What you change depends on your current configuration.- If any older node is still running in the same group when a v3.22.0 node starts, that node exits with code
41.
Removed config
To tune the new group protocol, use the Kafka consumer settingsheartbeat.interval.ms and session.timeout.ms. Pass them to Gateway as KAFKA_HEARTBEAT_INTERVAL_MS and KAFKA_SESSION_TIMEOUT_MS, like any other KAFKA_ connection parameter.Gateway removes three undocumented variables:GATEWAY_CONSUMER_GROUP_MEMBERSHIP_TIMEOUT_MSGATEWAY_CONSUMER_GROUP_POLL_INTERVAL_MSGATEWAY_INIT_CONSUMER_GROUP_MEMBERSHIP_TIMEOUT_MS
Some Prometheus metrics change name or are removed
The official Gateway Grafana dashboards don’t use any of these metrics, so they keep working. Only custom dashboards and alerts built on the metrics below need updating. For every metric Gateway exports, see the Gateway metrics reference.Latency percentiles come from the histogram only
gateway_latency_request_response_seconds no longer exports its quantile series. The official Gateway dashboard already computes its latency percentiles from the _bucket series, so it isn’t affected. If a custom dashboard or alert of yours reads quantile, compute percentiles from the _bucket series instead: The undocumented vertx_* metrics are removed
Gateway now reports requests to its HTTP API with new, documented metrics, and no longer exports the undocumented vertx_* metrics. If you read vertx_* directly, switch to the gateway_api_request_* metrics:codebecomesstatusandroutebecomespath. Path parameters change from:nameto{name}.gateway_api_request_totaldoesn’t count requests that match no endpoint.vertx_http_server_requests_totalcounted them withroute="".- Other
vertx_*metrics have no replacement, for examplevertx_http_server_response_time_seconds_max.
The undocumented gateway_lived_event_* gauges drop _total
If you read these gauges directly, drop the _total suffix: Behavior changes
Topics in Virtual Clusters have their own topic IDs
Topics in Virtual Clusters now have their own topic IDs, separate from the physical topic’s. Aliases and topic views already had their own. This fixes a topic ID support issue with Virtual Clusters. It causes additional disruption during the upgrade, particularly for franz-go 1.22+ clients, which will likely need a restart afterwards.Vault KMS external connections rename their engine variables
This only affects a HashiCorp Vault KMS external connection that you set up in 3.21, while external connections were a preview feature. Vault configured inline in an Interceptor’skmsConfig is unaffected. External connections are generally available from this release.The connection’s ENGINE and MOUNT variables become ENGINE_TYPE and ENGINE_MOUNT:Rename them before you upgrade. If you keep the old names, Gateway fails at startup and names the variable.
New and updated features
External connections are generally available
External connections leave preview. Gateway declares a connection to an external system once at startup, and Interceptors and topic views reference it by name instead of each holding its own copy of the address and credentials. Declare one withGATEWAY_EXTERNAL_CONNECTION_<NAME>_CONFIG_<PROPERTY> environment variables.Two kinds of external connection are available:- Schema registry external connections, named by topic views with
spec.schemaRegistryConnectionNameand by Interceptors that read schemas withschemaRegistryConnectionName. Reading schema-encoded topics through a topic view leaves preview too. - KMS external connections, named by the encryption and decryption Interceptors with
kmsConnectionName.
Vault external connections support every auth method
A HashiCorp Vault external connection now offers every auth method inline configuration does. On top of the token, AppRole and username and password added in 3.21, it authenticates with:Set the external connection’sAUTH_TYPE to the method you want. Azure, GCP and Fortanix are available as KMS external connections
Azure Key Vault, Google Cloud KMS and Fortanix DSM can now be configured centrally as KMS external connections, matching the providers available through inlinekmsConfig. Declare each external connection once, then reference it from encryption and decryption Interceptors with kmsConnectionName. See configure KMS external connections for details.Tokenization through a HashiCorp Vault external connection
An encryption Interceptor can now tokenize through a HashiCorp Vault external connection whoseENGINE_TYPE is TRANSFORM. Set each field’s keyId to a bare Transform role name. Tokenization configured inline keeps using a vault-transform:// keySecretId. This release also renames the external connection’s engine variables. Crypto shredding through KMS external connections
An encryption Interceptor that names a KMS external connection can now crypto shred. Add agateway block beside kmsConnectionName and give each field a bare keyId template. The external connection holds the master key, and Gateway stores a separate key for each record, as it does with inline configuration. The decryption Interceptor needs the same gateway block. Topic views can now filter on the current date and time
A topic viewWHERE clause now accepts CURRENT_DATE, CURRENT_TIME and CURRENT_TIMESTAMP:Lifecycle metrics record the latency of each segment of the request lifecycle
Request lifecycle metrics time each stage of a request inside Gateway, from reading it off the client socket to writing the response back. Each stage is a Prometheus histogram labeled with the Kafka API key and, where one applies, the Interceptor name. Use them to find which stage a latency spike comes from, such as authorization, an Interceptor, the upstream queue or Kafka itself.They’re off by default because they add high-cardinality series. Turn them on withGATEWAY_FEATURE_FLAGS_LIFECYCLE_METRICS=true, and scope them to the API keys and Interceptors you care about. See request lifecycle metrics. HTTP API requests have their own metrics
Gateway now exports Prometheus metrics for requests to its HTTP API: a request count, a duration histogram and the number of requests in progress, with labels for method, endpoint path and status. Use them to watch the HTTP API’s traffic, latency and error rate. See HTTP API metrics for names, labels and buckets. They replace the undocumentedvertx_* metrics, which are removed. Preview features
Topic ID support improvements
Topic ID support is still a preview feature, off by default. This release brings two improvements:- Incremental fetch sessions: you can now turn on topic ID support without turning off incremental fetch sessions. Previously, Gateway didn’t start with both flags set to
true. - Virtual Clusters: this release fixes the 3.21.0 known issue where, with Virtual Clusters configured, a client with an ALLOW ACL could intermittently receive
TOPIC_AUTHORIZATION_FAILED. To fix it, topics in Virtual Clusters now have their own topic IDs.
Quality of life improvements
- Audit log events:
- Kafka and REST API events report client and listener addresses consistently as
host:port, without resolution markers such as/<unresolved>. AUTHORIZATIONevents for denials by Gateway-managed ACLs include the client’s connection details, like other events.
- Kafka and REST API events report client and listener addresses consistently as
- Internal load balancing:
- Rolling restarts are smoother. Clients move away from a node that’s shutting down almost at once, instead of after a few seconds.
- Gateway nodes keep running during a Kafka outage. Previously, a node failed to start if Kafka was unavailable, and stopped if it lost contact with the rest of the Gateway cluster.
- HTTP API: once shutdown starts, Gateway answers new calls with
503. - Configuration:
- A
${VAR|default}placeholder in Interceptor and external connection configuration uses its default whenVARisn’t set. Previously the default only applied whenVARwas set but empty, and an unset variable failed the configuration withEnvironment variable 'VAR' not found. - Gateway catches more external connection misconfigurations at startup, instead of on first use.
- A
- Docker image: Gateway ships a Java Runtime Environment (JRE) instead of a full JDK, on a smaller base image. The image no longer includes JDK tools such as
jcmd,jstackandjmap, or the async-profiler added in v3.20.0. To use them, run theconduktor/conduktor-debugimage, which attaches to Gateway from a separate container.
Fixes
- Fixed three traffic control policies:
- Limit connection attempts:
maximumConnectionsPerSecondcounts only new connections each second. Previously it counted active connections too, so steady traffic could use up the limit. Withaction: THROTTLE, clients are now told to wait the configuredthrottleTimeMs. Previously they were always told 100 ms. - Limit commit offset: violations now name offset commits. Previously the message in audit events and logs said join group.
- Consumer group: with a
groupInstanceIdrule, a consumer that doesn’t setgroup.instance.idis now reported with the configured action. Previously its JoinGroup failed withUNKNOWN_SERVER_ERROR.
- Limit connection attempts:
- Fixed a slow HTTP API call blocking every other HTTP API call. When a long-running call blocked the
/healthendpoints, Kubernetes could restart the node. - Fixed the error clients get when they describe or delete a topic by ID with topic ID support off, which is the default. Commands such as
kafka-topics.sh --describe --topic-idnow fail withUnsupportedVersionException. Previously, describing by ID returned a single empty row and deleting by ID failed with a server error. Requests by topic name are unaffected. - Fixed removing static members from a consumer group in a Virtual Cluster. If your consumers set
group.instance.id, removing them from their group failed withUNKNOWN_MEMBER_ID, whether withkafka-consumer-groups.sh --delete-members, the Kafka Admin API or Kafka Streams removing a stream thread.
Known issues
- Cache Interceptor: the cache Interceptor doesn’t support incremental fetch sessions, which are on by default since v3.21.0. If you use it, set
GATEWAY_FEATURE_FLAGS_INCREMENTAL_FETCH_SESSIONS_ENABLED=false.
Security advisories
This release resolves the following advisories:- CVE-2026-40984 (Micrometer) and CVE-2026-45799 (Wire), both flagged in Gateway v3.21.0
- CVE-2026-63126 (Wire)
- CVE-2026-68497 (Jackson)
Fixes
- Fixed a regression where the application dropdown in alert ownership lost its filtering and listed every application. The filtering is restored: an application now shows only when you’re a member of one of its application groups that grants the manage-alerts permission on one of the application’s instances.
Security advisories
Image scanners flag the following advisories against the Console and Cortex (monitoring) images. None of them expose a reachable vulnerable code path in either image; they’ll clear from scans in an upcoming release, or as soon as upstream dependencies allow.Console image
- CVE-2026-19499 — a buffer overflow in the glibc
strfmon/strfmon_lmonetary-formatting functions. Nothing in the Console image calls these functions on external input — Console runs on the JVM, which does its own number formatting — so the vulnerable code path isn’t reachable. The fix has already shipped in the base OS (Wolfi glibc 2.44-r4); scanners may keep flagging it until the Wolfi advisory feed is corrected.
Cortex image
- CVE-2026-19499 — the same glibc advisory as above. Prometheus and Cortex are Go binaries that don’t use glibc’s monetary-formatting functions, so the vulnerable code path isn’t reachable here either.
- CVE-2026-82049 — Python’s
tarfileextraction filters can follow a hard link to a symbolic link and modify or expose files outside the extraction directory. Python is present in the Cortex image only to run thesupervisordprocess supervisor, which never extracts archives — nothing in the image processes tar archives with Python, so the vulnerable code path isn’t reachable. The upstream fix is merged in CPython but not yet part of a released 3.13.x version; the image will pick it up as soon as one ships.
Fixes
- Fixed a regression in Console 1.47.0 that stopped Console from connecting to Kafka clusters that authenticate with OAuth through Azure Managed Identity. Connections using
AzureManagedIdentityCallbackHandlerfailed with aNoClassDefFoundErrorbecause the Azure OAuth library wasn’t compatible with the Kafka 4 client. - Console no longer fails to read a Kafka Connect connector’s configuration when the Connect API returns a null value for one of the configuration fields. Previously, a single field like this broke the whole validation response, which blocked you from creating, editing or viewing affected connectors — for example, those using the Debezium Oracle 3.6.1 plugin.
- Fixed a UI issue concerning the page loader
Fixes
- During a rolling restart, produce and fetch requests in flight as each Gateway node shuts down could hit a shutdown race and receive a non-retryable
UNKNOWN_SERVER_ERROR, permanently failing Kafka Connect and MirrorMaker 2 tasks that run through the encryption Interceptor. This fixes that race.
Known issues
- Cache Interceptor: the cache Interceptor doesn’t support incremental fetch sessions, which are on by default since v3.21.0. If you use it, set
GATEWAY_FEATURE_FLAGS_INCREMENTAL_FETCH_SESSIONS_ENABLED=false.
Security advisories
This release resolves CVE-2026-41254 (Little CMS in the JDK), flagged in Gateway v3.21.0, by moving to JDK 25.0.4.Fixes
- During a rolling restart, produce and fetch requests in flight as each Gateway node shuts down could hit a shutdown race and receive a non-retryable
UNKNOWN_SERVER_ERROR, permanently failing Kafka Connect and MirrorMaker 2 tasks that run through the encryption Interceptor. This fixes that race.
- Breaking changes
- New and updated features
- Govern who can edit labels and descriptions
- Consume messages that carry a schema GUID in their headers
- Give application owners access to their own Chargeback data
- Let application owners manage their own alerts
- Manage service accounts from an application group
- View role bindings on a topic
- Live lineage
- Restrict Self-service permission grants with resource policies
- Apply reusable permission templates to application groups
- Manage topic data and partitions through the public API
- Preview features
- Quality of life improvements
- Fixes
- Security advisories
Breaking changes
Java 25 disables legacy TLS algorithms
Console now runs on Java 25, which disables legacy static-RSA cipher suites (TLS_RSA_*) and SHA-1 handshake signatures for outbound TLS connections such as SMTP, webhooks and Confluent Platform MDS. Modern TLS endpoints are unaffected; before upgrading, ensure legacy peers support TLS 1.3 or TLS 1.2 ECDHE with SHA-256-or-stronger signatures.TopicPolicy creation is now blocked
TopicPolicy has been deprecated since ResourcePolicy replaced it in Console 1.34.0. From this release, you can no longer create new TopicPolicies, and the deprecation messaging on existing ones has been improved. If you still rely on TopicPolicies — including in GitOps pipelines that apply TopicPolicy manifests — move them to ResourcePolicy with the moving from TopicPolicy guide.New and updated features
Govern who can edit labels and descriptions
By default, anyone who can view a Kafka resource can also edit its labels and description. You can now restrict label and description editing to users who hold a dedicated Manage metadata permission, separate from the permission to view or edit the resource itself.The new permission covers labels on topics, subjects, connectors, and consumer groups, and descriptions on topics and connectors. It’s enforced only when you opt in by settingenable_metadata_governance to true — until then, nothing changes. Application owners keep their access automatically.Find out more about governing who can edit labels and descriptions.Consume messages that carry a schema GUID in their headers
Console now decodes messages that reference their schema with a globally unique identifier (GUID) in the record headers, instead of a schema ID prepended to the payload. Consume these messages and read them as you would any other. Producers opt in to this format, available from Confluent Platform 8.2, with theHeaderSchemaIdSerializer.Console reads this format but doesn’t yet write it — produce and re-process still prepend the schema ID to the payload. Full GUID support across Console comes in a future release.Find out more about schema IDs in record headers.Give application owners access to their own Chargeback data
Viewing Chargeback used to require a platform-wide permission, which meant granting sight of every application’s costs. A newapplicationInstanceChargebackView instance permission now scopes access to a single application. Assign it through an ApplicationGroup — as the Chargeback Viewer quick-select or directly in the ApplicationGroup manifest — and those members see Chargeback filtered to the applications they own.The permission isn’t granted by default, including to groups that hold full access on their application instances, so nothing changes until you assign it. Platform teams that want to keep cost data centralized can block teams from self-granting it with a ResourcePolicy.Find out more about Chargeback permissions.Let application owners manage their own alerts
You can now assign thealertManage instance permission through an ApplicationGroup. Members can view, create, edit and delete alerts owned by that application instance, without needing platform-wide permissions. Assign it as the Alert Manager quick-select in the ApplicationGroup’s Application Instances section, or directly in the manifest.The permission isn’t granted by default, including to the owner ApplicationGroups created by migration, so nothing changes until you assign it. To create a topic, consumer group or Kafka Connect alert, members also need the matching Describe permission on the underlying resource.Find out more about instance permissions.Manage service accounts from an application group
TheserviceAccountManage instance permission now works end to end in the Console UI. Members of an ApplicationGroup that holds it on at least one application instance see the Service accounts entry in that cluster’s menu, without a cluster-wide ACL role.The page lists the application-managed service accounts of the instances they manage. Service accounts declared centrally on an application instance stay with platform administrators, so an instance that only uses one shows an empty page.Owner ApplicationGroups created by the 1.45.0 migration hold serviceAccountManage, so their members get the menu on upgrade.Find out more about instance permissions.View role bindings on a topic
On Confluent Cloud and Confluent Platform clusters, the topic details page now has a Role Bindings tab. Open it to see which principals hold which Role-Based Access Control (RBAC) roles on that topic, including the resource pattern that granted the binding.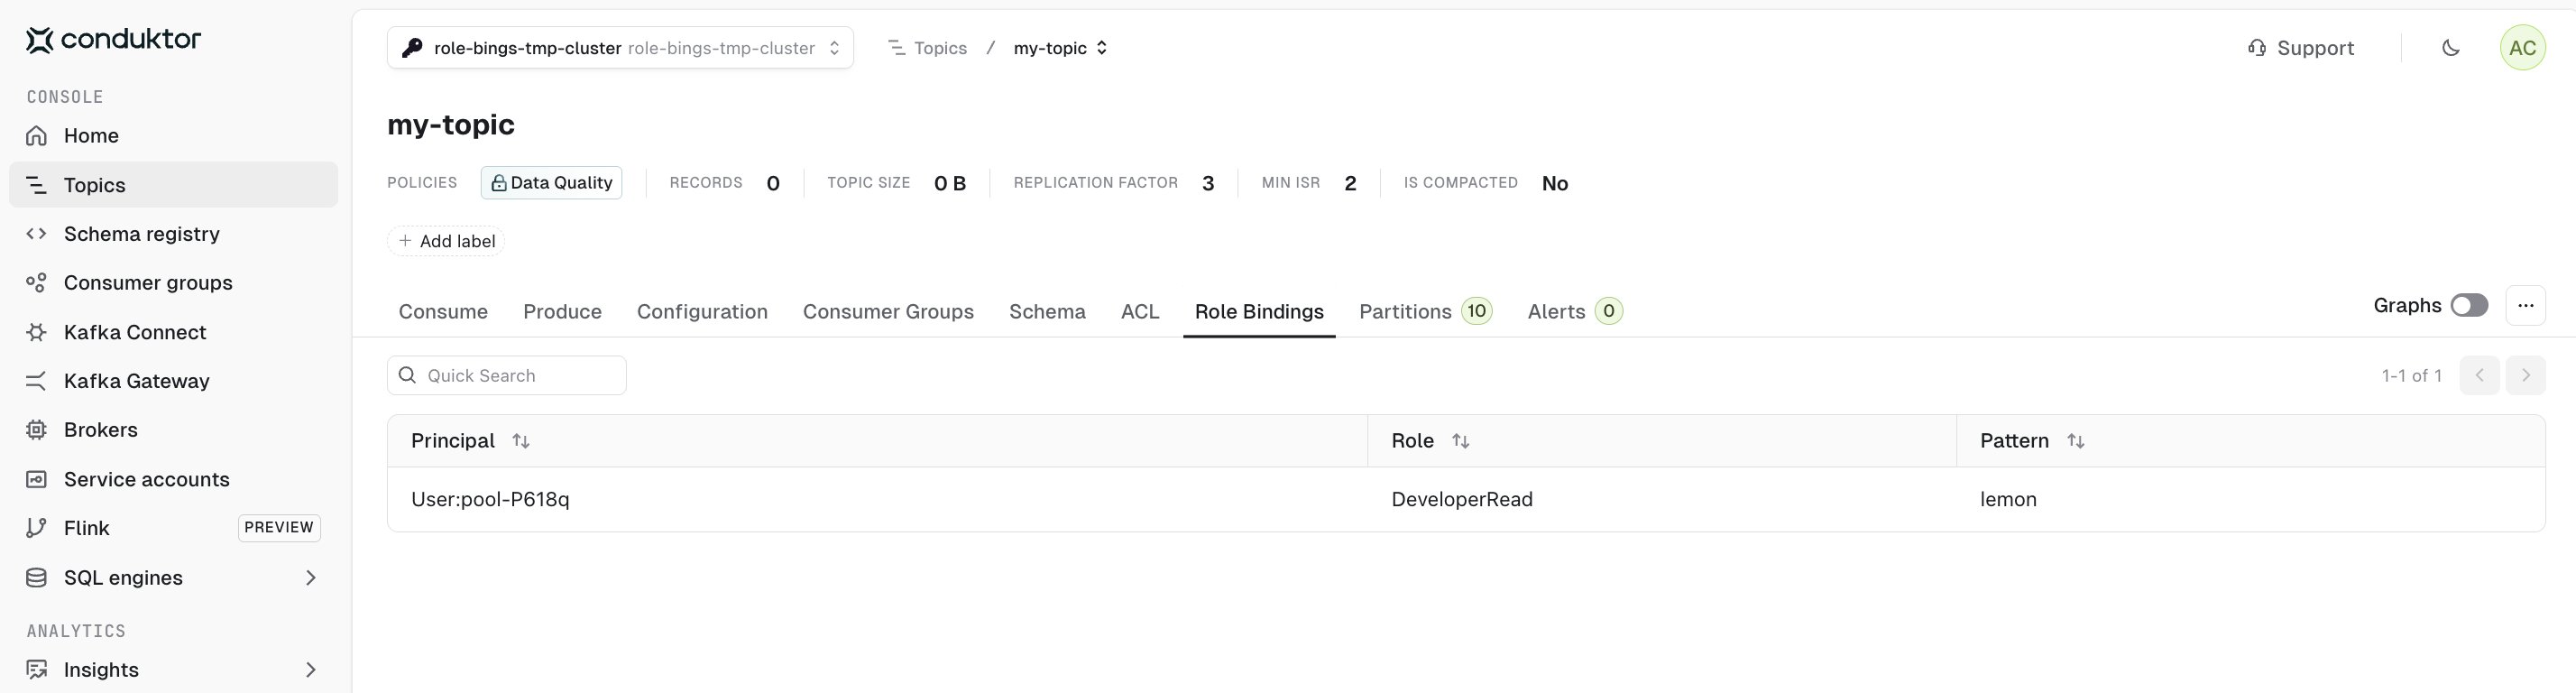
Live lineage
Stream lineage now shows your data in motion. Turn on the Live toggle in the Lineage view to overlay live throughput on the graph: each connection shows its current rate in bytes per second, updated every few seconds, with edges that grow thicker as traffic increases and animate in the direction the data flows.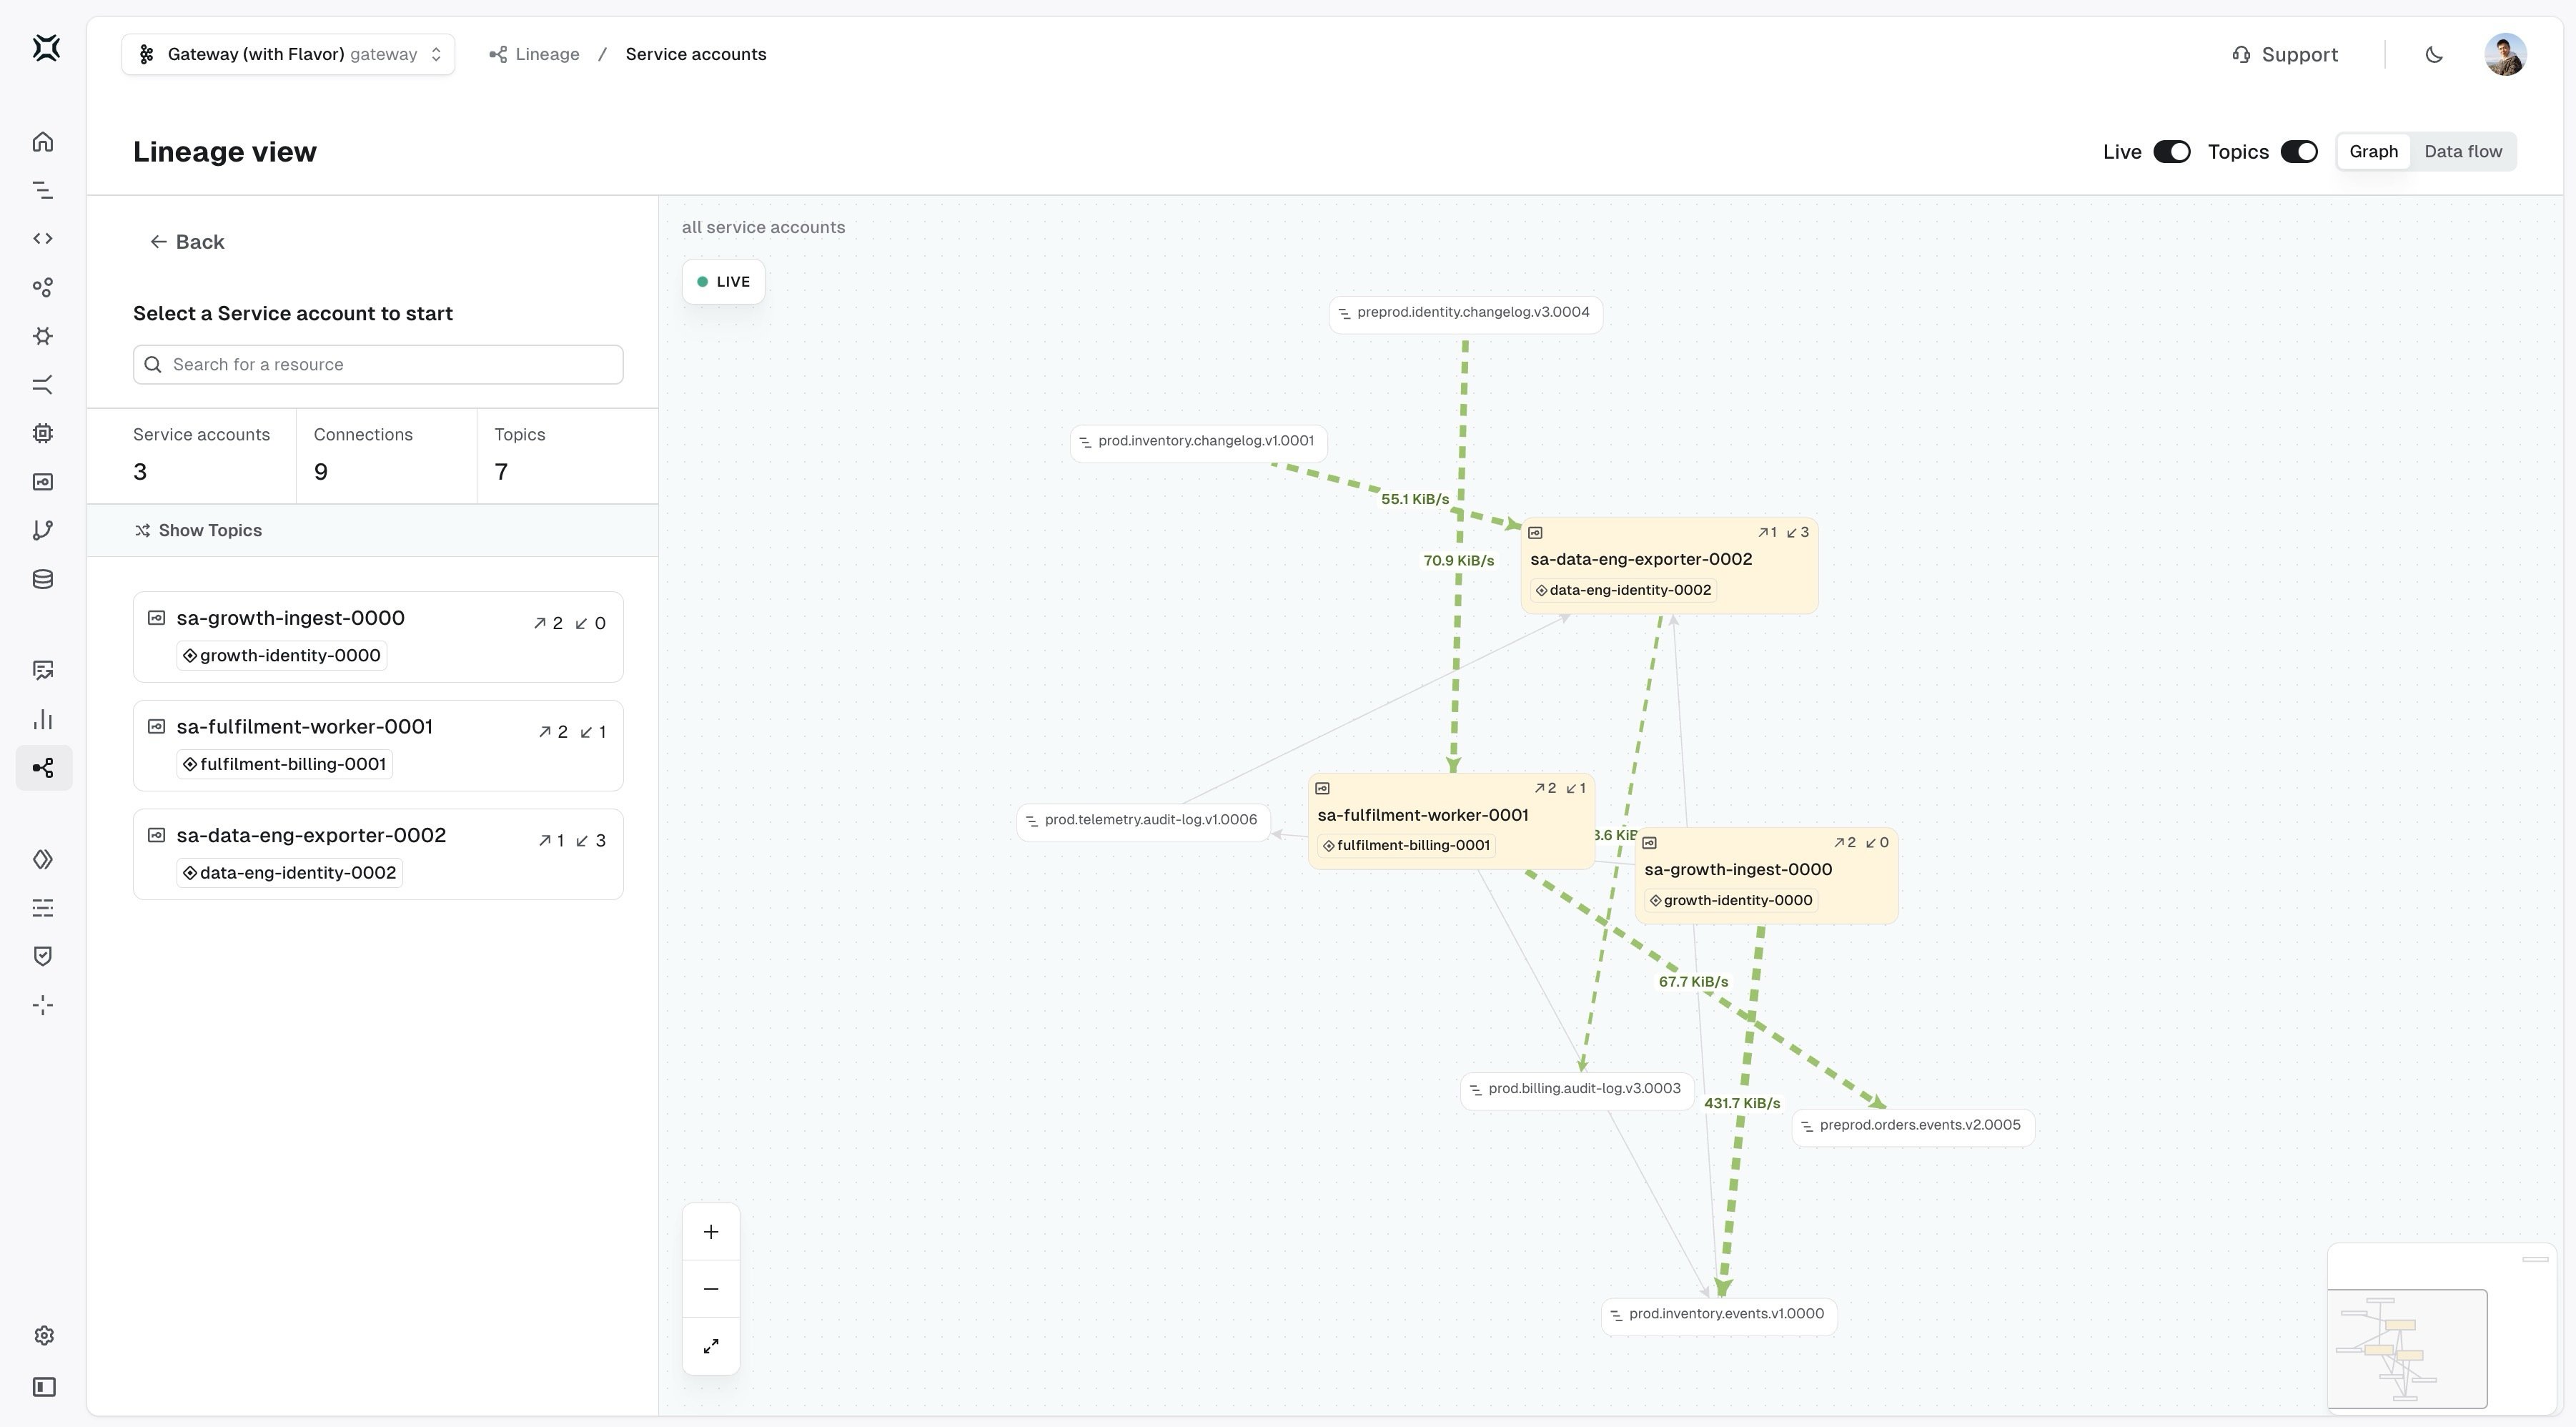
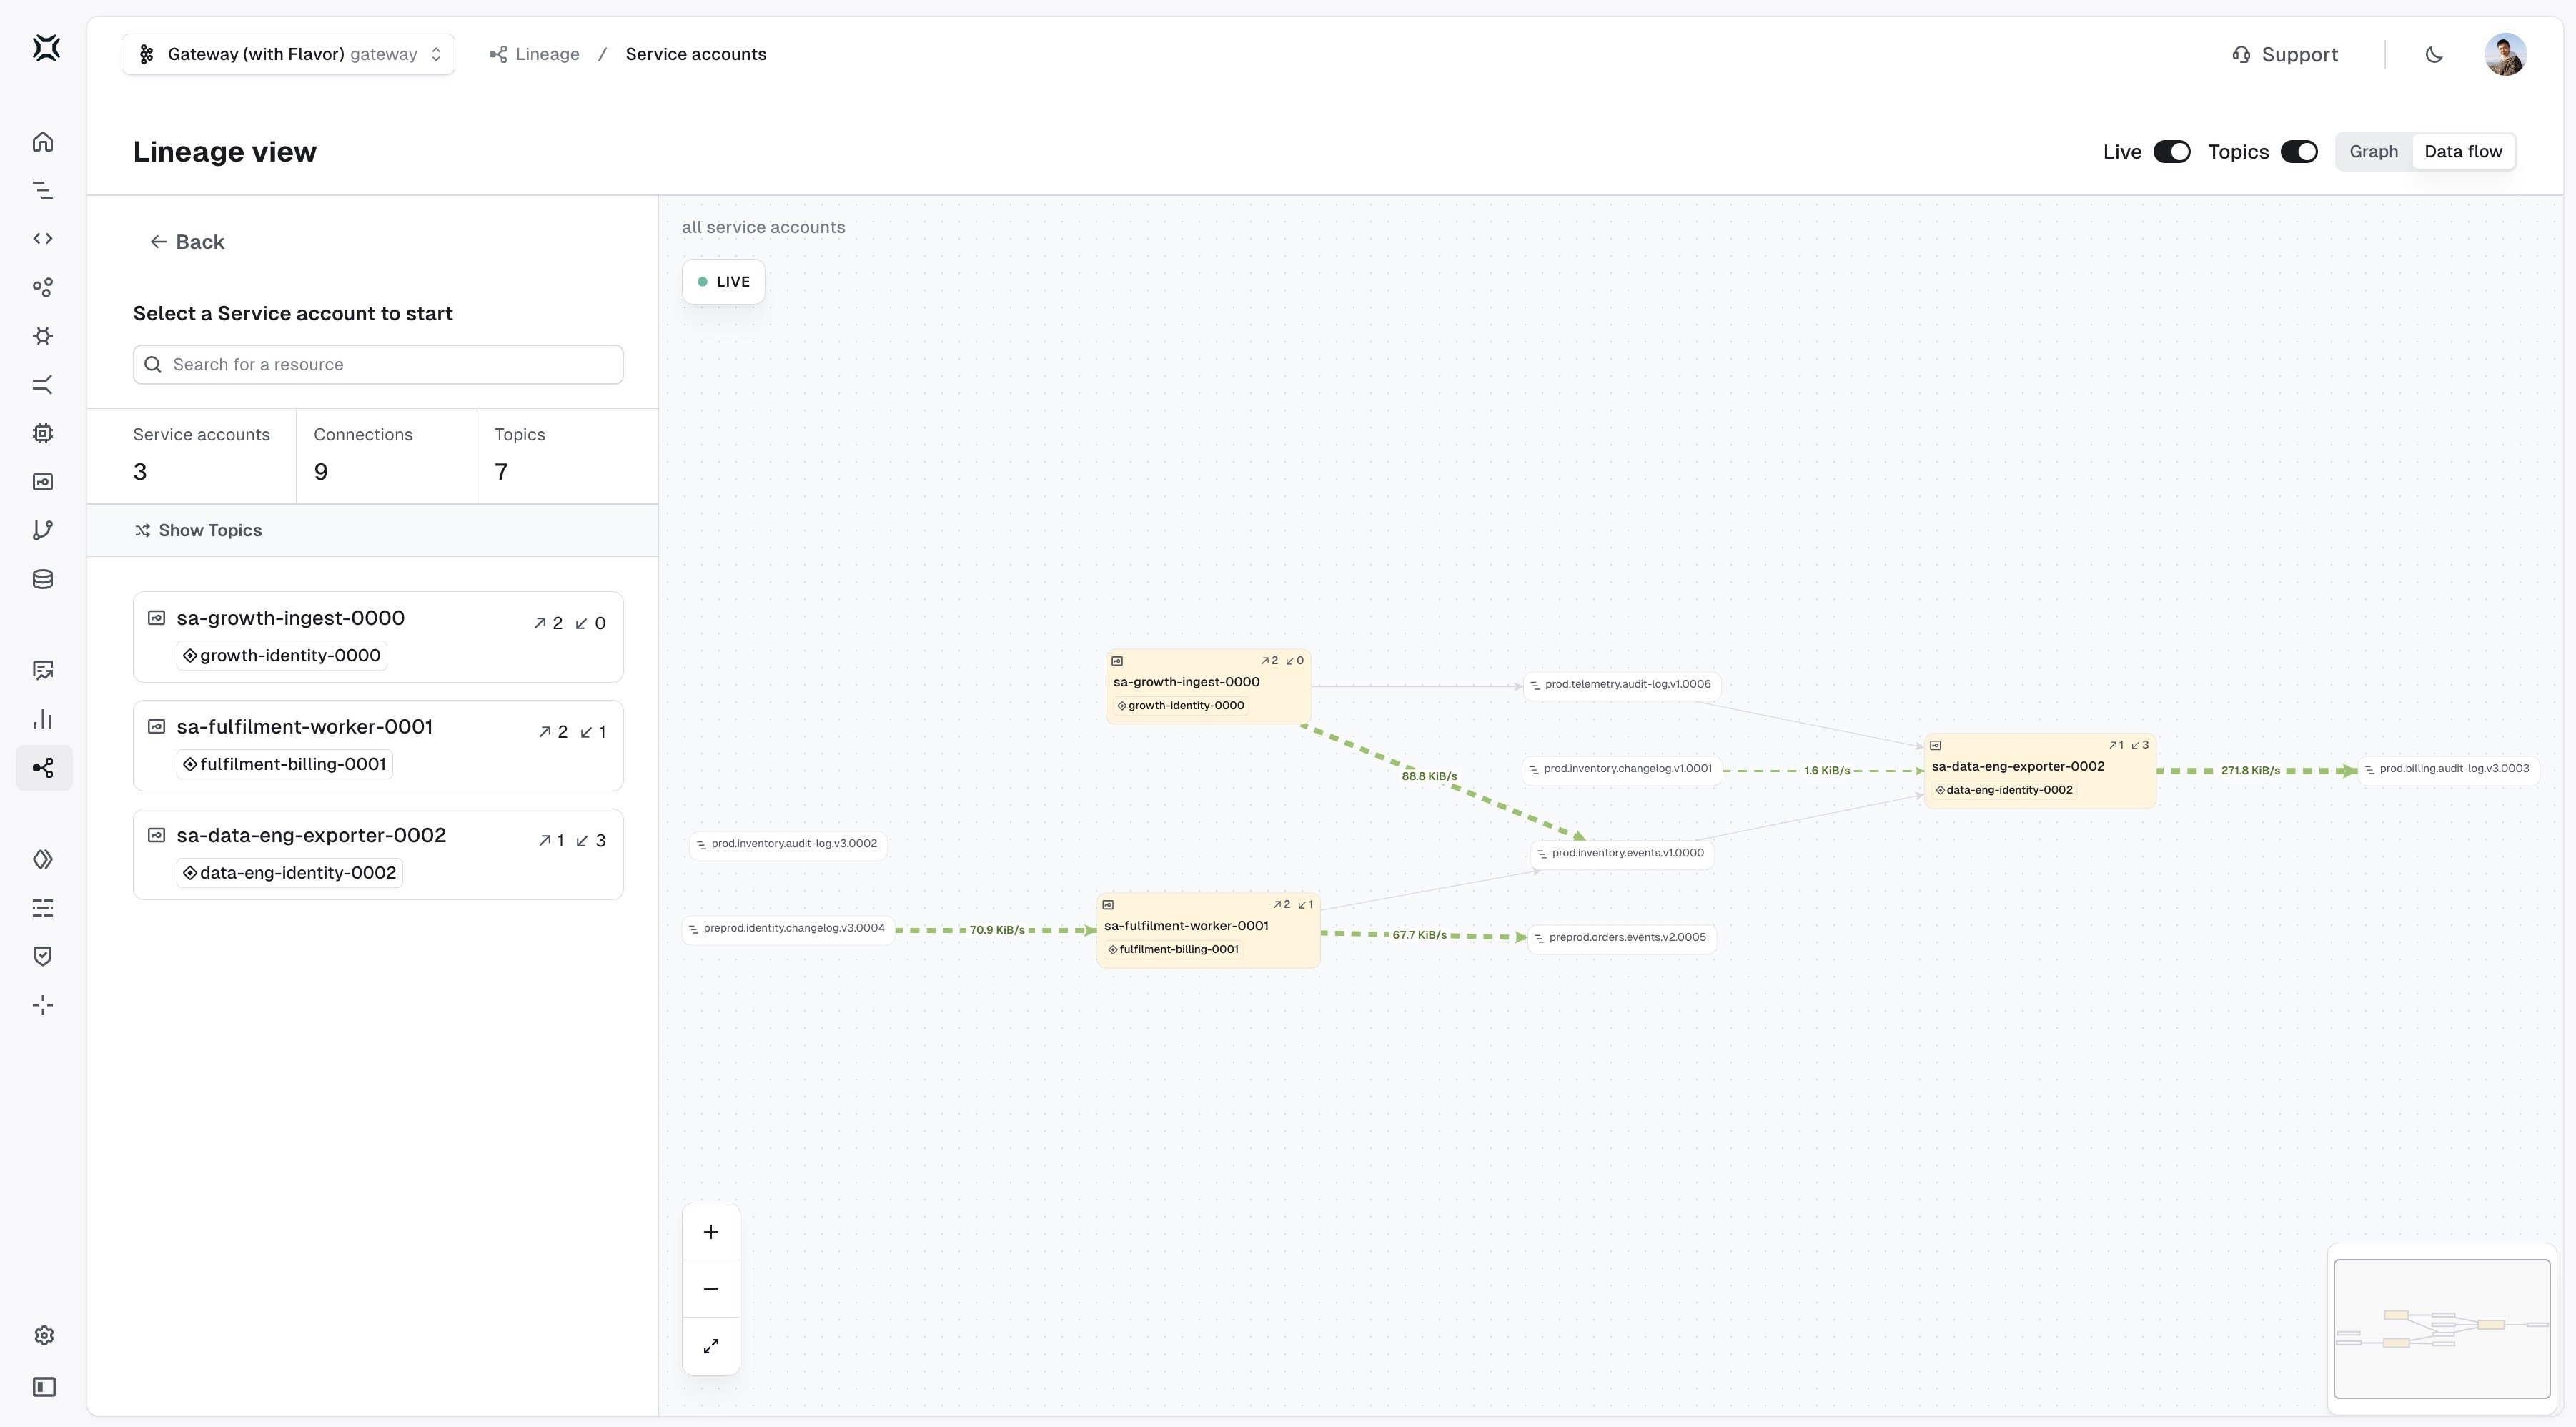
flushIntervalInSecond to a low value for the most responsive view. On other cluster types the Live toggle doesn’t appear.Restrict Self-service permission grants with resource policies
ResourcePolicy has a new target kind:ApplicationInstancePermission. Write Common Expression Language (CEL) rules that every application instance permission grant is checked against — for example, block WRITE access on topic resources — and any grant that breaks a rule is rejected with your error message. Rules can check both the user-facing and service-account permission carried by the grant.These policies are cluster scoped. Unlike Topic, Connector and Subject policies, they aren’t referenced from an Application’s policyRef — instead, go to the cluster management screen and assign them manually under Cluster resource policies, or link them to the KafkaCluster with spec.policiesRef through GitOps.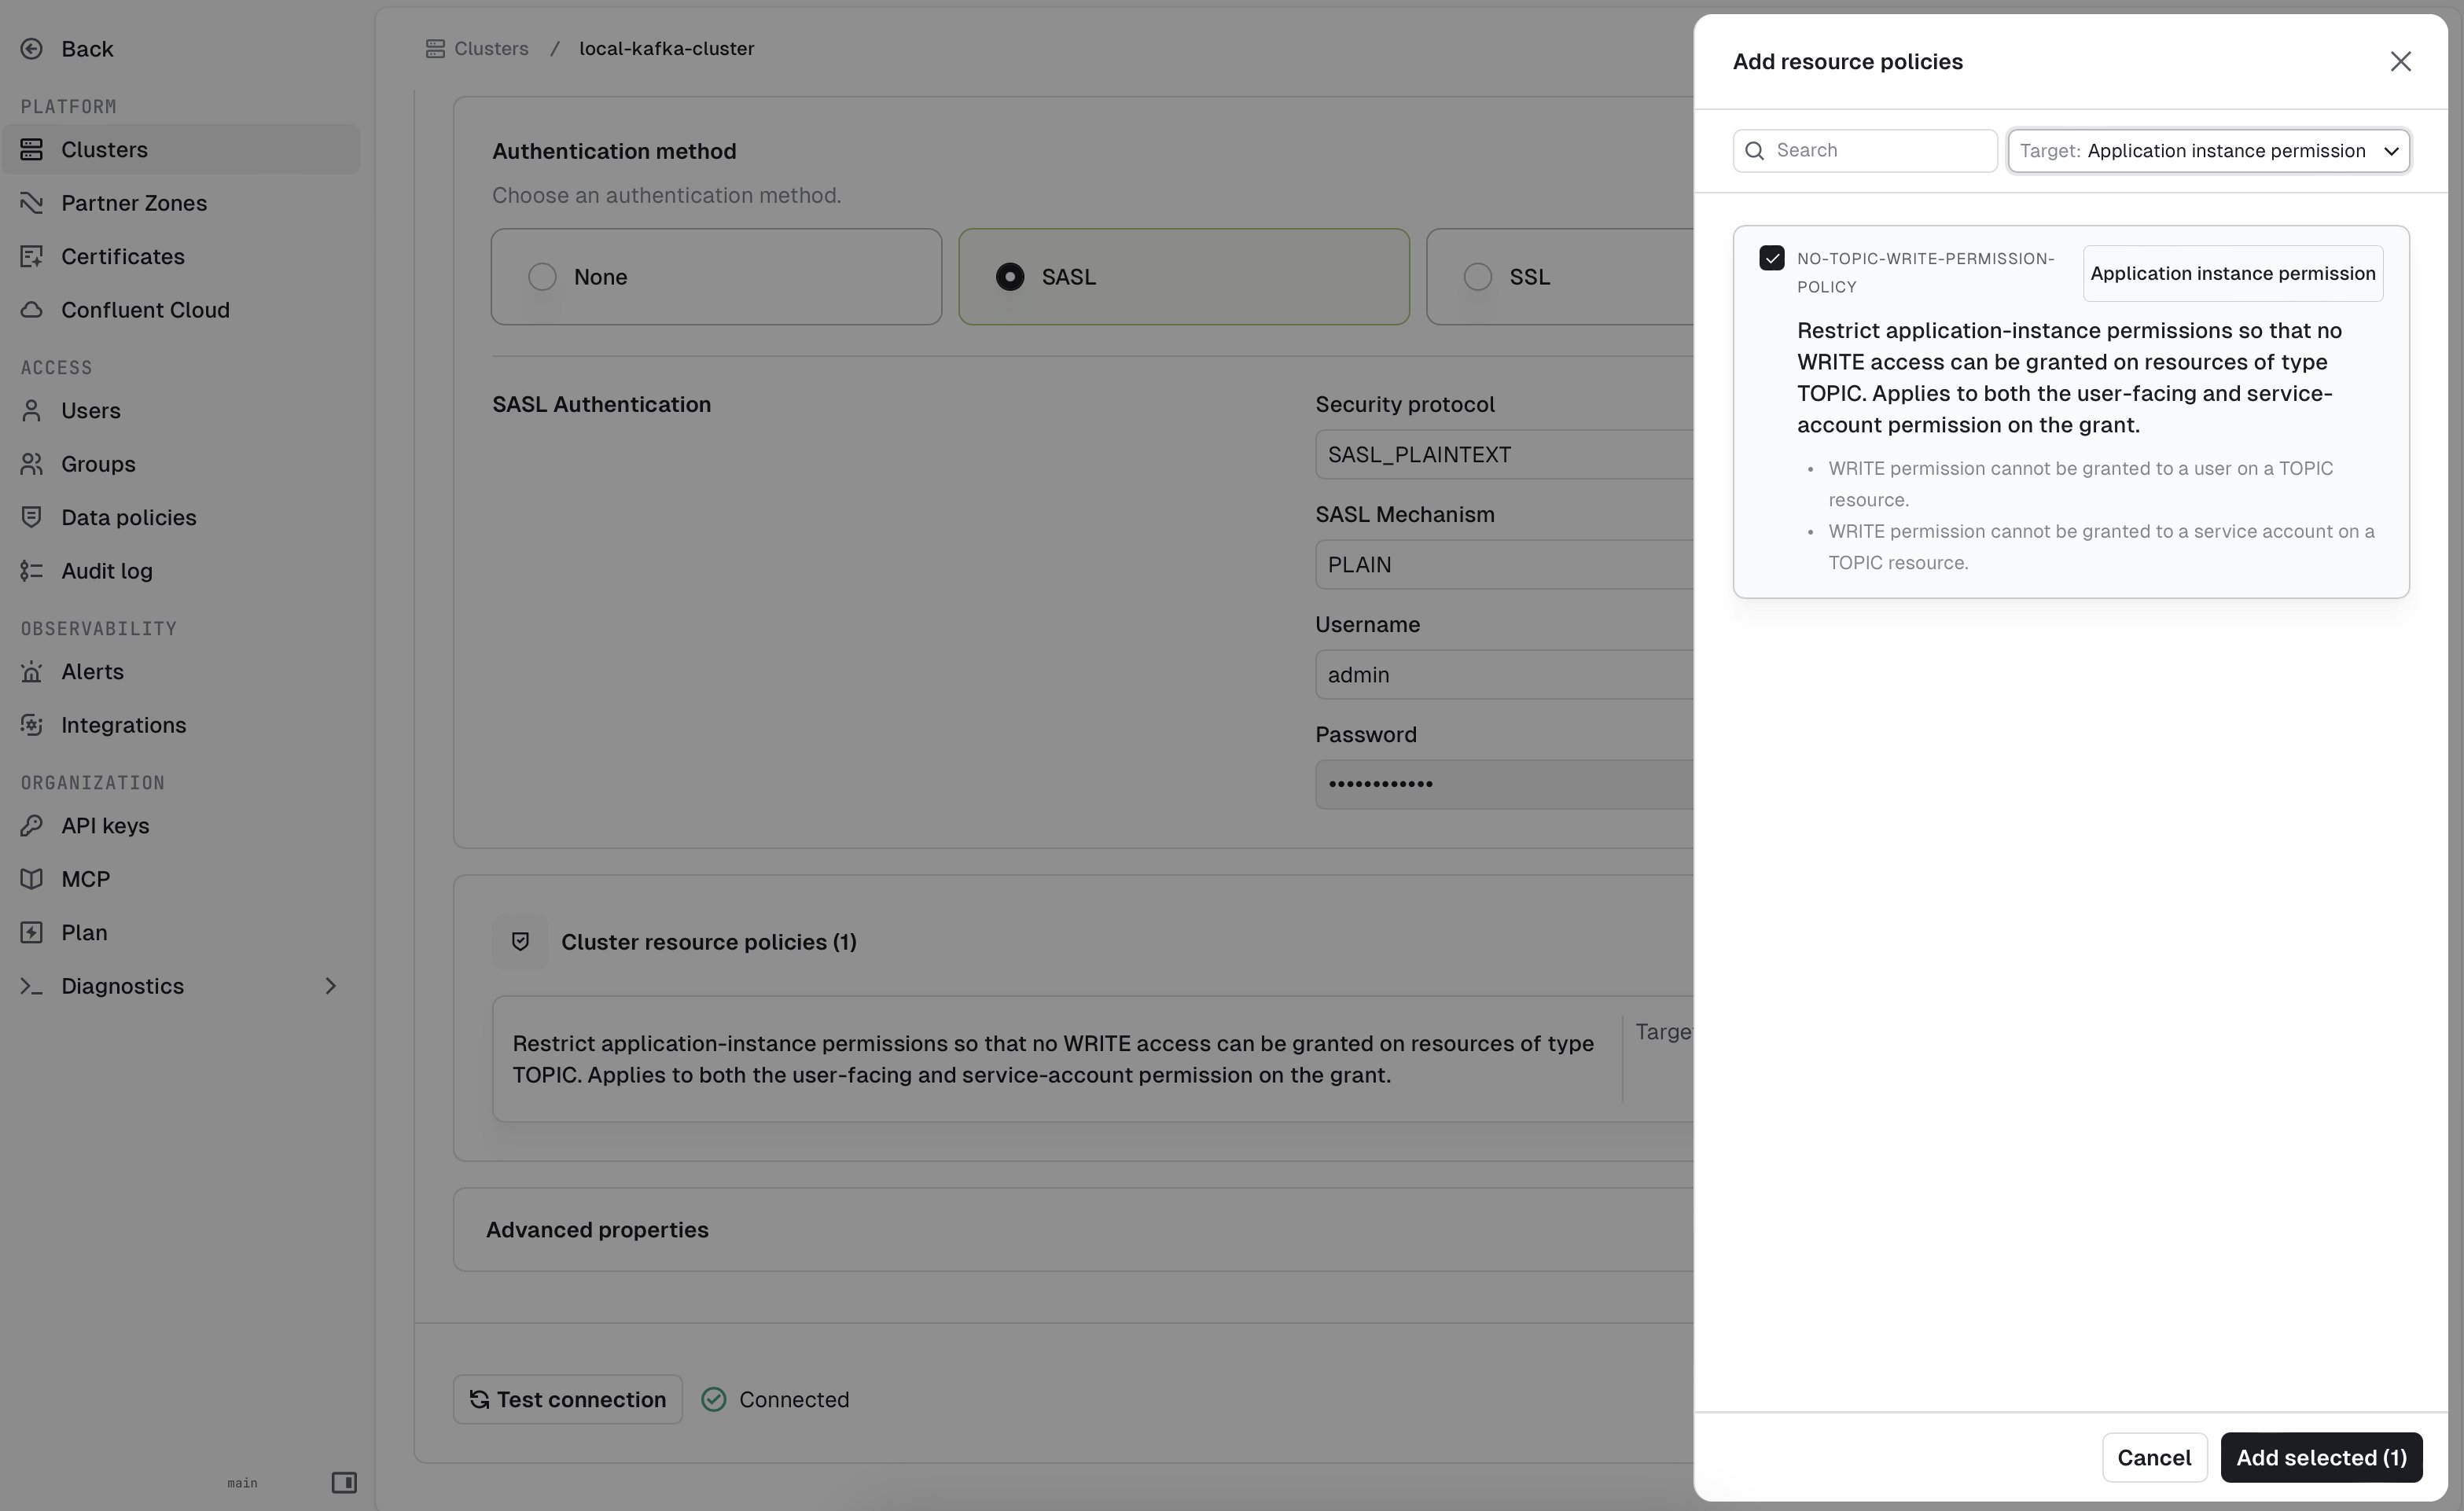
Apply reusable permission templates to application groups
Platform administrators can now define reusableApplicationGroupTemplate resources with a standard set of resource permissions. Manage templates through the public API or CLI, then apply one from an existing ApplicationGroup’s Resource access tab instead of configuring every permission separately.A template can be applied to one application instance or every instance in an application. You can review and adjust the resulting permissions before saving, so templates provide a consistent starting point without preventing instance-specific changes.Find out more about application group templates.Manage topic data and partitions through the public API
The public API now supports more topic administration operations. API clients can:- Increase a topic’s partition count
- Empty an entire topic or an individual partition
- Set low watermarks for one or more partitions
Preview features
Run Flink SQL statements on Confluent Cloud
Console now includes a Flink SQL workbench for Confluent Cloud, available in preview from the new Flink entry in the sidebar. List the statements running in your Confluent environments, write and run new ones in a SQL editor with a built-in catalog browser, watch results stream in live or take a bounded snapshot, export them to CSV, and stop or delete statements — all from Console.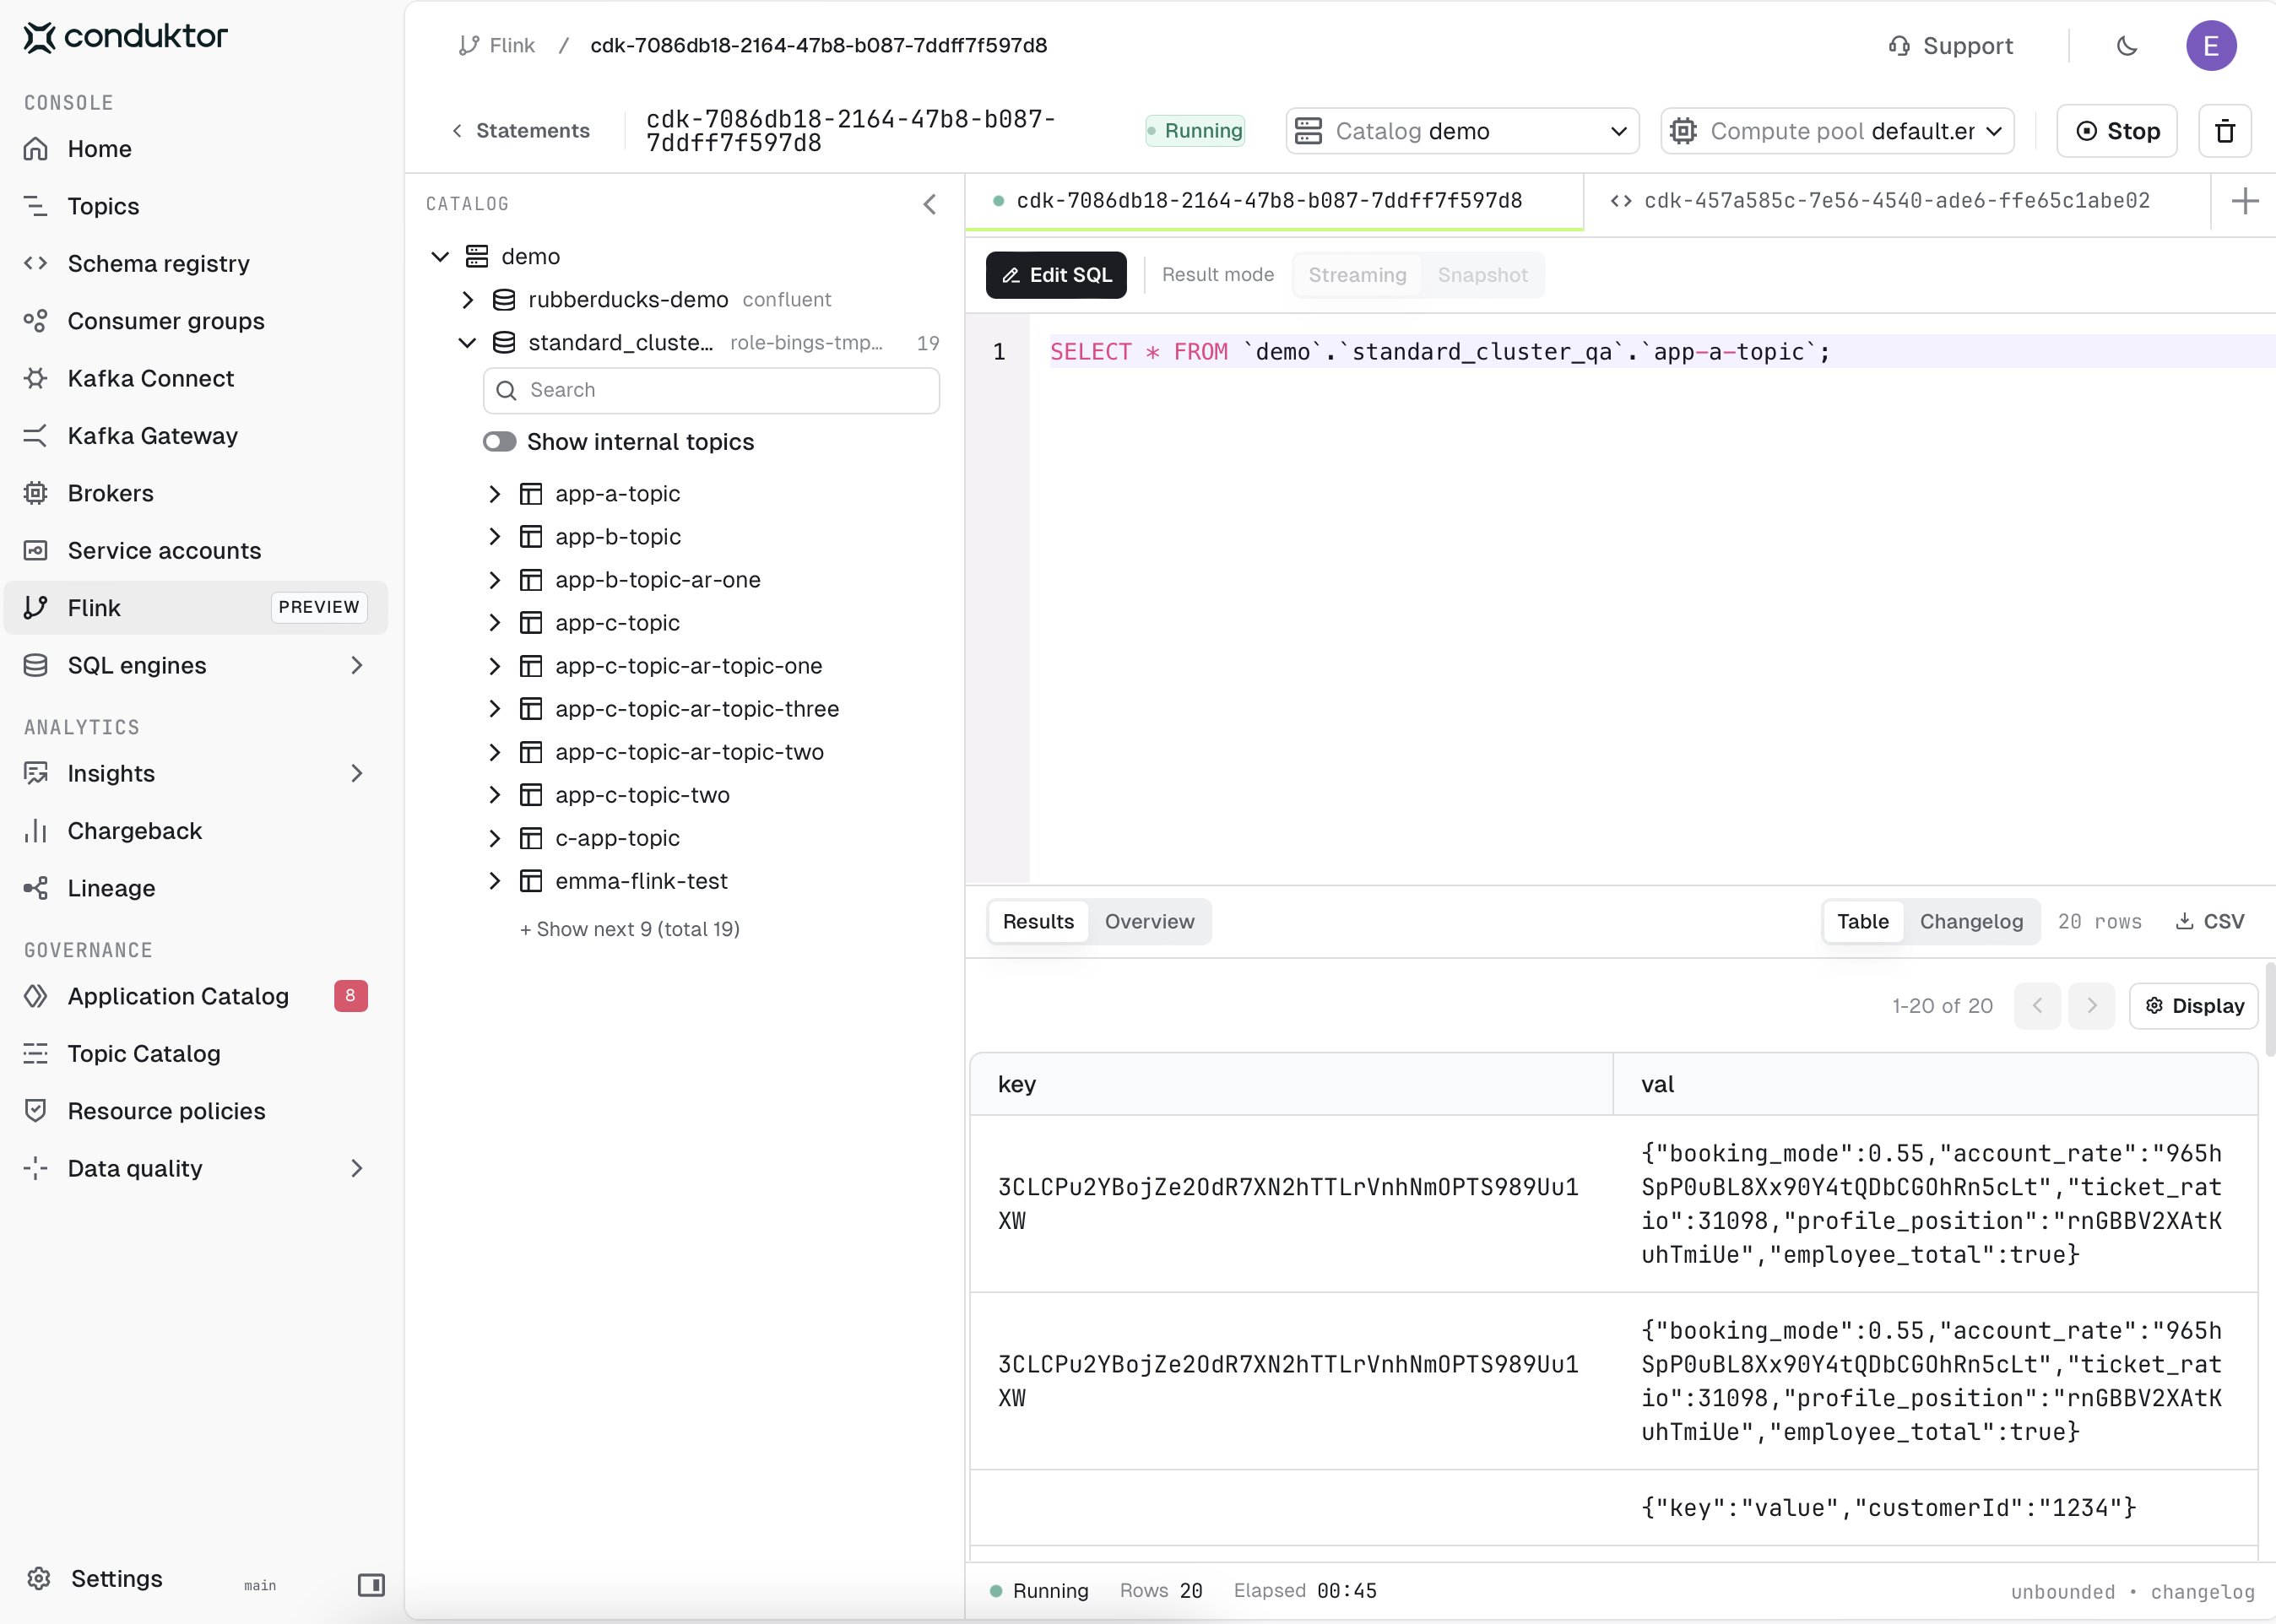
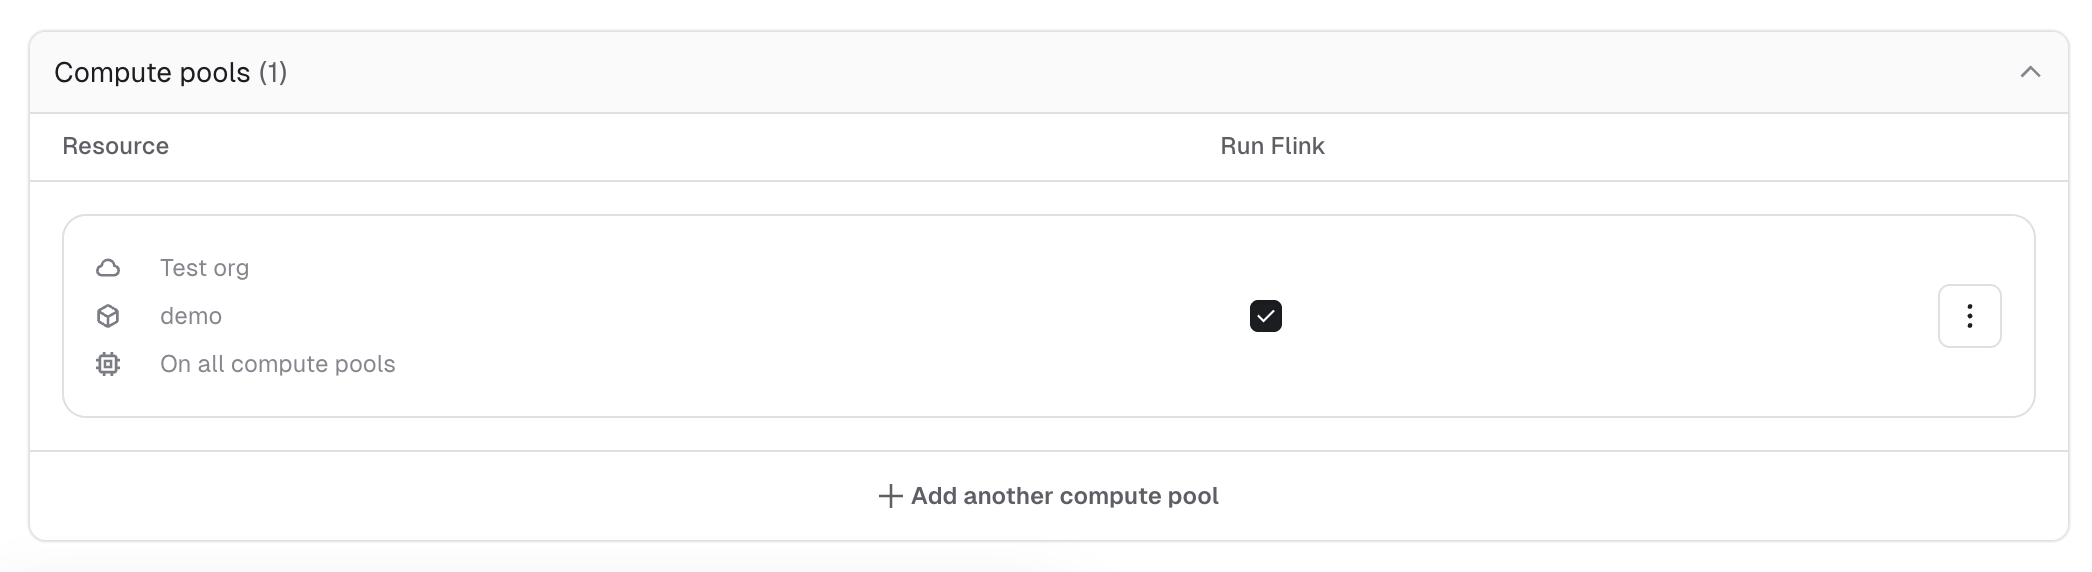
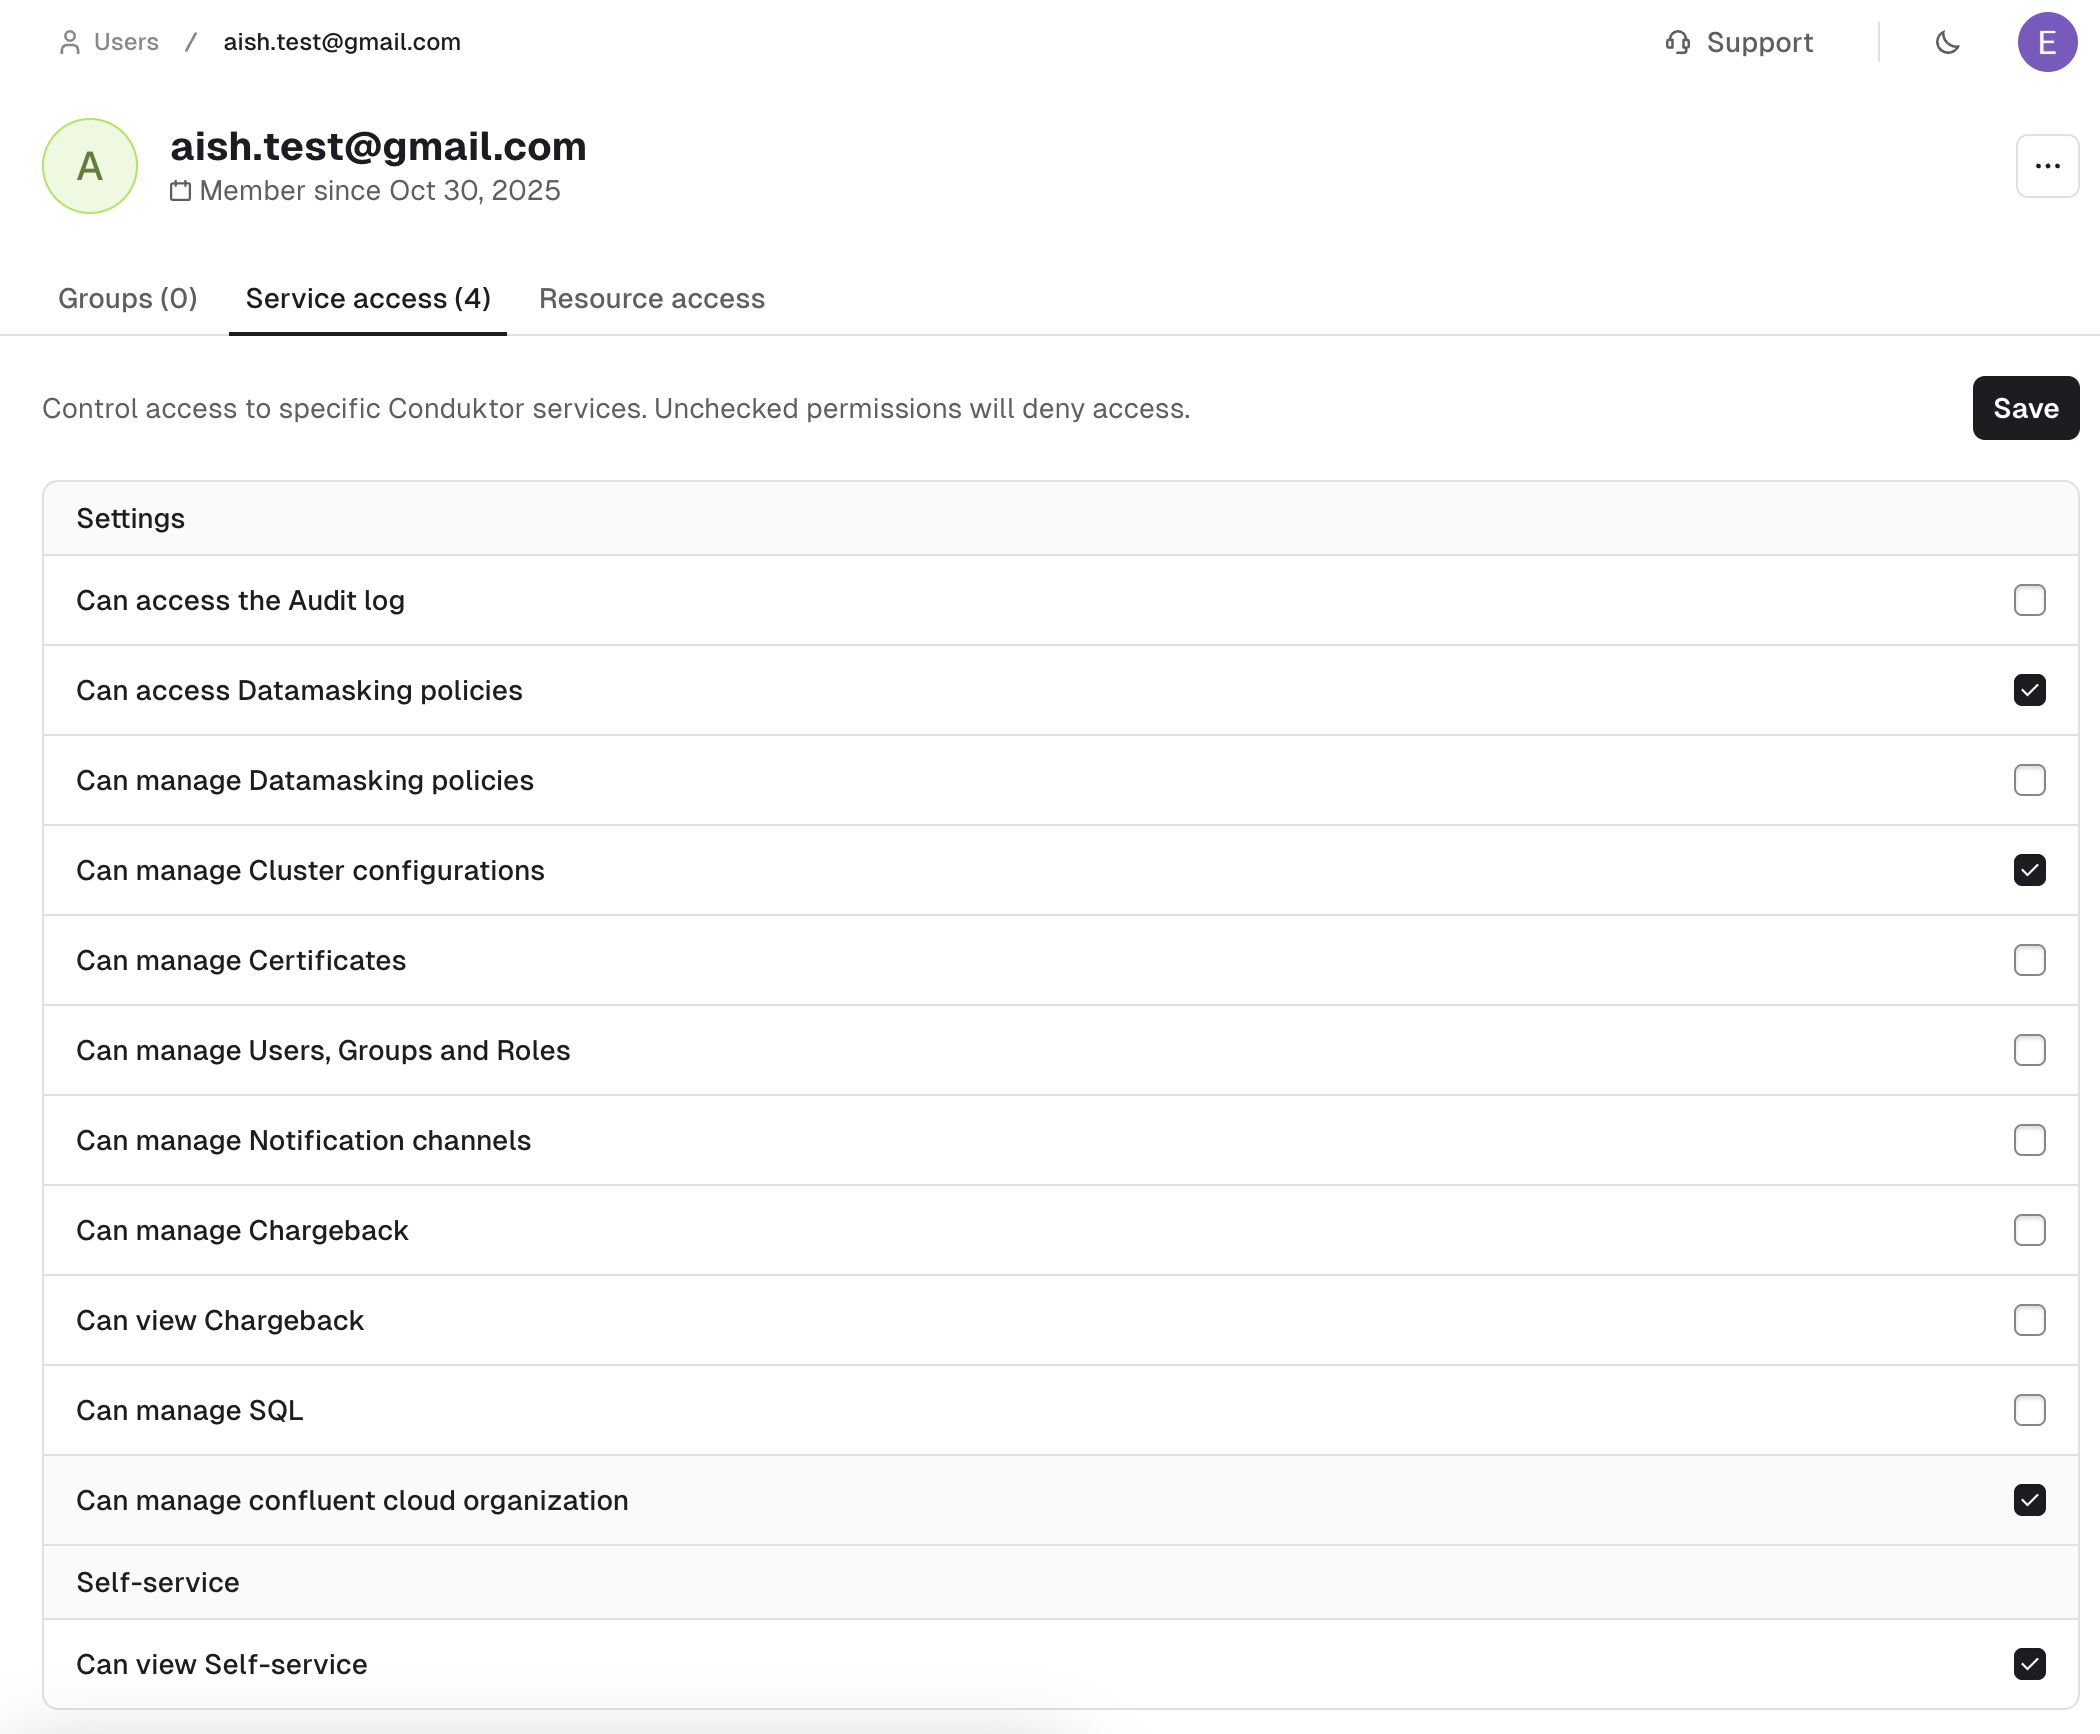
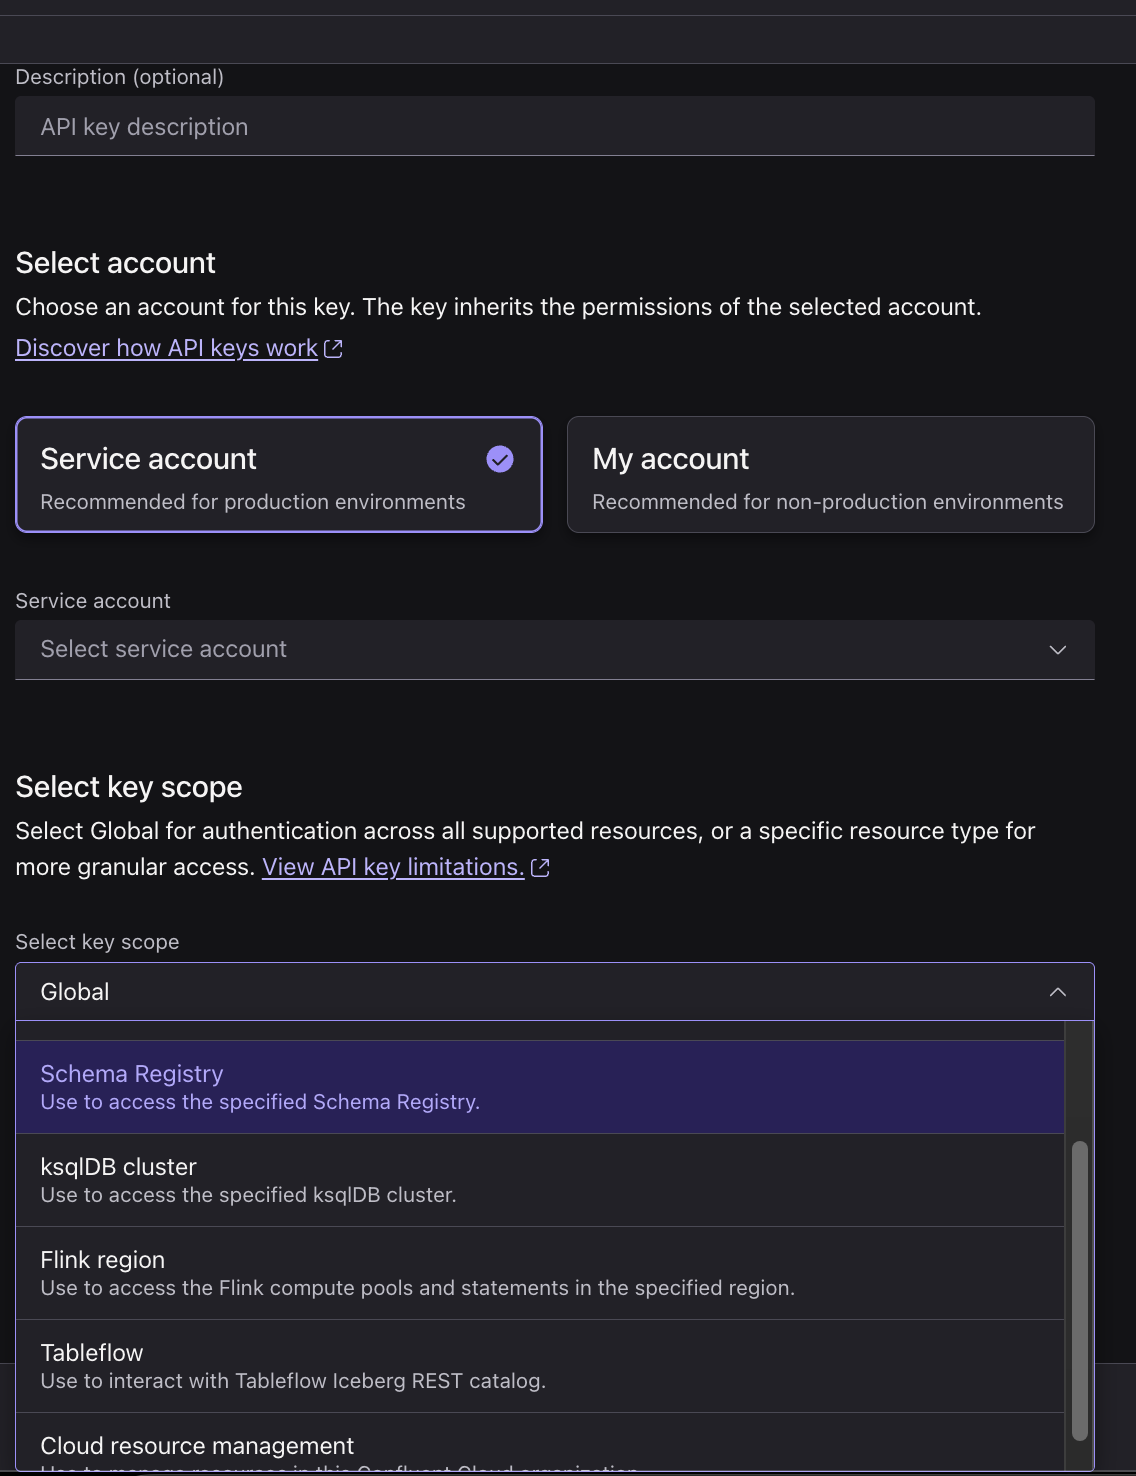
Quality of life improvements
- Added indexer watchdog that restarts indexer tasks if there is no indexer update for more than 10 minutes. See Indexer watchdog properties.
- Moved the topic cleanup policy setting into Advanced configuration in the topic creation form.
Upgrade to JRE 25
Console now runs on Java Runtime Environment (JRE) 25, replacing Eclipse Temurin Java Development Kit (JDK) 21. Both are long-term support (LTS) releases. This is a runtime change only — Console features and configuration are unchanged.If you build your own imageFROM the Console image, or set custom JVM options, verify any custom JAVA_OPTS against the JVM options removed or obsoleted across JDK 22–25: an unrecognized flag prevents the JVM from starting.Console now ships a JRE rather than a full JDK, so the JDK command line tools, such as jcmd, jstack and jmap, are no longer in the image, see conduktor/conduktor-debug image instead.Navigate between resources more quickly
Console’s sidebar has been reorganized into clearer expandable groups, with collapsed flyouts. App startup and route transitions now use responsive loading states, including an app shell skeleton and delayed in-page indicators, for a faster and smoother navigation experience.Topic, subject, consumer group and connector breadcrumbs now include recently viewed resources from the current cluster, making it quicker to switch between related resources without returning to a list page.Improved message workflows
- You can now reprocess a message from its standalone topic message page.
- CSV import now helps select subjects for Avro and JSON Schema serialization strategies.
Leadership diagnostics
Administrators can use the new Settings > Diagnostics > Leadership page to see which Console instance is the current leader and copy diagnostic values when troubleshooting a high-availability deployment.Smaller, hardened container images
Theconduktor/conduktor-console base image moves from eclipse-temurin:21-jdk-noble to a custom Chainguard Wolfi openjdk-25-jre image built with apko. Wolfi ships fewer packages and patches them faster, which cuts the number of common vulnerabilities and exposures (CVEs) reported against the image.We also cleaned up the image layers and removed the debug tools that shipped with previous releases. Together, these changes bring the compressed image size down from 860MB to 475MB and reduce the attack surface.We removed ldap-utils, nano, bind9-dnsutils, netcat, procps, gpg, gzip, tar and gettext. If you rely on any of them — for example to troubleshoot inside a running container — use the new conduktor/conduktor-debug image instead, which carries these tools and many more.To reach these tools in Kubernetes, the Console Helm chart in this release adds a debugSidecar helper that runs conduktor/conduktor-debug alongside the Console and Cortex pods. Turn it on when you need to investigate, and the tools are available in the pod without any change to the Console image itself. Find out more about troubleshooting with the debug sidecar.The conduktor/conduktor-console-cortex image moves to Wolfi too, from ubuntu:26.04. It now runs repackaged Cortex and Prometheus builds from our own forks, which backport upstream CVE fixes.We build the base, Cortex and debug images from open source definitions in the conduktor/container-images repository, so you can audit exactly what goes into them.Fixes
- Fixed timeout issue when indexing schemas from Karapace Schema Registry
- Partition skew value in Risk Analysis is now bounded to 0-100% and comparable across topics regardless of partition count
- Fixed an issue where ACLs with different hosts were merged into a single row
- Fixed an issue where the
KafkaTopicsAclReadpermission granted onAll clustersdidn’t apply to individual topics, hiding ACLs from affected users - Improved logging for misconfigured webhooks to make them easier to debug, and significantly decreased log noise from SSL handshake failures
- Fixed Self-service access workflows: duplicate requests are prevented, users with both permissions see Grant access and Request access, and external-group synchronization repairs missing permissions
- The Application instance view of Stream lineage no longer shows dangling service accounts on resources an application instance owns when the service account isn’t managed through an application instance
- Fixed consumer-group TimeLag alerts remaining healthy when some partition lags were unavailable
- Fixed topic-message exports with semicolon-containing fields or custom deserializers
- Chargeback indexing now recovers when a Gateway becomes available again
- Fixed broker key-metric graphs failing with HTTP 422 when Cortex contains duplicate time series
- Added the missing Stop action for self-managed Kafka Connect connectors in Console, with Resume available for stopped connectors
Lineage performance enhancements
Stream lineage has been rebuilt to handle large clusters. Graphs draw in a couple of seconds, panning and zooming stay smooth even with thousands of resources on screen, and the page stays responsive while the graph is arranged.Some of these improvements change what you see on screen:- Very large graphs show more of your resources. Console now keeps the 5,000 most connected resources, up from 1,000, and draws the most significant connections between them. A banner tells you when the graph has been trimmed.
- Zoomed out, the graph shows less detail. Names, icons and counts on each card give way to plain colored blocks with placeholder bars, and the labels on connections disappear. This is what keeps a big graph smooth — zoom in and the full detail comes back.
- The layout looks different. Cards are spread more evenly and no longer overlap, so a graph you knew from 1.46 will be arranged differently.
- In crowded areas, a few connection labels are skipped so they don’t print on top of each other. The connections themselves are still drawn.
- Clicking a resource highlights it and moves the view to it instead of replacing the graph. To open the focused view of a resource, click Expand in the sidebar. Your zoom and scroll position are remembered when you come back from a drill-down.
- Quick refreshes no longer dim the page. The loading overlay only appears when loading takes longer than half a second; faster refreshes show a thin progress bar at the top instead.
Security advisories
Console v1.47.0 is flagged by image scanners (Trivy, Grype) for seven findings against thebusybox, openssl and glibc packages in its base image. Both the conduktor/conduktor-console and conduktor/conduktor-console-cortex images are affected, as they share the same base. None of these findings have a practical impact on Console: the affected code either isn’t present in the images or is never reached by Console.Scanners label these findings High or Critical. Those ratings aren’t accurate here: OpenSSL rates both of its issues Low, the BusyBox issues score Medium, and of the two glibc findings one is formally disputed and the other is rated a minor issue by Debian.BusyBox- CVE-2026-38753 — use-after-free in the
awkapplet, triggered by a crafted AWK script - CVE-2026-38754 — heap overflow in the
ashshell, triggered by crafted input - CVE-2026-38755 — heap overflow in the
ashshell, triggered by crafted input
bash, gawk and coreutils, which provide these commands instead, and the vulnerable BusyBox applets are not installed. Each issue also requires passing a crafted script or input to the affected tool, which Console never does with untrusted input.OpenSSL- CVE-2026-14456 — unbounded memory growth in a QUIC server accepting new connections
- CVE-2026-54876 — memory leak in a TLS client that has OCSP response checking explicitly enabled, when it connects to a malicious server
- CVE-2019-1010022 — reported bypass of stack guard protection
- CVE-2026-5450 — one-byte heap overflow in the
scanffamily, using the%mcspecifier with a width over 1024 characters
scanf, and neither the Cortex nor Prometheus binaries are affected, as Go programs don’t use glibc for parsing. Debian rates the issue minor and has issued no advisory for it. A fix has been released upstream and will reach Console once it lands in the base image.We will fix the BusyBox, glibc, and OpenSSL findings in the next version of Console if fix versions are available.- Breaking changes
- Behavior changes
- New and updated features
- Incremental fetch sessions are now generally available
- Local service accounts now support SCRAM credentials
- Gateway now authenticates to upstream Kafka with OAuthBearer client assertions
- HAProxy Protocol client address has been added to more audit events
- Topic views now support more SQL syntax
- New client metrics Interceptor forwards KIP-714 telemetry to OTLP
- Dynamic header injection Interceptor now supports the consume path
- Gateway now reads and writes schema IDs in record headers
- Preview features
- Deprecated features
- Quality of life improvements
- Fixes
- Known issues
- Security advisories
Breaking changes
/health endpoint (deprecated) has been removed
The legacy /health endpoint — deprecated in v3.12.0 — has been removed in this release, so any health check still polling it fails. Update those checks before you upgrade.Use the dedicated probes instead: /health/live (liveness) and /health/ready (readiness). See the monitoring setup documentation for the probe endpoints.v1 API (deprecated) has been removed
The v1 Gateway admin and internal REST APIs were deprecated in v3.15.0 and have been removed in this release.If you still call the v1 API, migrate to the v2 API before you upgrade. It has been available since Gateway 3.3.0, which is when the Conduktor CLI gained support for it.If you manage Gateway through Console, upgrade Console to 1.44.0 or later first — that’s the first version to use the v2 API.The v1 reference stays available for older Gateway versions — see Removed APIs.Large batch handling Interceptor (deprecated) has been removed
TheLargeBatchHandlingPlugin (io.conduktor.gateway.interceptor.LargeBatchHandlingPlugin) was deprecated in v3.18.0 and has been removed in this release.Any existing configurations using this plugin are ignored and log an error message after upgrading to v3.21.0, until you delete those Interceptor configurations.See the removed Interceptors reference for the original documentation.Recommended alternative: Use the large message handling plugin instead. It offloads individual messages above the size threshold and takes the same configuration (s3Config/azureConfig, minimumSizeInBytes, localDiskDirectory).HAProxy Protocol audit event fields have moved
With HAProxy Protocol enabled (GATEWAY_FEATURE_FLAGS_HAPROXY_PROTOCOL=true), CONNECTION audit events reported the original client address in eventData. It now sits in the connection block, for this event and for other event types.Before:Behavior changes
Encryption Interceptors now prefer declared Vault credentials over VAULT_TOKEN
Encryption Interceptors now authenticate with the credentials their Vault configuration declares. VAULT_TOKEN is now only a fallback: Gateway reads it when an Interceptor declares no credentials and VAULT_AUTH_TYPE is unset.When credentials are declared and VAULT_TOKEN is also set:- Before: Gateway used
VAULT_TOKENonly. - Now: Gateway uses the declared credentials only, so those credentials have to be valid.
token: ${VAULT_TOKEN} (or declare no credentials) to stick to using the environment variable.See the data security documentation for the supported Vault authentication types. Schema ID headers are no longer encrypted
Gateway relies on the__key_schema_id and __value_schema_id headers it now reads and writes to resolve schemas, so it never encrypts them.When a header encryption pattern matches those names, such as header: ".*":- Before: Gateway encrypted them, and decryption restored them.
- Now: Gateway skips them on both paths, so records encrypted by an earlier release keep an encrypted schema ID header their consumers can’t resolve.
Incremental fetch sessions change three Interceptor behaviors
Incremental fetch sessions are now on by default. Three Interceptor behaviors differ on an unchanged deployment after you upgrade:- Deprecated SQL and CEL logical topics return incorrect results. Topic views aren’t affected.
- Fetch policies are validated when a session opens rather than on every fetch.
- The audit Interceptor records a fetch only when the request lists topics, so a steady-state consumer can look idle in audit logs.
GATEWAY_FEATURE_FLAGS_INCREMENTAL_FETCH_SESSIONS_ENABLED=false. See incremental fetch sessions for the flag and its default. Interceptors now validate AWS Glue schema registry credentials
validateCredentials in the shared schema registry configuration now defaults to true, matching the AWS SDK. The SDK check is local — it rejects a blank accessKey or secretKey rather than verifying them with AWS. Anything that reads schemas from AWS Glue is affected: encryption, data masking, header injection, topic views and the schema-aware Safeguard policies. When accessKey or secretKey resolves to an empty string, usually an environment variable that exists but holds no value:- Before: Gateway accepted the blank value and failed at its first Glue call, usually during interception.
- Now: Gateway reports
Access key ID cannot be blank.orSecret access key cannot be blank., logs the rejection, and the Interceptor doesn’t load.
basicCredentials block to fall back to the AWS default credential chain, or set validateCredentials to false to keep the previous behavior.Topic views now reject unsupported SQL
Gateway now validates a topic view statement against the exact set of SQL constructs it evaluates, and rejects anything else when you create or update the view.When a statement falls outside that set:- Before: Gateway accepted the view and ignored what it couldn’t evaluate — often a
WHEREpredicate that never filtered, so the view returned every record. - Now: Gateway rejects the view and logs an error quoting the statement. The rest of your configuration loads normally.
New and updated features
Incremental fetch sessions are now generally available
Incremental fetch sessions (KIP-227) graduate from preview to general availability and are now enabled by default. A consumer opens a session with one full Fetch request, then sends only the partitions that changed on each later request, which lowers Fetch overhead for consumers that read from many partitions.GATEWAY_FEATURE_FLAGS_INCREMENTAL_FETCH_SESSIONS_ENABLED now defaults to true and stays available as an operational opt-out. Topic ID support — a preview feature, off by default — can’t run alongside it: Gateway doesn’t start with both flags on, so enabling topic ID support means setting this flag to false.Three Interceptor behaviors change — see breaking changes before you upgrade.See incremental fetch sessions for the flag and its default. Local service accounts now support SCRAM credentials
Local service accounts can now authenticate with long-livedSCRAM-SHA-512 or SCRAM-SHA-256 credentials managed by Gateway, as an alternative to the short-lived PLAIN token. Gateway derives a verifier from the password you supply and stores only that verifier, never the clear password. Unlike tokens, SCRAM credentials don’t expire, which suits long-running clients.Enable the feature with GATEWAY_FEATURE_FLAGS_SERVICE_ACCOUNTS=true. Gateway-managed SASL listeners then advertise the SCRAM-SHA-512 and SCRAM-SHA-256 mechanisms alongside PLAIN, and new endpoints let you add, list, and revoke a service account’s SCRAM credentials. The same ACLs and Interceptors apply as for token-based authentication.See the Gateway service accounts tutorial for how to give a service account SCRAM credentials.Gateway now authenticates to upstream Kafka with OAuthBearer client assertions
Gateway can now authenticate to upstream Kafka clusters with OAuthBearer and a Private Key JWT (client assertion). Configure theKAFKA_SASL_OAUTHBEARER_ASSERTION_* environment variables to point to your private key and set the JWT claims. This uses native Kafka support from KIP-1258.See the Connect Gateway to Kafka documentation for the client assertion configuration.HAProxy Protocol client address has been added to more audit events
When Gateway sits behind a load balancer that sends the HAProxy Protocol header, the original client address now appears on every audit event type that reports a connection — AUTHENTICATION, APIKEYS_REQUEST, SAFEGUARD, INTERCEPTOR and ACL_ADMIN — not only CONNECTION. It’s reported in the event’sconnection.proxyConnection field, alongside the load balancer’s address — the same relocation that changes where CONNECTION events report it.The {{userIp}} header templating variable also now resolves to this original client address instead of the load balancer’s.See the load balancing documentation for how to capture the client IP address.Topic views now support more SQL syntax
Topic views support more SQL in this release:- Nested JSON output:
JSON_OBJECTin theSELECTclause, nested to any depth. IN/NOT IN: match a field against a literal list in theWHEREclause, for examplecountry IN ('UK', 'US').!=: accepted alongside<>.
New client metrics Interceptor forwards KIP-714 telemetry to OTLP
The new client metrics Interceptor terminates KIP-714 client telemetry in Gateway and forwards it to an OpenTelemetry (OTLP) collector, enriched with Gateway identity labels such asclient_id, principal and vcluster. Kafka clients from 3.7.0 onward push these metrics by default, so you collect producer and consumer health without changing client code and without any KIP-714 setup on your brokers.See the client metrics Interceptor reference for the OTLP exporter settings.Dynamic header injection Interceptor now supports the consume path
The dynamic header injection Interceptor now supports the consume path as well as produce. A newtarget field accepts PRODUCE, CONSUME or BOTH.See the data security documentation for the target field.Gateway now reads and writes schema IDs in record headers
Gateway now reads schema IDs from the__key_schema_id and __value_schema_id record headers as well as the value prefix, the format introduced in Confluent Platform 8.2, and writes them back the same way. Field-level encryption leaves those headers alone.Preview features
External connections for schema registries and KMS providers
External connections centralize the connection details Interceptors previously carried themselves. Gateway declares a connection to an external system once at startup, and Interceptors and topic views reference it by name instead of each holding its own copy of the address and credentials. Declare one withGATEWAY_EXTERNAL_CONNECTION_<NAME>_CONFIG_<PROPERTY> environment variables.This is a preview feature and is subject to change. Inline configuration remains fully supported.Two kinds of connection ship: schema registries and KMS providers.Schema registry connections can be named by two kinds of resource:- Topic views name a connection with
spec.schemaRegistryConnectionName, which lets them filter Avro, Protobuf and JSON-Schema records rather than only schema-less JSON. This is the only way to give a topic view a schema registry. - Interceptors that read schemas name a connection with
schemaRegistryConnectionName, as an alternative to their ownschemaRegistryConfig. Inline configuration keeps working and isn’t deprecated.
kmsConnectionName, as an alternative to an inline kmsConfig. Two providers are available as a connection:- HashiCorp Vault, authenticating with:
- a token
- AppRole
- a username and password
- AWS KMS, authenticating with:
- access keys
- temporary credentials
- the AWS SDK’s default provider chain
Deprecated features
convert_json schemaDataMode is deprecated for Avro records
Deprecated in: v3.21.0. Removal planned for v3.24.0.The convert_json value of the field-level encryption schemaDataMode setting is deprecated. It converts Avro records to JSON when Gateway encrypts them, which breaks the link to their schema in the backing topic. Use preserve_avro instead, the default since v3.3, which keeps the record in Avro and preserves that link.Existing configurations continue to work without changes, but Gateway now logs a deprecation warning when it loads an Interceptor that sets convert_json.See the data security documentation for the schemaDataMode options.offsetCorrectness on concentrated topics is deprecated
Deprecated in: v3.21.0. Removal planned for v3.24.0.The spec.offsetCorrectness flag on ConcentrationRule is deprecated. It makes concentrated topics report virtual offsets, so that lag and message count read correctly.Existing deployments continue to work without changes. Gateway now logs a single deprecation warning at startup listing the affected concentrated topics.If you have offsetCorrectness enabled in production, get in touch for support with this migration.Quality of life improvements
- Gateway now rejects invalid ACL bindings (such as an
ANYorMATCHpattern type, or a malformed principal) at creation instead of silently ignoring them, matching Apache Kafka behavior. A storedMATCHbinding previously brokeDescribeAclsfor the whole cluster. See the Gateway authentication and authorization documentation for how Gateway ACLs work. - Gateway now stores ACL bindings in batches, so large
CreateAclsrequests complete much faster and no longer hold up other clients.
Fixes
- Gateway now fails to start when SNI routing targets multiple clusters but a host pattern is missing
{{physicalCluster}}, instead of silently routing everything to the first cluster. See the Gateway listener documentation for how SNI routing works. - Clients generated from the Gateway v2 OpenAPI spec can now deserialize service account responses.
- Gateway now distributes work more evenly across pooled upstream connections.
Known issues
- Topic ID support: with the
GATEWAY_FEATURE_FLAGS_TOPIC_ID_SUPPORTfeature flag on and one or more Virtual Clusters configured, a client holding an ALLOW ACL can intermittently receiveTOPIC_AUTHORIZATION_FAILED. Topic ID support stays in preview, with the feature flag off by default, until the fix ships. - Cache Interceptor: the cache Interceptor doesn’t support incremental fetch sessions, which are on by default since v3.21.0. If you use it, set
GATEWAY_FEATURE_FLAGS_INCREMENTAL_FETCH_SESSIONS_ENABLED=false.
Security advisories
The following advisories will be addressed in the next release, or as soon as upstream dependencies allow:- CVE-2026-40984 — against Micrometer’s HTTP server instrumentation, flagged by image scanners. Gateway uses Micrometer as its metrics framework but not that module, so the vulnerable code path isn’t reachable in Gateway.
- CVE-2026-41254 — against the Eclipse Temurin JDK 25 base image, flagged by image scanners. The vulnerable code path is in the Little CMS color management library bundled with the JDK, and is unreachable in Gateway.
- CVE-2026-45799 — against
wire-runtime, which reaches Gateway through Confluent’s Protobuf schema provider. The advisory covers any Wire-decoding service, so Gateway v3.21.0 is affected.
Updated features
Configurable HTTP request timeout
The Console HTTP request timeout is now configurable through the newCDK_PLATFORM_HTTP_REQUESTTIMEOUTSECONDS environment variable (property: platform.http.requestTimeoutSeconds). Increase the timeout to accommodate long-running requests behind slow upstream systems, or lower it to fail faster in environments with tight service-level objectives.Faster ApplicationInstance applies on Confluent clusters using role bindings
For Confluent Cloud and Confluent Platform clusters configured to use role bindings (rather than ACL mode), applying an ApplicationInstance now skips role binding API calls when the ApplicationInstance has no state change, and issues the remaining calls in parallel. This cuts apply time on unchanged instances and speeds up applies that do have work to do.Fixes
- Improved performance of the ApplicationGroup API.
- Improved transactionality and rollback behavior of the ApplicationGroup API.
Updated features
Configurable HTTP request timeout
The Console HTTP request timeout is now configurable through the newCDK_PLATFORM_HTTP_REQUESTTIMEOUTSECONDS environment variable (property: platform.http.requestTimeoutSeconds). Increase the timeout to accommodate long-running requests behind slow upstream systems, or lower it to fail faster in environments with tight service-level objectives.Faster ApplicationInstance applies on Confluent clusters using role bindings
For Confluent Cloud and Confluent Platform clusters configured to use role bindings (rather than ACL mode), applying an ApplicationInstance now skips role binding API calls when the ApplicationInstance has no state change, and issues the remaining calls in parallel. This cuts apply time on unchanged instances and speeds up applies that do have work to do.Preview features
RBAC on labels
Early access to role-based access control (RBAC) on labels is available in this release. Contact your Conduktor account team if you’d like to try it. Full documentation will be published with the v1.47.0 release.Fixes
- Fixed a regression in group membership reconciliation during single sign-on (SSO) login that affected some SSO providers.
- Improved performance of the ApplicationGroup API.
- Improved transactionality and rollback behavior of the ApplicationGroup API.
Security advisories
Console v1.46.1 is flagged by image scanners (Trivy, Grype) for CVE-2026-54512 and CVE-2026-54513 againstcom.fasterxml.jackson.core:jackson-databind. Both findings have no practical impact on Console.Console’s own jackson-databind is already patched (2.21.4 and 3.2.0). The flagged 2.15.2 version comes from a copy of jackson-databind that is shaded and relocated inside a graph library Console uses internally to support stream lineage. Its classes are not on the classpath as com.fasterxml.jackson.databind.*, so the vulnerable code paths can’t be reached from Console. The library uses its shaded copy for internal serialization, not for deserializing attacker-controlled input.We intend to address this finding in the next major Console release.Breaking changes
Cortex alert manager port
Theconduktor/conduktor-console-cortex image now exposes the alert manager API on port 9009 instead of 9010. This follows the Cortex upgrade from 1.18 to 1.21, which also upgrades Prometheus from 2.54 to 3.8.You’re impacted if
You deploy theconduktor/conduktor-console-cortex image and configure CDK_MONITORING_ALERT-MANAGER-URL (or monitoring.alert-manager-url in YAML) with port 9010.If you deploy with the Console Helm chart console-1.31.0 or later, the chart applies the new port for you and you don’t have to do anything. When
platformCortex.enabled is true, the chart always points Console at port 9009: setting config.monitoring.alert-manager-url has no effect, and setting the same variable through platform.extraEnvVars fails the release with a duplicate key error.What you have to do
Change the port from9010 to 9009:CDK_MONITORING_CORTEX-URL. If you publish or allow-list the Cortex container ports — in a Docker Compose file, an AWS security group or a Kubernetes network policy — you can also drop port 9010.New and updated features
Stream lineage
Stream lineage gives you an interactive map of how data flows across your Kafka estate, with the topics, applications, and service accounts that produce or consume each stream rendered side by side. Use it to trace how a topic is being read and written across applications, identify which service accounts depend on a given topic, and investigate the downstream impact of a topic or application change.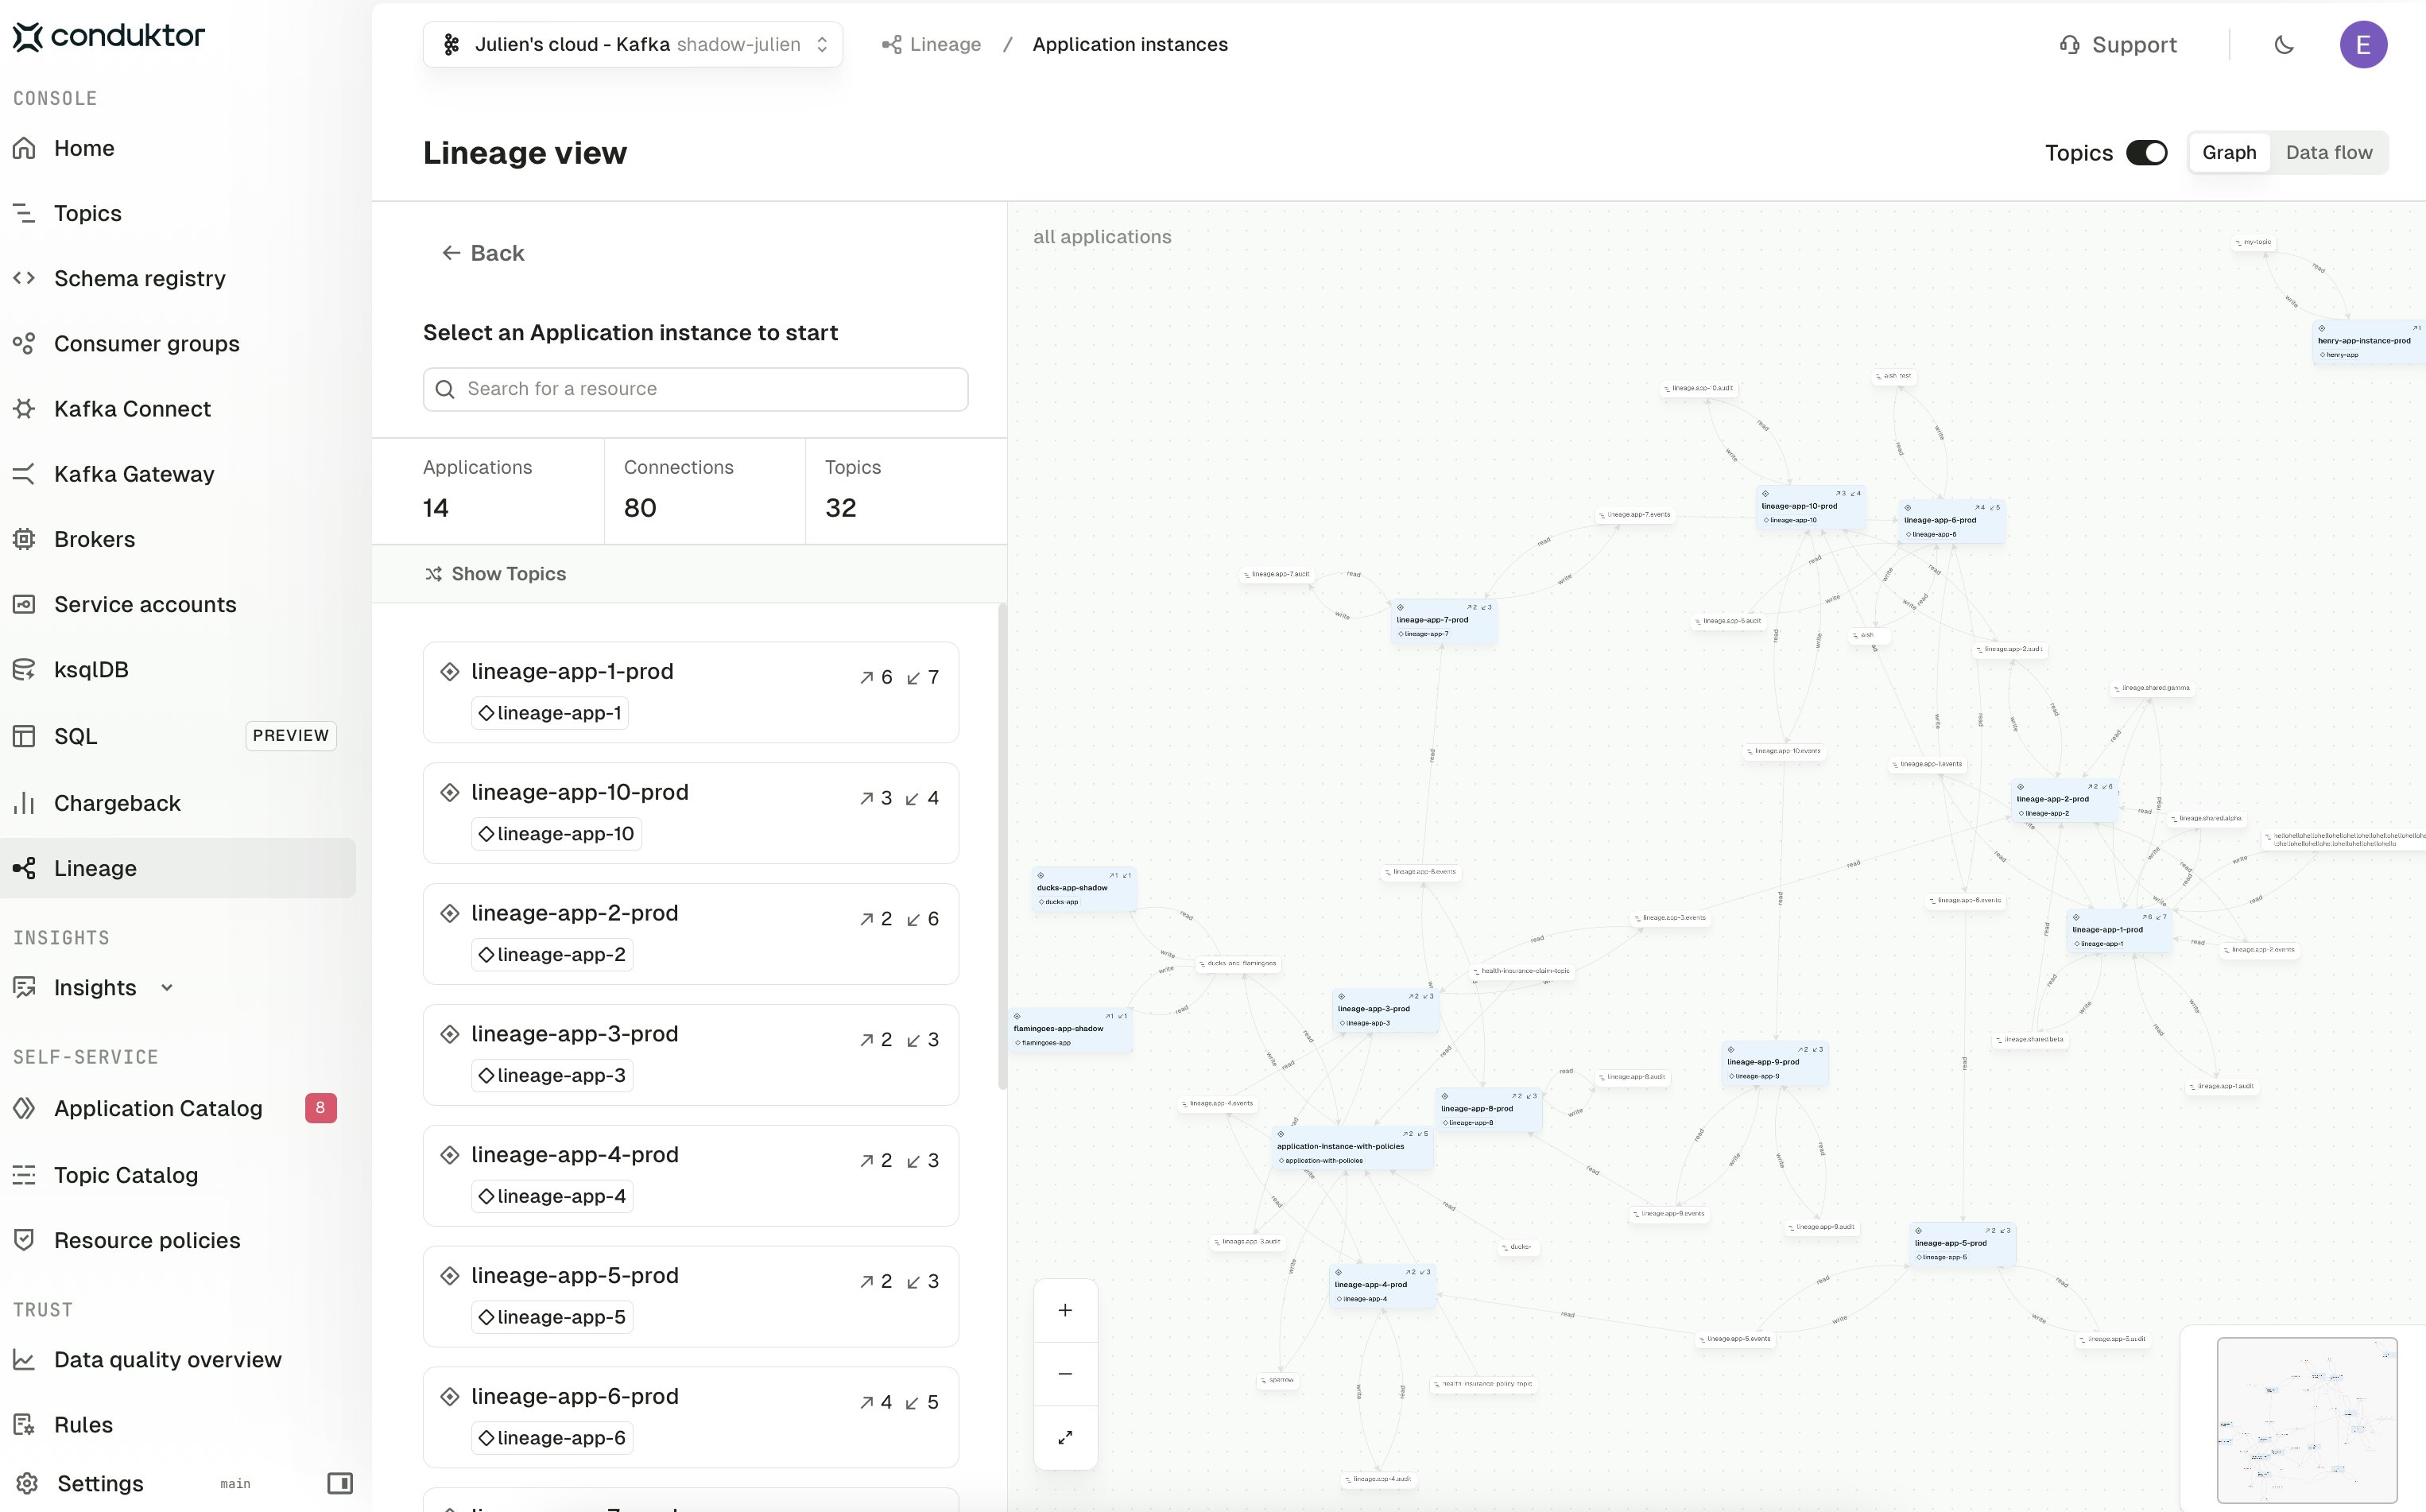
ApplicationInstance and ApplicationInstancePermission resources — so it stays in sync with the model you’ve declared in Console. On Confluent Cloud and Confluent Platform clusters configured to use role bindings, the edges are populated from those role bindings instead.Stream lineage offers two ways to explore your platform:- Application instance view — see how Self-service applications connect through the topics they share, with a Topics toggle to either include the topics on the graph or collapse them into a compressed application-to-application view
- Service account view — reason about access at the Kafka authorization layer, with each service account as a node and edges drawn straight from the ACLs that grant read or write access to a topic
CDK_STREAM_LINEAGE_* environment variables to tune the in-memory graph cache.Kafka Connect lifecycle and offsets
- You can now stop a Kafka Connect connector. Stopping a connector releases its tasks and resources, unlike pausing, which keeps them assigned. Manage the new
STOPPEDstate from the connector page or the public API. - The connector page has a new Offsets tab to view a connector’s source and sink offsets. To edit or reset offsets, use the public API while the connector is stopped to control where it resumes from.
- You can set the initial state of a connector when you create it. Set
initialStatetoRUNNING,PAUSED, orSTOPPEDto deploy a connector without immediately starting it.
Consumer group protocol reporting
Consumer group descriptions now report the group type and protocol (CLASSIC or CONSUMER) introduced by the next-generation consumer group protocol (KIP-848), so you can tell at a glance which clients have moved to the new protocol.Mask all fields in a data masking policy
Data masking policies now have a Mask all fields toggle. When enabled, Console applies the policy’s masking rule to every scalar value it finds in a message — at every nesting depth, including inside arrays — without you needing to enumerate field paths. Numbers are masked to0 and booleans to false so message schemas stay valid; per-field policies that target specific paths still take precedence.
Permission management
-
Topic owners can now be given access to view the ACLs on their owned topics without needing a cluster-wide permission. To view topic ACLs, a user has to be granted one of:
clusterViewACLon the related cluster (classic RBAC), which continues to cascade ACL viewing to every topic in the cluster, or- one of the Self-service application instance permissions
applicationInstancePermissionGrantAccessorapplicationInstancePermissionProposeAccess, assigned through an application group on the owningApplicationInstance.
- Three new Kafka Connect permissions let you grant connector stop and offset operations independently of pause, resume, and restart: stop a connector, view offsets, and manage offsets. These default to off for existing custom roles, so existing permission grants are unchanged until you opt in.
Resource templates
Platform teams can now define topic and connector templates that pre-fill the Console creation forms. Admins curate templates with the CLI — set a display name, an optional description, and the default partitions, replication factor, configuration and labels — and application teams pick one to start from a vetted setup instead of a blank form, adjusting the values before they submit. Templates can include{{placeholder}} values, such as a team name in a topic naming convention, that the user replaces during creation. Templates are suggestions, not rules: pair them with a ResourcePolicy to enforce the boundaries.See the TopicTemplate and ConnectorTemplate reference for the YAML schema.Chargeback
- Chargeback is now enabled by default. The
CDK_CHARGEBACKV2_ENABLEDenvironment variable defaults totrue; set it tofalseto disable Chargeback. - Chargeback now attributes Kafka Connect costs. Set a default connector task hour cost per cluster, with optional per-connector-class overrides, then view Connect costs in the cluster, application, and label views and drill down into individual connectors.
- Connectors that carry a Chargeback Label can now be grouped and filtered in the Chargeback label view.
- The Chargeback CSV export now includes connector task hours and connect cost columns.
- The Chargeback public API now exposes endpoints to manage cost rates and Chargeback Labels, and to export Chargeback data as CSV.
Public API changes
- The public API now exposes connector lifecycle operations: stop, pause, resume, restart, and offset management (view, edit, reset).
- The public API now exposes consumer group operations: describe a group, view its members and topics, delete a group, and preview or reset offsets.
- The Chargeback public API now exposes endpoints to manage cost rates and Chargeback Labels, and to export Chargeback data as CSV. See the Chargeback section for the full set of related changes.
Quality of life improvements
- Export includes Kafka headers
Fixes
- Consumer offset retrieval no longer fails when some partition leaders are offline
- Consumer page date-time filters now display time in local time instead of UTC
- SSO test for Azure Entra ID shows explanation why group or email claims are missing
- Added
CORTEX_COMPACTOR_RETENTION_PERIODenvironment variable - Support nested OIDC group claim
- Breaking changes
- New and updated features
- Preview features
- Deprecated features
- Quality of life improvements
- Fixes
- Security advisories
Breaking changes
Mixed network configuration
Gateway now refuses to start if you mix legacy network configuration variables with listener configuration variables. Previously, the legacy variables were silently ignored in that case. See Migrate to listener configuration for a side-by-side mapping and a worked example.Internal Kafka client upgraded to 4.2
Gateway now uses the Apache Kafka client 4.2 internally, upgraded from 3.9. This drops support for the oldest client protocol versions, so applications connecting to Gateway need a Kafka client of at least Apache Kafka 2.1 for the Java client, or the equivalent for other libraries (see KIP-896). Only clients older than that are affected. It does not change the minimum Kafka broker version that Gateway supports. We expect low impact for most deployments.Gateway does not yet support the new Kafka 4 group protocols and now blocks them for every client, in both API blocking modes:
- Share groups (KIP-932), also known as Kafka queues.
- Streams groups (KIP-1071), the new Kafka Streams rebalance protocol.
GATEWAY_FEATURE_FLAGS_BLOCK_UNSUPPORTED_APIS=false, Gateway passed the KIP-932 share-group APIs through to the backing Kafka cluster. They’re now always blocked. See API blocking modes.New and updated features
New listener configuration GA
The new configuration format supporting multiple listeners withGATEWAY_LISTENER_<NAME>_* environment variables is now generally available. It graduates from preview to the recommended way to configure Gateway networking.The same configuration can define one or many listeners. Each listener has its own security protocol, routing strategy and network bindings, letting you expose Gateway through multiple endpoints (for example, internal PLAINTEXT and external SASL_SSL) when needed.With listener configuration, GATEWAY_SECURITY_MODE and GATEWAY_ACL_ENABLED have to be set explicitly — they’re no longer inferred from the backing Kafka cluster.See Configure Gateway listeners.Topic views GA
Topic views graduate from tech preview to general availability and are now enabled by default. They provide non-materialized, SQL-filtered views of physical Kafka topics.Building on the 3.19.0 preview, topic views now also support:- Consumer
group.idvalidation to prevent the silent data loss that can occur when a consumer group is shared across views of the same backing topic. See Set the consumer group ID. - Expanded SQL: date and time comparisons, record metadata in the
SELECTclause, and parse-time rejection of unsupported multi-value field paths. See SQL transformation. onErrorenforced at fetch time, includingFAIL_FETCH. See Error handling.
- Views with invalid SQL are rejected. Most views created in the tech preview keep working. Recreate any that Gateway rejects with valid SQL.
- Existing consumer groups stop working. Their
group.iddoesn’t follow the new convention, so create a new group with agroup.idthat does. See Set the consumer group ID. A new group starts with no committed offsets. If you use Console, you can duplicate the existing group under the new name to keep its position.
Faster ACL authorization
ACL evaluation is now more efficient, especially on clusters with many ACLs. Authorization decisions are unchanged.Preview features
Incremental fetch sessions
Gateway can now support Apache Kafka incremental fetch sessions (KIP-227) on the Fetch API, behind a feature flag. Incremental fetch sessions let a consumer send only the partitions that changed after it opens a session, which lowers Fetch request overhead for consumers that read from many partitions.Enable it withGATEWAY_FEATURE_FLAGS_INCREMENTAL_FETCH_SESSIONS_ENABLED=true. You can’t combine it with topic ID support. See incremental fetch sessions for setup and limitations.Deprecated features
Legacy network configuration
Deprecated in:v3.20.0. Removal planned for v3.23.The global GATEWAY_PORT_*, GATEWAY_ADVERTISED_HOST, GATEWAY_HOST, GATEWAY_ROUTING_MECHANISM, GATEWAY_BIND_HOST, GATEWAY_ADVERTISED_SNI_PORT, GATEWAY_ADVERTISED_HOST_PREFIX, GATEWAY_SNI_HOST_SEPARATOR and GATEWAY_SECURITY_PROTOCOL environment variables are deprecated. New deployments should use listener configuration.Existing deployments continue to work without changes, but Gateway now logs a deprecation warning at startup when it detects any of these variables, pointing to the migration guide.When you’re ready to migrate, see Migrate to listener configuration for a side-by-side mapping and a worked example.Quality of life improvements
Upgrade to JDK 25
Conduktor Gateway now runs on JDK 25, replacing JDK 21. Both are long-term support (LTS) releases. This is a runtime and toolchain change only — Gateway features and configuration are unchanged — and it is low impact for most deployments. The runtime base image moves fromeclipse-temurin:21-jdk to eclipse-temurin:25-jdk.If you build your own image FROM the Gateway image, or set custom JVM options, verify any custom JAVA_OPTS against the JVM options removed or obsoleted across JDK 22–25: an unrecognized flag prevents the JVM from starting.Automatic OAuth URL allow-list
The Kafka 4 client library adds a security control: theorg.apache.kafka.sasl.oauthbearer.allowed.urls system property. The OAuth or OpenID Connect (OIDC) client only calls a URL that’s on this allow-list and refuses any URL that isn’t. Now that Gateway’s internal Kafka client is on 4.2, this property applies to Gateway too.Gateway sets the property automatically at startup from the OAuth URLs you already configure: the downstream JSON Web Key Set (JWKS) endpoint and any upstream token endpoints. OAuth authentication continues to work after the upgrade with no extra JVM argument.To control the allow-list yourself, for example to add or restrict URLs, you can still set the property manually, which overrides the value Gateway derives.Fixes
- Include async-profiler to help investigating performance issue
- Secret env vars whose values start with a YAML-special character (such as
[) no longer cause Gateway to fail at startup. Affected vars:GATEWAY_SSL_KEY_STORE_PASSWORD,GATEWAY_SSL_KEY_PASSWORD,GATEWAY_SSL_TRUST_STORE_PASSWORD,GATEWAY_HTTPS_KEY_STORE_PASSWORD,GATEWAY_HTTPS_TRUST_STORE_PASSWORD,GATEWAY_CONFLUENT_CLOUD_API_SECRET,GATEWAY_USER_POOL_SECRET_KEY. - Fix process hang when startup or shutdown fails
- Prevent reprocessing of deleted interceptor configuration on startup
Security advisories
Gateway v3.20.0 is affected by CVE-2026-45799. We will address it in a future release once our upstream dependencies allow.Fixes v1.44.2
- Fixed erroneous “subject not found” errors appearing in the topic record detail view when the subject exists.
CVEs in conduktor-console-cortex
Three CVEs are flagged as high severity in the Cortex container image:- CVE-2026-34040
- CVE-2026-41567
- CVE-2026-42306
CVE-2026-34040
This exploit involves an AuthZ plugin bypass in the Docker daemon HTTP API middleware. Cortex doesn’t embed or run dockerd, so it isn’t affected.CVE-2026-41567 and CVE-2026-42306
Both CVEs relate to thedocker cp command and its implementation in dockerd. Cortex doesn’t embed or run dockerd, so it isn’t affected.New features
Gateway Community Edition
Conduktor Gateway introduces a new edition: Gateway Community Edition — a Kafka-managed passthrough proxy with no Gateway-managed features. Standard Conduktor Gateway licenses are unaffected by this release.See Gateway Community Edition for included capabilities, excluded features, customer-visible restrictions, and how to obtain a license.Security advisories
This release resolves CVE-2026-22016 (Java API for XML Processing) and CVE-2026-34282 (Networking), both flagged in Gateway v3.19.0.Fixes
- Fixed an issue where Chargeback did not attribute costs to applications managed through Self-service in the service accounts panel.
- Fixed a Chargeback issue where costs could be assigned to the wrong day for users in non-UTC timezones.
Security advisories
- Updated the JDK 21 base image to include upstream patches for CVE-2026-34282.
- Updated the bundled Netty dependency to address recently disclosed CVEs.
Breaking changes
Self-service owner group permissions
Starting with Console 1.45.0, application owner groups no longer have implicit permissions to create API keys, request or grant access, or manage resources at the application instance level. Owner groups can now only create ApplicationGroups.All previous owner group permissions have to be explicitly assigned through ApplicationGroups using the newinstancePermissions field.You’re impacted if
You rely on application owner group members to:- Create or delete application instance API keys
- Request access to other teams’ topics through the Topic Catalog
- Grant or approve access requests to your application’s topics
- Manage service accounts for the application instance
Do you have to do anything?
In most cases, no. On upgrade to Console 1.45.0, an automatic migration creates a mirror ApplicationGroup for each existing application owner group. This mirror group is assigned all instance permissions (applicationInstancePermissionRequestAccess, applicationInstancePermissionGrantAccess, applicationInstancePermissionProposeAccess, applicationInstanceApiKeyManage, serviceAccountManage) so that existing users keep their current access.The mirror group is labeled for identification with the following conventions:- the name is the same as the application name with
-ownerssuffix (e.g. the applicationmy-appwill have a mirror group namedmy-app-owners) - the description starts with
[Default Owner]You can review and adjust these groups after upgrade to restrict specific permissions to specific teams.
instancePermissions field where needed. See the Self-service resource reference for the updated schema.The automatic migration only applies to applications that exist at upgrade time. For new applications created after upgrading, the platform team or application owner has to create an ApplicationGroup with the appropriate
instancePermissions as a first step, otherwise the team will not be able to request or grant access, create API keys, or manage service accounts.Conduktor Console Cortex upgrade
Console 1.45.0 upgrades the bundled Cortex image from 1.18 to 1.21, which includes an upgrade from Prometheus 2.54 to 3.8. This is a one-way upgrade — you cannot roll back to the previous image once data has been written by the new one.You’re impacted if
All deployments running Conduktor Console Cortex are impacted.Pre-upgrade checklist
- Back up TSDB storage. Snapshot your TSDB volume or object storage bucket. This is mandatory — there is no in-place downgrade path.
- Review custom Grafana dashboards. The provided Conduktor Grafana dashboard works without changes, but custom dashboards may need updates due to the PromQL and label changes listed below.
PromQL and query behavior changes
These changes can silently alter query results in custom dashboards, recording rules and alerts:Scraping and ingestion changes
- Targets that don’t return a valid
Content-Typeheader now fail the scrape instead of falling back to the Prometheus text format. If you see scrape failures after upgrading, setfallback_scrape_protocolin your scrape configuration. - UTF-8 metric and label names are now accepted by default. To keep strict pre-upgrade behavior, set
metric_name_validation_scheme: legacy. - Prometheus 3 no longer supports Alertmanager’s v1 API. If your Alertmanager configuration uses
api_version: v1, update to v2 (requires Alertmanager 0.16.0 or later).
Configuration flag changes
The following feature flags have been removed and are now default behavior. Passing them with--enable-feature produces a warning but has no effect:promql-at-modifier, promql-negative-offset, new-service-discovery-manager, expand-external-labels, no-default-scrape-port, agent, remote-write-receiver, auto-gomemlimit, auto-gomaxprocsOf these, no-default-scrape-port may change metric label values — targets like https://example.com/metrics no longer have :443 appended.Other flag changes:remote_writeenable_http2now defaults tofalse. If you depend on HTTP/2 multiplexing for remote write, opt in explicitly.- The log format changed from
go-kit/logtoslog. Anything parsing Cortex logs (for example, Loki recording rules or log-based alerts) needs adjustment.
Cortex-specific changes
- The bucket index is now enabled by default. Disabling it (
-blocks-storage.bucket-store.bucket-index.enabled=false) is not recommended for production. - Ruler API and Alertmanager API flags have graduated from experimental (for example,
-experimental.ruler.enable-apiis now-ruler.enable-api). The old flags still work but are deprecated. - The
-distributor.otlp.enable-type-and-unit-labelsflag is deprecated and replaced by-distributor.enable-type-and-unit-labels. Update your configuration if you use OTLP ingestion.
Disk usage on Kubernetes
In Cortex 1.21, the compactor and cleanup jobs run in parallel rather than sequentially. On large Consoles with significant metric volume, this can cause peak local disk usage to grow enough to fill the pod’s ephemeral storage and trigger eviction.For Kubernetes deployments running large workloads, we recommend attaching a persistent volume to the Cortex pod instead of relying on ephemeral storage, so the compactor has headroom to run alongside cleanup. See Store platform data into a persistent volume in our Helm chart docs for configuration details.New and updated features
Self-service
Granular instance permissions for ApplicationGroups
ApplicationGroups now support a newinstancePermissions field, separate from the existing resource-level permissions field. This lets platform teams delegate application-instance-level actions to specific groups rather than granting them implicitly to all owner group members.Service account management delegation
The newserviceAccountManage instance permission allows platform teams to delegate service account management to specific ApplicationGroups. Previously, service account management was only available to owner group members.UI updates for ApplicationGroup members
The Console UI now checks ApplicationGroup instance permissions when determining access to Self-service actions. ApplicationGroup members with theapplicationInstancePermissionRequestAccess permission can request topic access, and members with applicationInstancePermissionGrantAccess can approve or grant requests directly from the Topic Catalog and Application Catalog pages.Enforce restrictions on ApplicationGroups with a ResourcePolicy
After the migration, application teams own their ApplicationGroups and choose whichpermissions and instancePermissions to assign. Platform teams can keep guardrails on what teams are allowed to grant themselves with a ResourcePolicy of targetKind: ApplicationGroup, linked through spec.policyRef.For example, to enforce GitOps-only approval, restrict ApplicationGroups to a read-only resource permission set and to safe instance permissions — any write operation (topicDelete, topicEditConfig, applicationInstancePermissionGrantAccess, serviceAccountManage) then has to go through the CLI:Unified Chargeback
Chargeback now measures four cost axes — storage, partitions, ingress and egress — across vanilla Kafka, Confluent Cloud and Gateway clusters from a single page:- Three views: group costs by Cluster, Application (with drill-down into application instances) or by the values of a configured label key
- Drill-downs: every row can be expanded to show the topics and service accounts that contributed to its cost
- Chargeback Labels: administrators select which label keys are eligible for grouping (for example,
team,cost-center,env) - Settings drawer: cost rates and Chargeback Labels are managed from a single drawer behind the cog icon, replacing the previous gear flow
- CSV export: the Export dropdown downloads the current view honoring the active filters, view, period and search
AWS Glue schema IaC
Application teams can now manage their Glue schema resources lifecycle through IaC with the addition of the GlueSchema object.Confluent Platform role bindings
Console now supports Confluent Platform Role-Based Access Control (RBAC) role bindings for Self-service. To enable role bindings, go to the Confluent Platform cluster’s provider settings and turn on the role bindings flag.Once enabled, applying a Self-service resource creates Confluent Platform role bindings for the service account instead of Kafka ACLs. Role bindings are also visible in the service account UI for Confluent Platform clusters that have the flag enabled.See the Self-service resource reference for the role bindings created for each resource type, and the Confluent Platform RBAC migration tutorial for step-by-step setup.Subject ACLs for Schema Registry Proxy
Subject ACLs can now be created on application-managed service accounts to control access to specific subjects via the Schema Registry Proxy. This isn’t available on standard ServiceAccount resources, and only takes effect when the service account’s application instance is on a cluster whose Schema Registry is fronted by a Schema Registry Proxy.This provides more granular access control for teams using the Schema Registry Proxy to manage their schemas.Schema Registry Proxy is a preview feature — reach out to your solutions architect for more information.
Fixes
- Added PersonalApiKey audit log type to differentiate from AdminApiKey
- Fixed an error when parsing the Create Connector API response in Kafka Connect 4.2.0+
- Added a detailed cause to deserialization error messages when consuming records
- Fixed a spurious “Subject not found” popup on the record detail view for topics using a Confluent Schema Registry, when deserialization had already succeeded
- Fixed Schema Registry Proxy not syncing subject ACLs to the
_conduktor_srp_commandscommand topic - Fixed the Schema Registry selection on a cluster reverting to “none” after saving
- Fixed the Kafka Connect UI becoming inaccessible when any connector returned a null version in its status response
- Fixed the
list_interceptorsModel Context Protocol (MCP) tool failing when called using a personal access token - Fixed the Resource Access tab showing a blank page for teams with KsqlDB or Connector permissions referencing a cluster that no longer exists
- Fixed topic action menus showing destructive options to users with read-only permissions
- Improved performance of
conduktor applywhen applying anApplicationInstancecontaining many resources
Security advisories
CVE-2026-22016 — Java API for XML Processing (JAXP) component
The Eclipse Temurin JDK 21 base image contains CVE-2026-22016, a vulnerability in the Java API for XML Processing (JAXP) component of Oracle Java SE. Exploitation requires the application to use JAXP APIs to process untrusted XML data. Conduktor products do not process XML through JAXP, so the vulnerability is not exploitable in our deployments.CVE-2026-34282 — Networking component
The Eclipse Temurin JDK 21 base image contains CVE-2026-34282, a vulnerability in the Networking component of Oracle Java SE, allowing a denial of service attack. We will issue patched versions of our products once a fix is available upstream.- Breaking changes
- New features
- Preview features
- Deprecated features
- Coming in v3.20.0
- Quality of life improvements
- Fixes
- Security advisories
Breaking changes
Removed Interceptors
The following Interceptors were deprecated in v3.16.0 and have been removed in this release:Affected Interceptors:io.conduktor.gateway.interceptor.ProduceJsonataPluginio.conduktor.gateway.interceptor.FetchJsonataPluginio.conduktor.gateway.interceptor.FetchEncryptPluginio.conduktor.gateway.interceptor.FetchEncryptSchemaBasedPlugin
Duplicate TLS domain names in the keystore
If the Gateway keystore had two or more private key entries whose certificates mapped to the same hostname (overlapping Subject Alternative Name (SAN) or Common Name (CN)), earlier versions kept one entry and ignored the other without reporting an error. From this release, Gateway rejects that configuration and fails to load TLS contexts. The error identifies the conflicting domain. Remove the duplicate key entry or give each entry distinct SANs or CNs so each hostname maps to one certificate.Default for GATEWAY_ACL_ENABLED changed when no network configuration is set
Without any networking configuration (see details below), GATEWAY_ACL_ENABLED now defaults to false regardless of the security mode inferred from the backing Kafka.
This change is part of the new multi-listener configuration zero-config mode, which enables a quick way for developers to get started with Gateway without needing to set up a full network configuration.
In this zero-config mode, Gateway assumes that ACLs are not needed and disables them by default for simplicity.Setting any of the following environment variables will keep the previous default behavior of GATEWAY_ACL_ENABLED (true for GATEWAY_MANAGED, false for KAFKA_MANAGED), ensuring no breaking changes for most production deployments:GATEWAY_SECURITY_PROTOCOLGATEWAY_PORT_STARTGATEWAY_PORT_COUNTGATEWAY_BIND_HOSTGATEWAY_ADVERTISED_HOSTGATEWAY_ADVERTISED_SNI_PORTGATEWAY_ROUTING_MECHANISMGATEWAY_ADVERTISED_HOST_PREFIXGATEWAY_SNI_HOST_SEPARATORGATEWAY_TENANT_IN_HOSTNAME
New features
HAProxy Protocol support
Gateway now supports HAProxy Protocol if enabled by settingGATEWAY_FEATURE_FLAGS_HAPROXY_PROTOCOL to true.This allows it to know the original client IP address (that was replaced by the external load balancer’s own IP address) and then use it in audit logs and error logs. Load balancers like HA Proxy or Nginx supports this protocol.See the complete explanation about HAProxy Protocol.Plan feature coverage
From v3.19.0, Gateway enforces that the features used by newly configured Interceptors are included in your license. The Admin API returns403 Forbidden when you create or update an Interceptor requiring a feature your license doesn’t include, and the response identifies the feature.Preview features
Topic views
Topic views provide non-materialized views of physical Kafka topics, similar to database views. They apply transformations to records as they’re consumed, without modifying the underlying data. In this tech preview, topic views support SQL-based filtering and projection on schema-less JSON. Topic views are an iteration on the SQL Topic Plugin, which is now deprecated.SQLWHERE clauses can filter on record keys, headers, partition, offset and timestampSee the complete guide to topic views.Topic ID support
The Gateway now supports topic-ID based Kafka protocol handling.Initial coverage is limited to the Fetch API. Previously, ApiVersions negotiation advertised Fetch up to v12 to force topic-name fetches; with this feature enabled, clients can negotiate Fetch v13 or higher. Additional APIs will land behind the same flag in upcoming releases.Opt in by setting feature flag via environment variable:${GATEWAY_FEATURE_FLAGS_TOPIC_ID_SUPPORT=true}.As this is a preview feature, we recommend enabling it only in non production environments.Multi-listener updates
This release changes the behavior of the multi-listener configuration (preview):GATEWAY_ACL_ENABLEDis now required, alongsideGATEWAY_SECURITY_MODE. Set it totrueorfalse(typicallytrueforGATEWAY_MANAGED,falseforKAFKA_MANAGED).- Per-listener SSL client authentication: each listener can now have its own mTLS client authentication policy, set via
GATEWAY_LISTENER_<NAME>_SSL_CLIENT_AUTH. The globalGATEWAY_SSL_CLIENT_AUTHenvironment variable is ignored in multi-listener configuration.
Deprecated features
Virtual SQL Topic Plugin
Deprecated in:v3.19.0
Planned removal: v3.22.0
Full plugin name: io.conduktor.gateway.interceptor.VirtualSqlTopicPluginTopic views (tech preview) provide an SQL transformation option which will provide all of the functionality of the SQL Topic Plugin.
Coming in v3.20.0
Internal Kafka client upgrade. Gateway v3.20.0 will upgrade the internal Apache Kafka client from version 3.9 to version 4.0 or later. The upgrade drops support for early versions of some Kafka protocol API keys, but does not change the minimum Kafka broker version that Gateway supports. The change is expected to have low impact for most deployments.Quality of life improvements
Faster bulk Interceptor apply
Bulk Interceptor configuration updates throughconduktor apply and the Admin API are up to 10x faster with lower CPU use than on v3.18.x when you apply many Interceptors in sequence. Simplified Docker image build
The Gateway Docker image is now built from a singleDockerfile, replacing the previous three-stage Maven/Jib pipeline. The runtime entrypoint and HEALTHCHECK behavior are unchanged.If you extend the Gateway image in your own Dockerfile (for example, FROM conduktor/conduktor-gateway:3.18), verify your custom build against 3.19.0, as the internal image layer structure differs from previous releases.Fixes
- The
/metricsendpoint no longer issues blockinglistTopicscalls during scrapes, which could stall the HTTP event loop and cause health-check timeouts in constrained environments.
Security advisories
CVE-2026-22016 — Java API for XML Processing (JAXP) component
The Eclipse Temurin JDK 21 base image contains CVE-2026-22016, a vulnerability in the Java API for XML Processing (JAXP) component of Oracle Java SE. Exploitation requires the application to use JAXP APIs to process untrusted XML data. Conduktor products do not process XML through JAXP, so the vulnerability is not exploitable in our deployments.CVE-2026-34282 — Networking component
The Eclipse Temurin JDK 21 base image contains CVE-2026-34282, a vulnerability in the Networking component of Oracle Java SE, allowing a denial of service attack. We will issue patched versions of our products once a fix is available upstream.Fixes v1.44.1
- Fixed a bug where changing an ApplicationInstance resource’s ownership mode deleted ACLs for the ApplicationInstance’s service account. All customers using Self-service with limited ownership mode should upgrade to this patch release immediately.
- Fixed an authentication issue that caused auto-restart jobs to fail for Connectors created using specific authentication mechanisms.
Breaking changes v1.44.0
Minimum Gateway version v1.44.0
Console 1.44.0 has migrated from Gateway v1 APIs to v2 APIs. This requires Gateway 3.12.0 or later.You’re impacted if
You are running a Gateway version older than 3.12.0 alongside Console.Do you have to do anything?
Upgrade Gateway to 3.12.0 or later before upgrading to Console 1.44.0.Gateway v1 API support will be removed in an upcoming Gateway release. Console versions prior to 1.44.0 will not be compatible with that Gateway release - upgrade Console first.New and updated features v1.44.0
Self-service v1.44.0
Topic prefix support
Self-service now supports requesting and granting access to topic prefixes through the Console UI. This feature enables teams to manage permissions for multiple topics that share a common prefix, streamlining access management for applications that work with groups of related topics.To use this feature, navigate to Application Catalog > Application > select the Application Instance you want to request access from > Ownership section of the Application Instance. From there, you can request access to topic prefixes in addition to individual topics.Transactional ID resources
Self-service now supports TRANSACTIONAL_ID resources for ApplicationInstances and application-managed service accounts, enabling teams to manage transactional IDs as part of their application resources.TRANSACTIONAL_ID resources support the standard ACL operations (Write and Describe). For Confluent Cloud clusters with role bindings enabled, DeveloperRead and DeveloperWrite role bindings are automatically created.This enhancement allows applications using transactional Kafka producers to provision and manage their transactional IDs through Self-service. See the Self-service reference documentation for configuration examples.Insights v1.44.0
RBAC Aware
Insights are now available for all teams using Console. Access is based on the RBAC setup, a user can see insights for the topics where they have permission to view or edit the topic configuration.Focus and Filtering
To provide a more focussed experience when viewing Insights the views have been expanded out into dedicated pages for risks, costs and VIP topics. Across all of these areas the ability to filter the information shown has also been extended, with each view now being filterable by topic name patterns and by the Self-service application owning the resources.These changes allow specific areas of interest of ownership to be analysed, while still providing a high level overview of system health.Quality of life improvements v1.44.0
- Support for Confluent Platform proprietary topic configuration keys when creating topics through the UI and CLI for clusters configured with Confluent Platform as the provider.
- Optimized subject search to be more efficient.
- Added a Bytes as text toggle in topic message details to decode base64-encoded bytes fields as readable UTF-8 text.
- Platform teams can now configure a default number of partitions for topic creation, and custom URLs for the Support and Feedback links in Console. See UI settings properties for details.
Fixes v1.44.0
- Producing Protobuf messages no longer fails when schema references have path-like subject names (e.g.,
org/conduktor/test/schema.proto). - CSV import now detects the topic’s schema format (Avro, JSON Schema, Protobuf) and pre-selects the matching serializer, instead of defaulting to String/JSON.
- Fixed consumer group lag being incorrectly reported as a negative value.
- Fixed consumer group indexing timeout on large clusters when multiple groups share the same topic-partition.
- Fixed an out-of-memory error when indexing clusters with 100K+ consumer group assignments while handling concurrent API requests.
- Fixed message reprocess issue when the payload is large.
- Fixed message reprocess issue when the payload contains NaN value.
- Fixed an issue with schema actions menu being hidden when the schema is in indexing state.
- Fixed scroll bar overlap in the Produce Message panel when all sections are expanded.
- Fixed LDAP authentication failing when group mappings are configured (regression in 1.43.0).
- Fixed Confluent Cloud metrics indexing failing when the telemetry API is accessed through an outbound proxy.
- Fixed Kafka Connect returning 400 errors when accessed through AWS load balancers due to HTTP/2 upgrade headers.
- Fixed message reprocessing failing for Avro messages with timestamp logical types.
Breaking changes v3.18.0
License key required to start Gateway
From v3.18.0, Gateway will only start if a valid license is provided. If you’re already using a license, no changes are required.If you’d like to trial Gateway, contact us.Once you’ve migrated to Gateway v3.18.0, you can remove the license topic_conduktor_gateway_license or _conduktor_${GATEWAY_CLUSTER_ID}_license from your Kafka cluster.Removed external storage option from encryption interceptor
The deprecatedexternalStorage configuration parameter has been removed from encryption Interceptors (EncryptPlugin, FetchEncryptPlugin, EncryptSchemaBasedPlugin, FetchEncryptSchemaBasedPlugin).Impact:- Interceptor configurations containing
externalStorage: truewill fail to load - Messages encrypted with external storage mode cannot be decrypted after upgrading
- The
GATEWAY_ENCRYPTION_CONFIGS_TOPICenvironment variable is no longer used - The
_conduktor_gateway_encryption_configsKafka topic is no longer managed by Gateway
externalStorage: true.If you haven’t migrated yet
Messages encrypted with external storage mode can’t be decrypted after upgrading to v3.18.0.You should:- either downgrade to a version before 3.18.0, decrypt affected data and then re-encrypt using the default header-based storage before upgrading;
- or accept that previously encrypted data using the external storage will no longer be decryptable.
- Remove the
externalStoragefield from your Interceptor configurations. - Optionally delete the orphaned
_conduktor_gateway_encryption_configstopic. Find out more about encryption configuration.
New features v3.18.0
Multiple listeners (preview)
Gateway now supports multiple listeners, allowing you to expose different network endpoints with independent security protocols, routing strategies and network bindings. This is a preview feature and is subject to change.Configure listeners using the newGATEWAY_LISTENER_<NAME>_* environment variables:Message integrity Interceptor
The message integrity Interceptor lets you sign Kafka records on produce and verify them on fetch so consumers can detect if a record was modified after it was produced. Two plugins work together: ProduceIntegrityPolicyPlugin (signs with HMAC-SHA256 via Tink) and FetchIntegrityPolicyPlugin (verifies and drops or allows records by policy). Signing keys are stored in HashiCorp Vault KV v2 and cached locally; credentials are taken from the Interceptor config (including${VAR} placeholders).See Data security for configuration, Vault auth types, and key setup.Deprecated features v3.18.0
Gateway metrics deprecated in v3.18.0
The following three metrics are being deprecated in v3.18.0 and we plan to remove them completely in v3.21.0:gateway_upstream_connections_downstream
Does this affect me?
Yes, if you’re using this metric. Check your Grafana dashboards and alerting rules for references to it.If you have any:- remove all references to the metric.
- replace them with
gateway_active_connections_vclusterto monitor active connections per Virtual Cluster.
Large batch handling plugin
Deprecated in:v3.18.0
Planned removal: v3.21.0
Affected Interceptors:io.conduktor.gateway.interceptor.LargeBatchHandlingPlugin
Fixes v3.18.0
- Improved the masking of secrets across the codebase in case they are ever serialized in logs in the future.
- Fixed the OpenAPI specification, so
UpsertResultenum values are correctly defined as strings, not empty object types. - Added a timeout to
await()operations during shutdown to prevent the process from hanging indefinitely. - Changed the readiness probe to fail during shutdown to prevent the pod from receiving traffic.
- Fixed an issue where TLS connections mid-handshake were not closed properly during shutdown.
- Fixed an issue where the Vault connection intermittently reported an
invalid tokenerror. - Large message Interceptor: added disableChecksums option in S3 config for S3-compatible storage (MinIO, NetApp ONTAP). When set to true, the SDK uses a checksum format that these backends accept. Otherwise, the uploads can fail because the default checksum is not accepted. Find out more about configuring S3.
- Fixed a bug in the ReadOnlyTopic safeguard policy THROTTLE action.
- Improved performance of Gateway when field-level encryption is configured by doing encryption work on separate thread pool.
- Improved performance of field-level encryption by processing partitions in parallel.
- Fixed default Docker healthcheck (e.g. Docker Compose environments).
- Optimized the keep alive re-auth of Fortanix KMS connections with a dynamic refresh mechanism and use of the
refresh()API call. - Gateway’s Vert.x-based admin API server now explicitly disables HTTP/2 cleartext upgrades on the admin API listener and responds over HTTP/1.1
- Conduktor Scale:
- Quality of life improvements
- Fixes
- Upcoming changes: deprecation notice for Self-service topic policies
Conduktor Scale
Community Edition
We’ve overhauled our free license. If you’re currently using it, the changes will only be applied when you upgrade to Console v1.43.0.Find out more about the Community Edition.Quality of life improvements v1.43.0
- Added support for Boolean, Short, Int and UUID format types when producing and consuming topic messages.
- Kafka Connect UI now enforces RBAC permissions and hides actions the user is not permitted to perform.
- Moved the MCP navigation link to the Settings page to reduce the number of items in the main menu.
- Added support for managing Kafka Connect connector resource policies in the UI.
- Improved the Topic consume page to return more explicit errors and to include a retry option.
- Added a new
Kafka.ConsumerGroup.Createevent type that tracks consumer group creation events in the audit log. - Added a public API endpoint to manage Kafka Connect connectors’ auto-restart.
Fixes v1.43.0
- The Request access button in the Topic Catalog is now disabled when the user doesn’t own any applications.
- After deleting a cluster, the deletion dialog now closes and cluster list is refreshed.
- Alert history now shows correct time ranges for 1D/7D/30D views and accurate tooltip dates spanning midnight.
- The Reset Offset and Add Partitions drawers now stay open as expected on Firefox ESR.
- The
CDK_DATAPOLICY_DISABLEKEYMASKINGsetting now correctly disables key masking in data policies. - Exporting large topic messages (over 100 KB) now includes the full message content instead of empty values.
- Connector auto-restart settings are no longer unexpectedly disabled when connectors are temporarily unavailable.
Upcoming deprecation notice v1.43.0
Self-service topic policies will be deprecated in Console v1.46.0. We recommend that you convert all your existing topic policies to resource policies as soon as possible. The resource policies have feature parity with the legacy topic policies.Use the Console UI to do this easily: go to Settings > Policies migration.- Conduktor Scale:
- Quality of life improvements
- Fixes
Conduktor Scale
Chargeback without Gateway
This Console version introduces new Chargeback capabilities that do not require Gateway. Metrics and costs can be viewed by application, application instance and topic.Find out more about Chargeback without Gateway.Insights filtering and sorting
The Insights dashboard now offers enhanced filtering, sorting and search capabilities:- Global filtering - filter all Insights data by label or topic type (internal, streams, user). Click any label in a table to apply it as a filter.
- Sorting and searching - tables in risk analysis, VIP topics and governance sections now support column sorting and search.
- Topic classification - topic type labels are now shown alongside custom labels for easier identification.
- Filtered exports - when filters are applied, exported CSV files include a -filtered suffix and contain only the filtered data.
Cluster wide resource policies
Platform teams can now enforce resource policies at the cluster level, ensuring that all your Kafka resources follow the best practices across the entire platform.With cluster-wide policies, you can set standards across all the resources for replication factor, minimum in-sync replicas, schema restrictions and much more, without having to specify them individually for each application.New resource policies page
The new Resource policies page replaces the Topic Policies page and provides a centralized view of all the policies with enhanced filtering and navigation.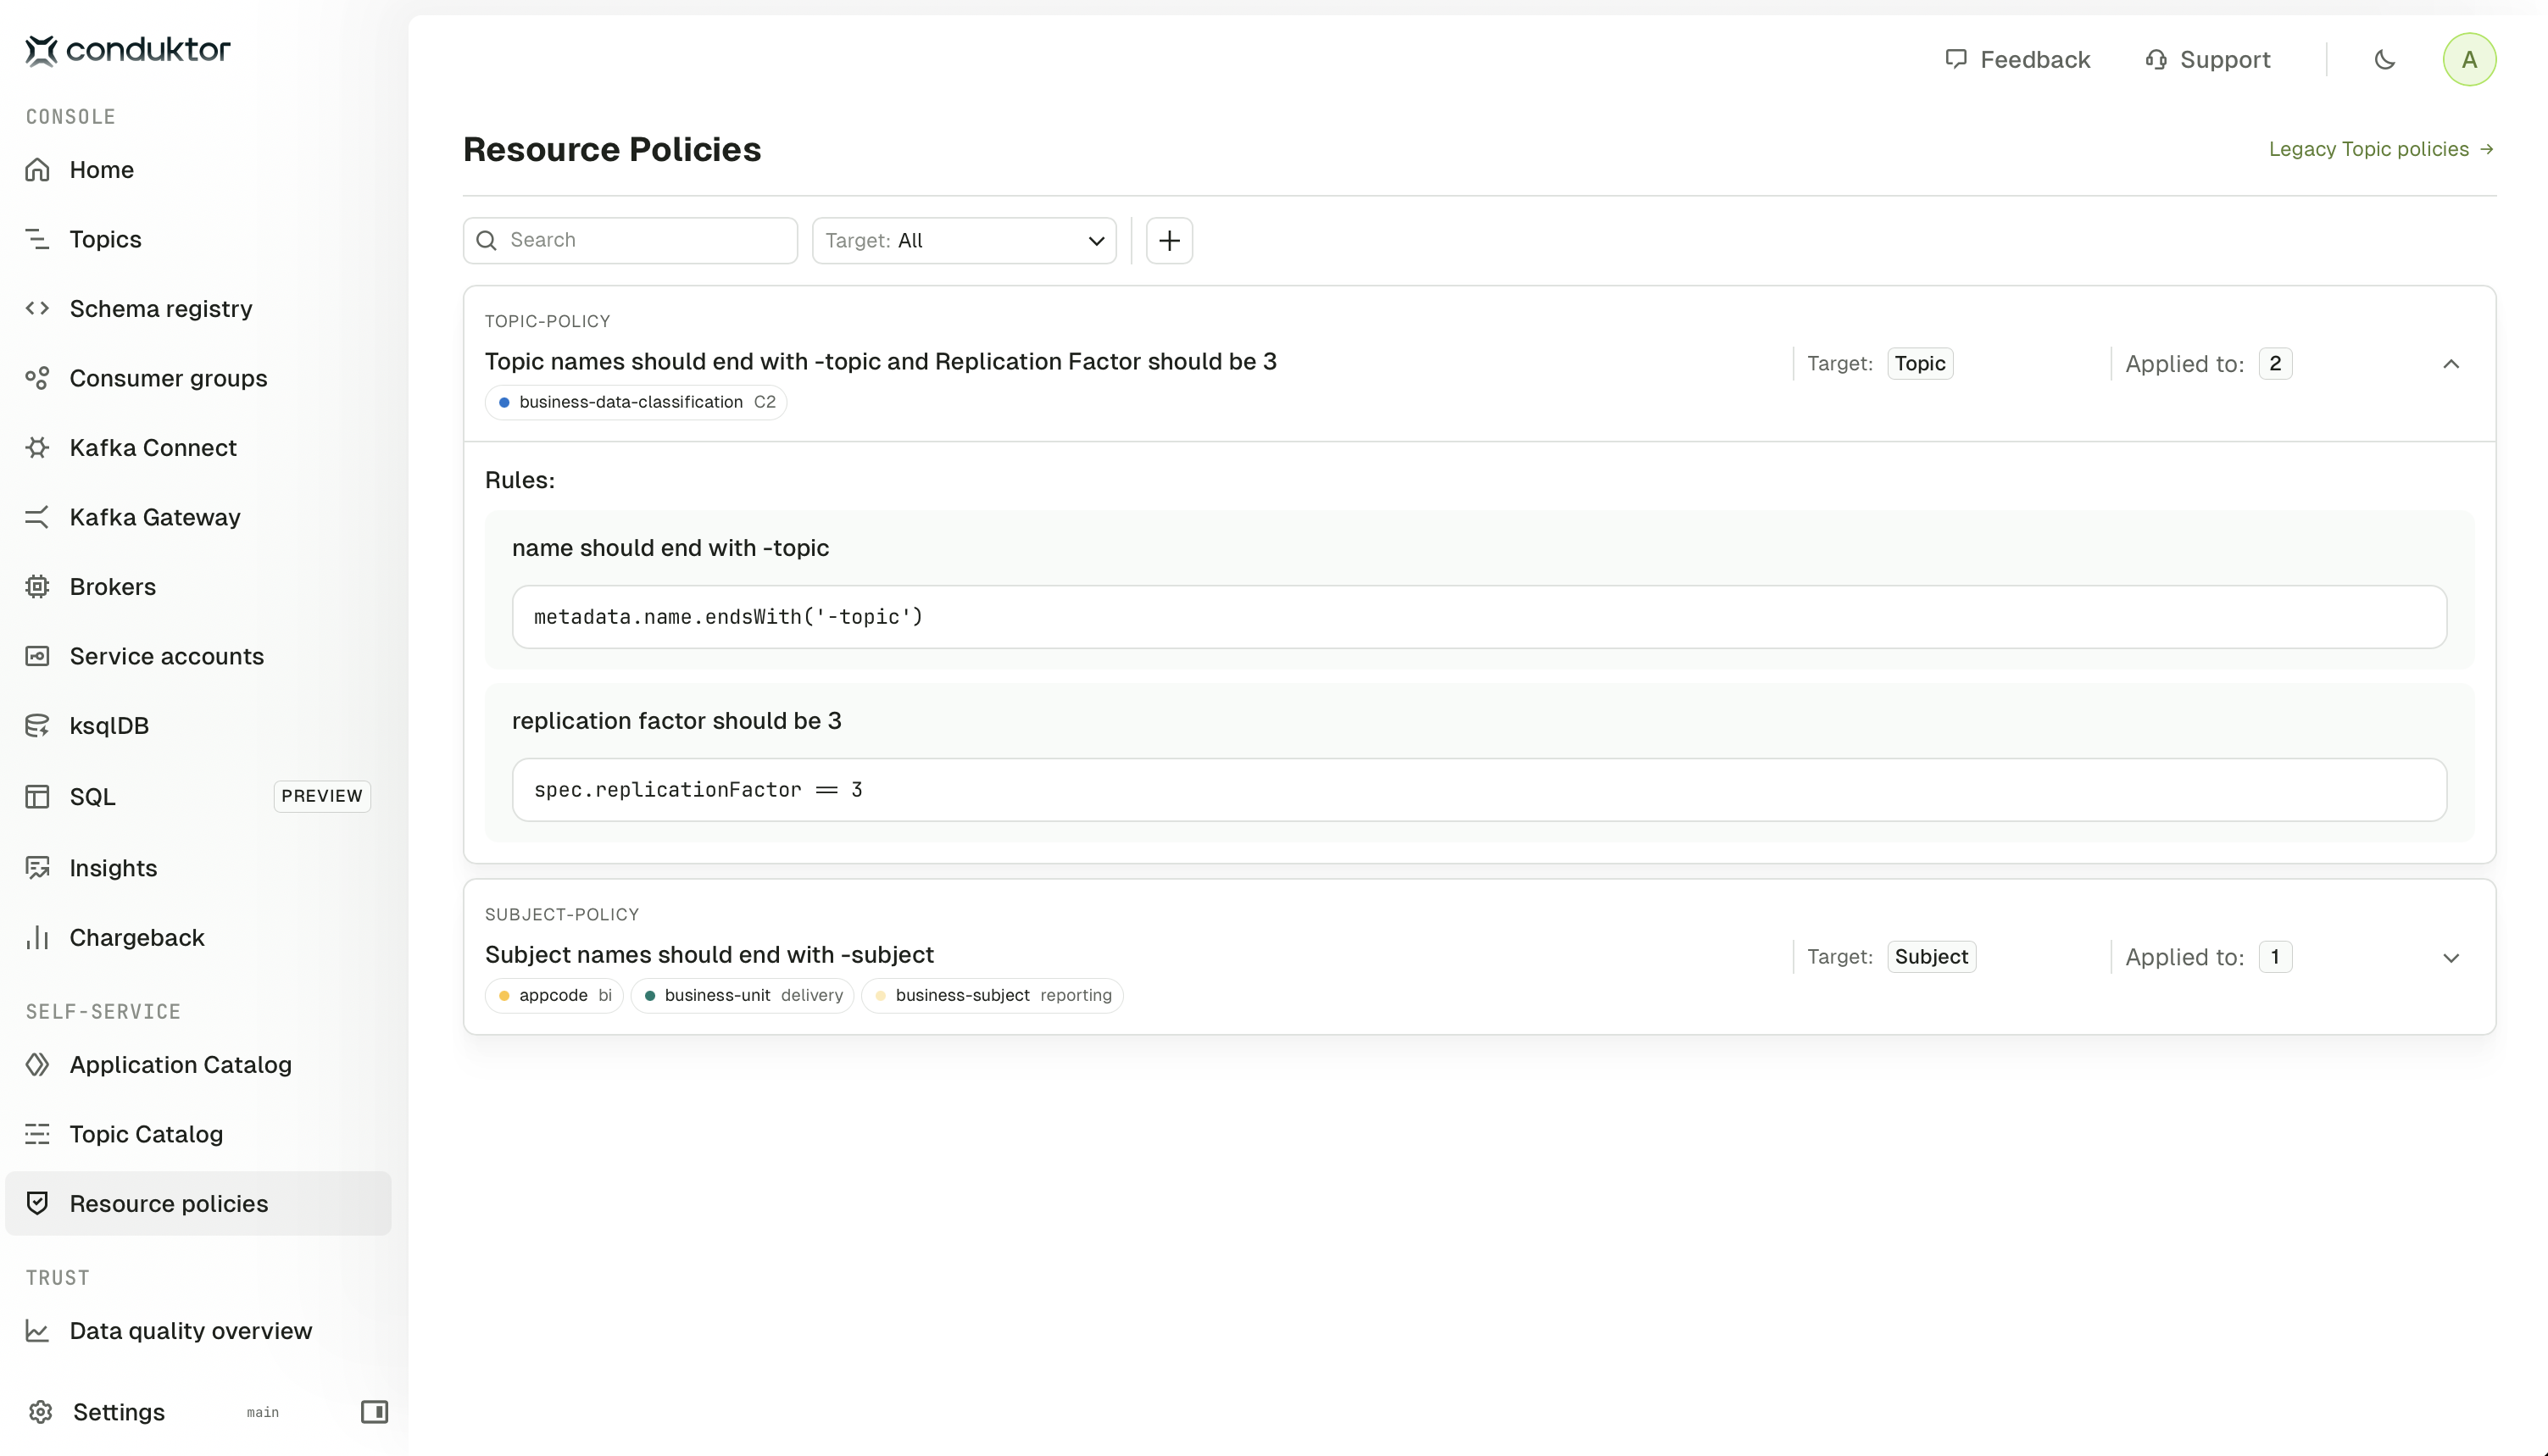
Quality of life improvements v1.42.0
- Added support for optional basic auth for the metric scraping endpoints (
/api/monitoring/metricsand/monitoring/metrics/). To configure, useCDK_MONITORING_BASICAUTH_EMAILandCDK_MONITORING_BASICAUTH_PASSWORD. Find out more. - Sensitive information such as passwords, tokens, keys and secrets are now redacted in audit logs.
- Made a number of visual improvements to the topic consume message drawer
- Added support for environment variables in webhook alert configurations, allowing secrets to be injected securely using
{{env.*}}syntax (for environment variables prefixed withCDK_WEBHOOK_, with the prefix stripped). - Added basic authentication support for outbound Prometheus/Cortex/Mimir queries via the
monitoring.prometheus-authconfiguration. - Added a new consumer value format
SchemaRegistryto prevent a poison pill when the first record(s) are not in the expected format. - Refactored topic indexing to reduce memory consumption and remove hard-coded timeout for retrieving offsets.
- Refactored consumer group indexing to reduce the number of queries to the database.
- Cluster selection menu moved to the top of the page for better user experience.
Fixes v1.42.0
- Fixed Reset Topics functionality for some Kafka Connect servers where topics weren’t being correctly refreshed.
- Fixed a bug where identity providers for Confluent Cloud weren’t displaying all known identity providers in the Service Accounts UI.
- Fixed override of
CDK_GLOBAL_JAVA_OPTSenvironment variable that was not working as expected. - Fixed an error that occurred when Confluent CLI applied new subject with
--dry-run. - Fixed the group v2 API to include ksqlDB permissions in the response.
- Fixed performance regression on the group v2 API
- Exporting large topic messages no longer results in empty values for truncated data.
- Improved login performance for LDAP users with many groups.
- Changed the topic list implementation to query the database instead of kafka, allowing a much faster response.
- The logical connector ID is now displayed for Confluent Cloud managed connectors.
- Fixed ksqlDB custom headers not being applied, which prevented combining mTLS authentication with Basic Auth headers.
- Fixed AWS Glue schema ID display in consumed messages - UUID-based schema IDs are now handled correctly without causing errors.
- Added configuration of PKCE method for better support of OIDC providers.
- New features
- Deprecated features:
- Fixes
- Quality of life improvements
New features
Support for Vault Transform Secrets Engine
Gateway’s encryption/decryption Interceptors now support the Vault Transform Secrets Engine in addition to the default Transit Secrets Engine.This means that Gateway now provides an alternative method for protecting sensitive data in Kafka messages: tokenization and format-preserving encryption:- tokenization: sensitive data is replaced with tokens that are deterministically generated when the same key is used, while also storing the original values securely in HashiCorp Vault’s transform secrets engine.
- format-preserving encryption: data is still encrypted but the format and length of the original field data is preserved.
EncryptPlugin, DecryptPlugin, etc.).Simply specify a vault-transform:// prefix in your keySecretId (e.g. vault-transform://my-role).Find out more about Vault KMS configuration.Low level network configuration
Added the ability to customize some of the low level network configuration.Deprecated features v3.17.0
Filtering topics with CEL
Deprecated in:v3.17.0
Planned removal: v3.20.0
Full plugin name: - io.conduktor.gateway.interceptor.CelTopicPluginTopic views (tech preview) provide an will provide a CEL transformation option in a future release which will provide all of the functionality of the CEL Topic Plugin.
Fixes v3.17.0
- If Confluent Cloud Principal Resolver is configured, the Confluent Cloud API Secret is now masked.
- Fixed a bug causing duplicate broker connections and incorrect client disconnections.
- Fixed FindCoordinator to preserve all Kafka error codes instead of incorrectly converting them to
COORDINATOR_NOT_AVAILABLE, ensuring clients receive accurate error information from Kafka. - Fixed Fetch v16 response handling to prevent invalid MessageSetSize errors
Quality of life improvements v3.17.0
- General improvements to log messages for better readability and clarity.
- Adjusted log level for better operational visibility.
- Breaking changes
- Conduktor Scale:
- Conduktor Shield
- Conduktor Trust
- Quality of life improvements
- Fixes
Breaking changes v1.41.0
If you currently use Chargeback, please note that we have folded this into a broader Chargeback feature, including costs based on topic storage and partitions. To continue to use the existing feature you will need to set an environment variable, documented here.This will also enable the new Chargeback functionality that does not depend upon Gateway.Conduktor Scale
MCP server
Preview functionality: This is currently a preview feature and is subject to change as we continue working on it.
Chargeback without Gateway
This Console version introduces Chargeback for storage and partitions which allows tracking of byte and partition usage across clusters.It works directly with Console’s metadata indexer - there’s no need to set up or maintain Gateway.You can:- track costs based on storage consumption (byte-hours) and partition counts (partition-hours) per topic,
- view costs aggregated by day or month, with percentage attribution showing each cluster’s contribution to total spend,
- set cost rates per cluster for both storage and partitions,
- see overall costs, storage-only costs, or partition-only costs.
Configurable context path
Console now supports context path configuration for deployments such ashttps://company.com/conduktor. This is especially useful for restricted Kubernetes environments with ingress controllers. Find out how to deploy with a context path.Key masking in data policies can be disabled
Data masking policies for keys that are not JSON or schema-based can be disabled.Find out about data policy properties.Conduktor Trust
Added onboarding banners to the Rules and Policies pages to help users get started with data quality.The banners will disappear as soon as you create your first Rule or Policy.Find out about data quality.Quality of life improvements v1.41.0
- Refactored topic and consumer group indexing tasks to reduce load on Kafka clusters and improve CPU and memory usage. Timeouts may need to be adjusted to align with the updated duration of these indexing tasks.
- Added usage data to help admins track Console usage and monitor license utilization. Admins can view active users, see Self-service applications and instances, access requests, view total Partner Zones and shared topics across three time periods: last 30 days, current month and the last 12 months. This feature includes a monthly trends graph and CSV export for offline analysis. Historical data builds up over time as Console collects usage metrics. Find out more about usage data.
- The consumer group offset lag graph previously displayed the max offset lag value, but has been adjusted to display the sum value to correspond with its alerting behaviour.
Fixes v1.41.0
- Resolved IO exceptions that were happening for customers with long-running queries.
- Improved performance of Insights data collection by 2-3x through various optimizations, reducing resource usage and speeding up metrics gathering.
- Adjusted default Insights refresh frequency from 5 minutes to 15 minutes, freeing up system resources.
- ksqlDB server configuration now accepts the authorization HTTP header, allowing you to use both SSL and basic authentication.
- Added configuration option to disable data masking on record keys, allowing you to see and filter by keys that are not structured data.
- Self-service RBAC operations now happen in a single transaction, preventing incomplete object creation when deploying via CI/CD.
- Conduktor CLI dry-run mode now correctly reports
NotChangedwhen there are no actual changes to Self-service application resources.
- Breaking changes:
- New features:
- Deprecated features:
- Fixes
Breaking changes
The metric gateway_license_remaining_days is now a positive number
If you have set up any alerts on the metric gateway_license_remaining_days in your own monitoring stack, please check them prior to this release.
The metric was incorrectly reporting a negative number when time remained on the license, and this has now been corrected.New features
New v2 APIs for clusters
The v2 API now supports cluster switching operations and retrieving physical cluster connection configurations.A new endpointv2/cluster-switching/check is available to check which physical cluster is currently active (main or failover).Check out the Gateway v2 API reference for more details.Support for Fortanix KMS
Gateway now supports field-level and full payload encryption/decryption using Fortanix Data Security Manager (DSM) as the Key Management Service (KMS). This integration enables secure encryption of Kafka messages with keys managed by Fortanix. Find out how to configure Fortanix KMS.Deprecated features v3.16.0
Fetch encryption Interceptors
Deprecated in:v3.16.0
Planned removal: v3.19.0
Affected Interceptors:io.conduktor.gateway.interceptor.FetchEncryptPluginio.conduktor.gateway.interceptor.FetchEncryptSchemaBasedPlugin
JSONata transformer Interceptors
Deprecated in:v3.16.0
Planned removal: v3.19.0
Affected Interceptors:io.conduktor.gateway.interceptor.FetchJsonataPluginio.conduktor.gateway.interceptor.ProduceJsonataPlugin
The GATEWAY_INTERCEPTOR_CONFIG_LOCATION environment variable
Deprecated in:v3.16.0
Planned removal: v3.19.0This variable allowed users to configure global Interceptors by pointing to a configuration file location.We recommend using Gitops tooling instead.Delegated security modes
Deprecated in:v3.10.0
Planned removal: v3.19.0We’ll remove support for delegated security modes in v3.19.0. Currently, we support backwards compatibility for configurations using DELEGATED_XXX environment variables.If you’re still using these, you should migrate to the GATEWAY_SECURITY_MODE. Check out the migration guide.Fixes v3.16.0
- The metric
gateway_license_remaining_daysis now a positive number when there is time remaining on the license, instead of negative. - Gateway now preserves upstream Kafka errors in metadata responses instead of unconditionally overwriting them with unknown topic errors, allowing clients to see the actual error from Kafka.
- Data masking now gracefully skips records with full payload encryption headers, preventing errors when both Interceptors are applied to the same topic. This applies when using header-based encryption storage (
externalStorage: falsewhich is the default).
Rebuilt with the Go 1.25.12 toolchain.Find out more.
Rebuilt with the Go 1.25.7 toolchain.Find out more.
run covers the Console topic API, and the AWS SDK used for remote state storage is up to date.Find out more.run covers the Console consumer group and Kafka Connect connector APIs, and template fetches the templates Console holds.Find out more.version reports the correct version number and commit hash, and the released binaries are statically linked.Find out more.State management for the resources the CLI manages,
--dry-run on delete and the -v and -vv verbosity levels.Breaking change: the Go packages moved. This affects only projects that import the CLI as a Go library. The commands and flags are unchanged.Find out more.New
edit command, and apply shows a diff for the resource kinds that support it, such as ServiceAccount.Find out more.apply accepts --recursive, the bundled resource schema covers the Console 1.36 resources and delete no longer sends an empty scope for an Interceptor that has no metadata.scope.Find out more.Fixes
- Fixed an issue introduced in
v0.6.0, where intermittent failure on some apply runs where kind ordering would not be respected. In some scenarios the parent resource is not made before the child (e.g. ApplicationInstances being created before Applications) and the run would fail, this could be fixed by attempting a retry. - Fixed an issue introduced in
v0.6.0where failed runs would not return an exit code, leading to silent failures in CI actions.
Changes
This release introduced a couple of bugs that were fixed in CLI v0.6.1, please use that version instead of v0.6.0.
apply operations, use the --parallelism flag.The flag accepts integer values between 1 and 100. If a value outside this range is provided, the command will show an error and exit. Find out more.Change
- The -o flags are now visible at the get root command level, making output options more discoverable.
Fix
- Fixed an issue where alerts could not be deleted via the CLI when using the metadata group. Find out more.
Changes
- Included Gateway resources in
get all - Added cause to ApiError responses
- Fixed apply template comment in YAML file
- Added option to edit and apply immediately to template command
- Standardized flag descriptions
Fix
- Fixed verbose mode in single client configuration
Changes
- Environment variable references can now be passed to Gateway or Console, allowing you to store references to secret variables used by the host within your configuration.
- Partner Zones are now available, allowing you to securely share your streaming Kafka data with external partners without the need to replicate the data.
- More informative error responses in certain situations
- Console API schema updated
- Added
run - Schema code reorg
- Ops 630 pass external environment variable reference
- Introduced dev mode for hidden command
- Panic replaced with graceful exit
- Included Partner Zones Gateway API changes
Fixes
- buildAlias duplication fixed
- Fixed ServiceAccount check when defining commands
- Release Action fixed
- Various doc fixes
- Fixed duplicate printout statements
Changes
- Added support for
-o jsonand-o nameonget - Updated to latest Gateway API
- Added support for Gateway API v2
- Clarified version with a
v
Fixes
- Fixed the release tag
- Fixed missing key retrieval from environment
Changes
- Made
/apinot mandatory when setting base URL - Updated offline schema for future
- Added support for description from file in topic resources
- Added support for
delete -f - Improved client interface
- Improved CLI API for terraform provider POC
- Added a command to create token
- Added a login command
Fix
- Fixed auto login in client
Features
- This release is only compatible with Console 1.23 or above
- Made CTL work with complex path
- Set CDK-CLIENT header to improve analytics
Fixes
- Fix for adding
prefix X-to custom header
Conduktor CLI allows you to perform operations directly from your command line or a CI/CD pipeline to a Conduktor Console instance.
Features
- Support for
get,apply(upsert) anddeletecommands for the following Conduktor Console resources:- Application
- ApplicationInstance
- ApplicationInstancePermission
- Support for
--dry-runonapplyanddelete - Support
completionthat generates the autocompletion script for the specified shell - Support for proxy auth using certificate and key
- Support
ignoreuntrusted certificates environment variable - Configurable environment variables